One live register for every security risk
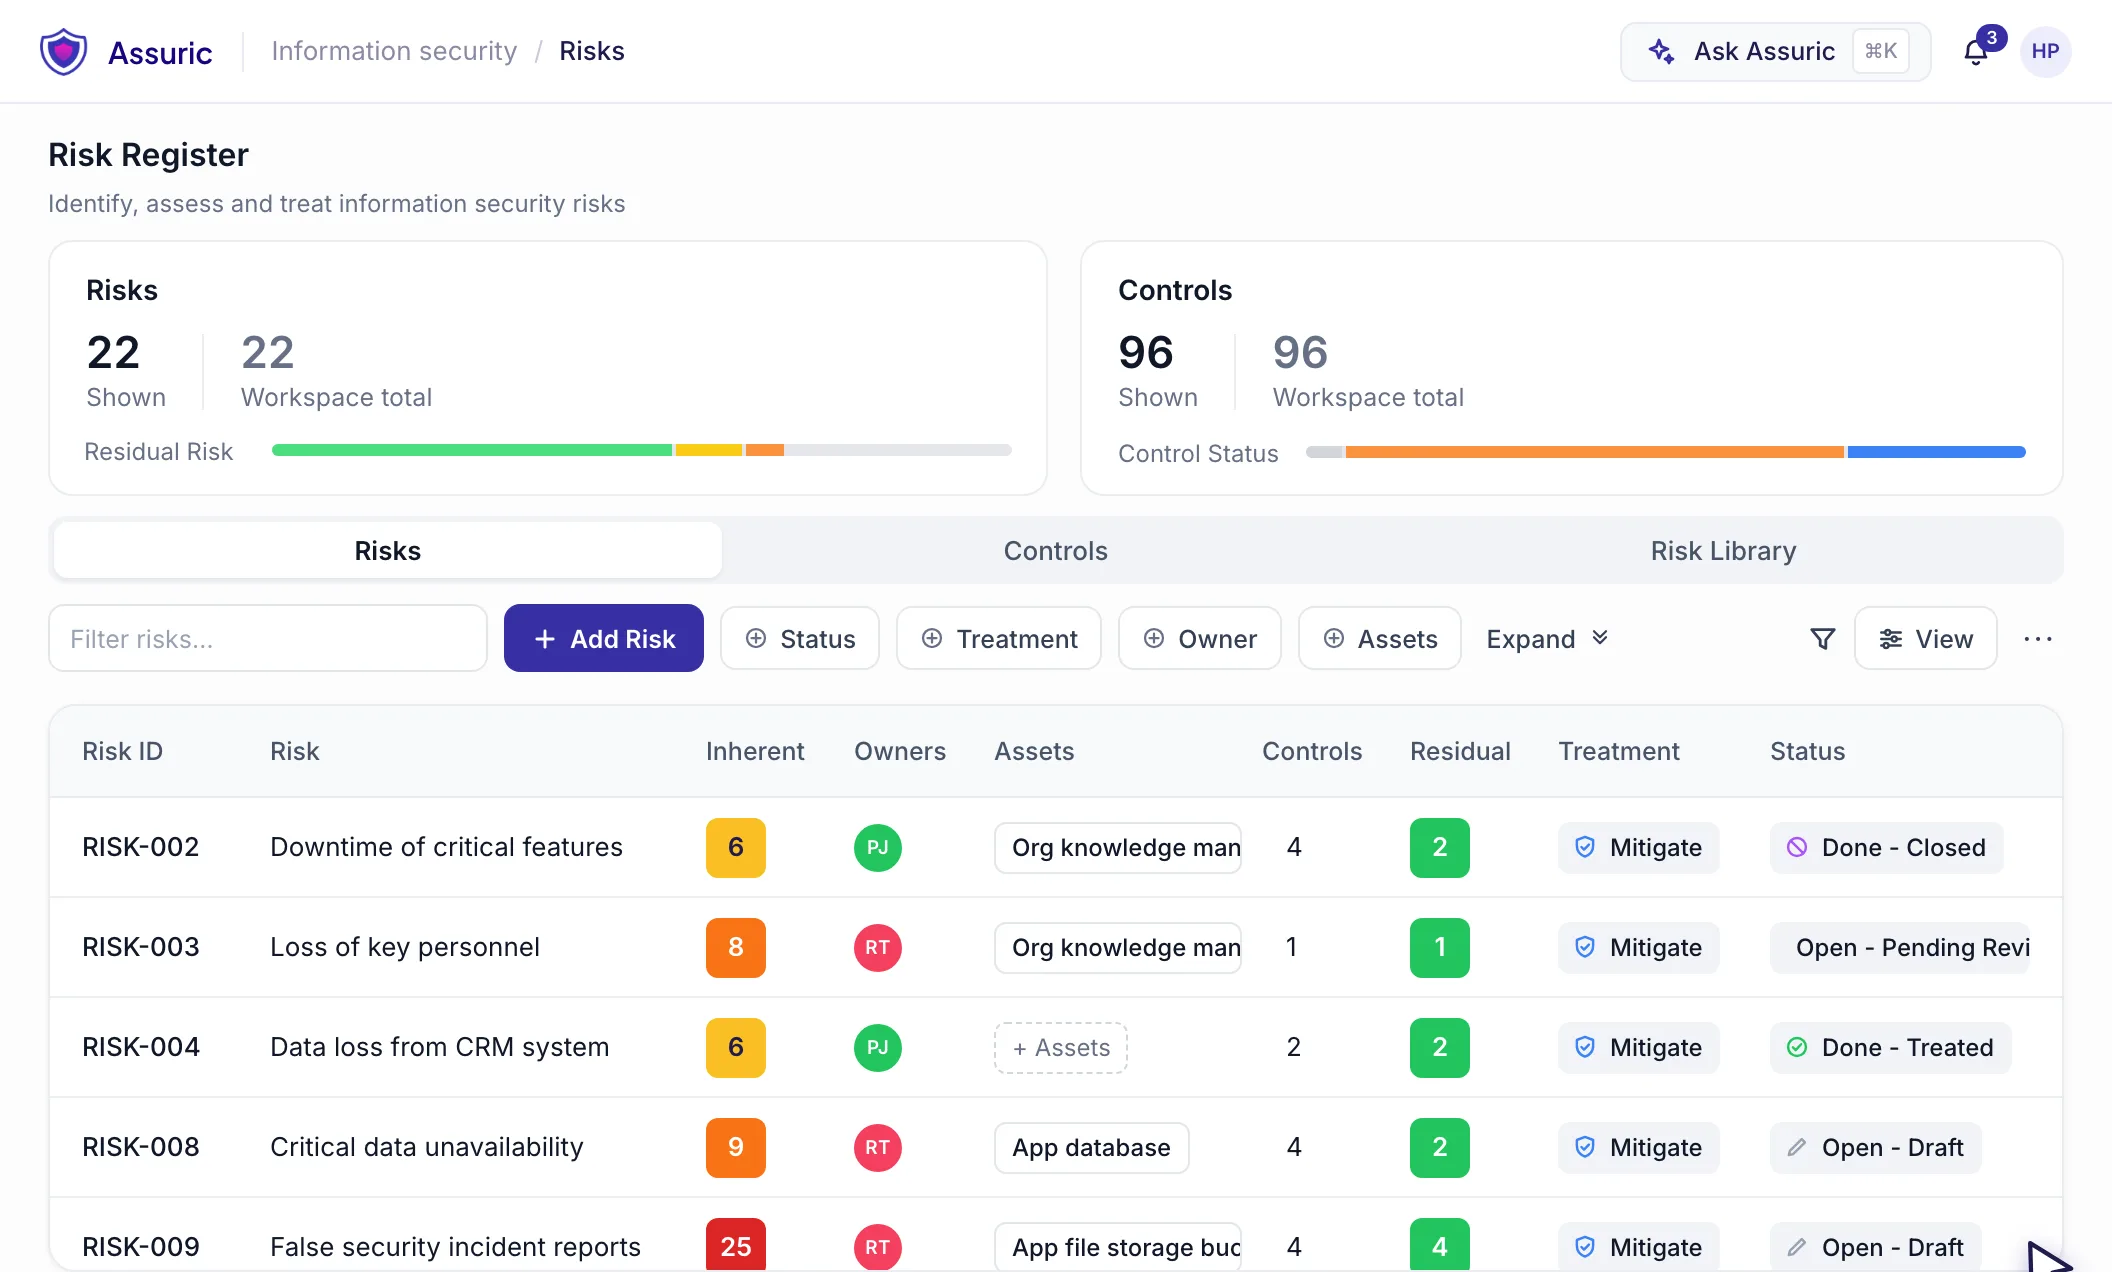
Record each risk with its category, owner and affected assets, and track it from identification through to treatment or closure.
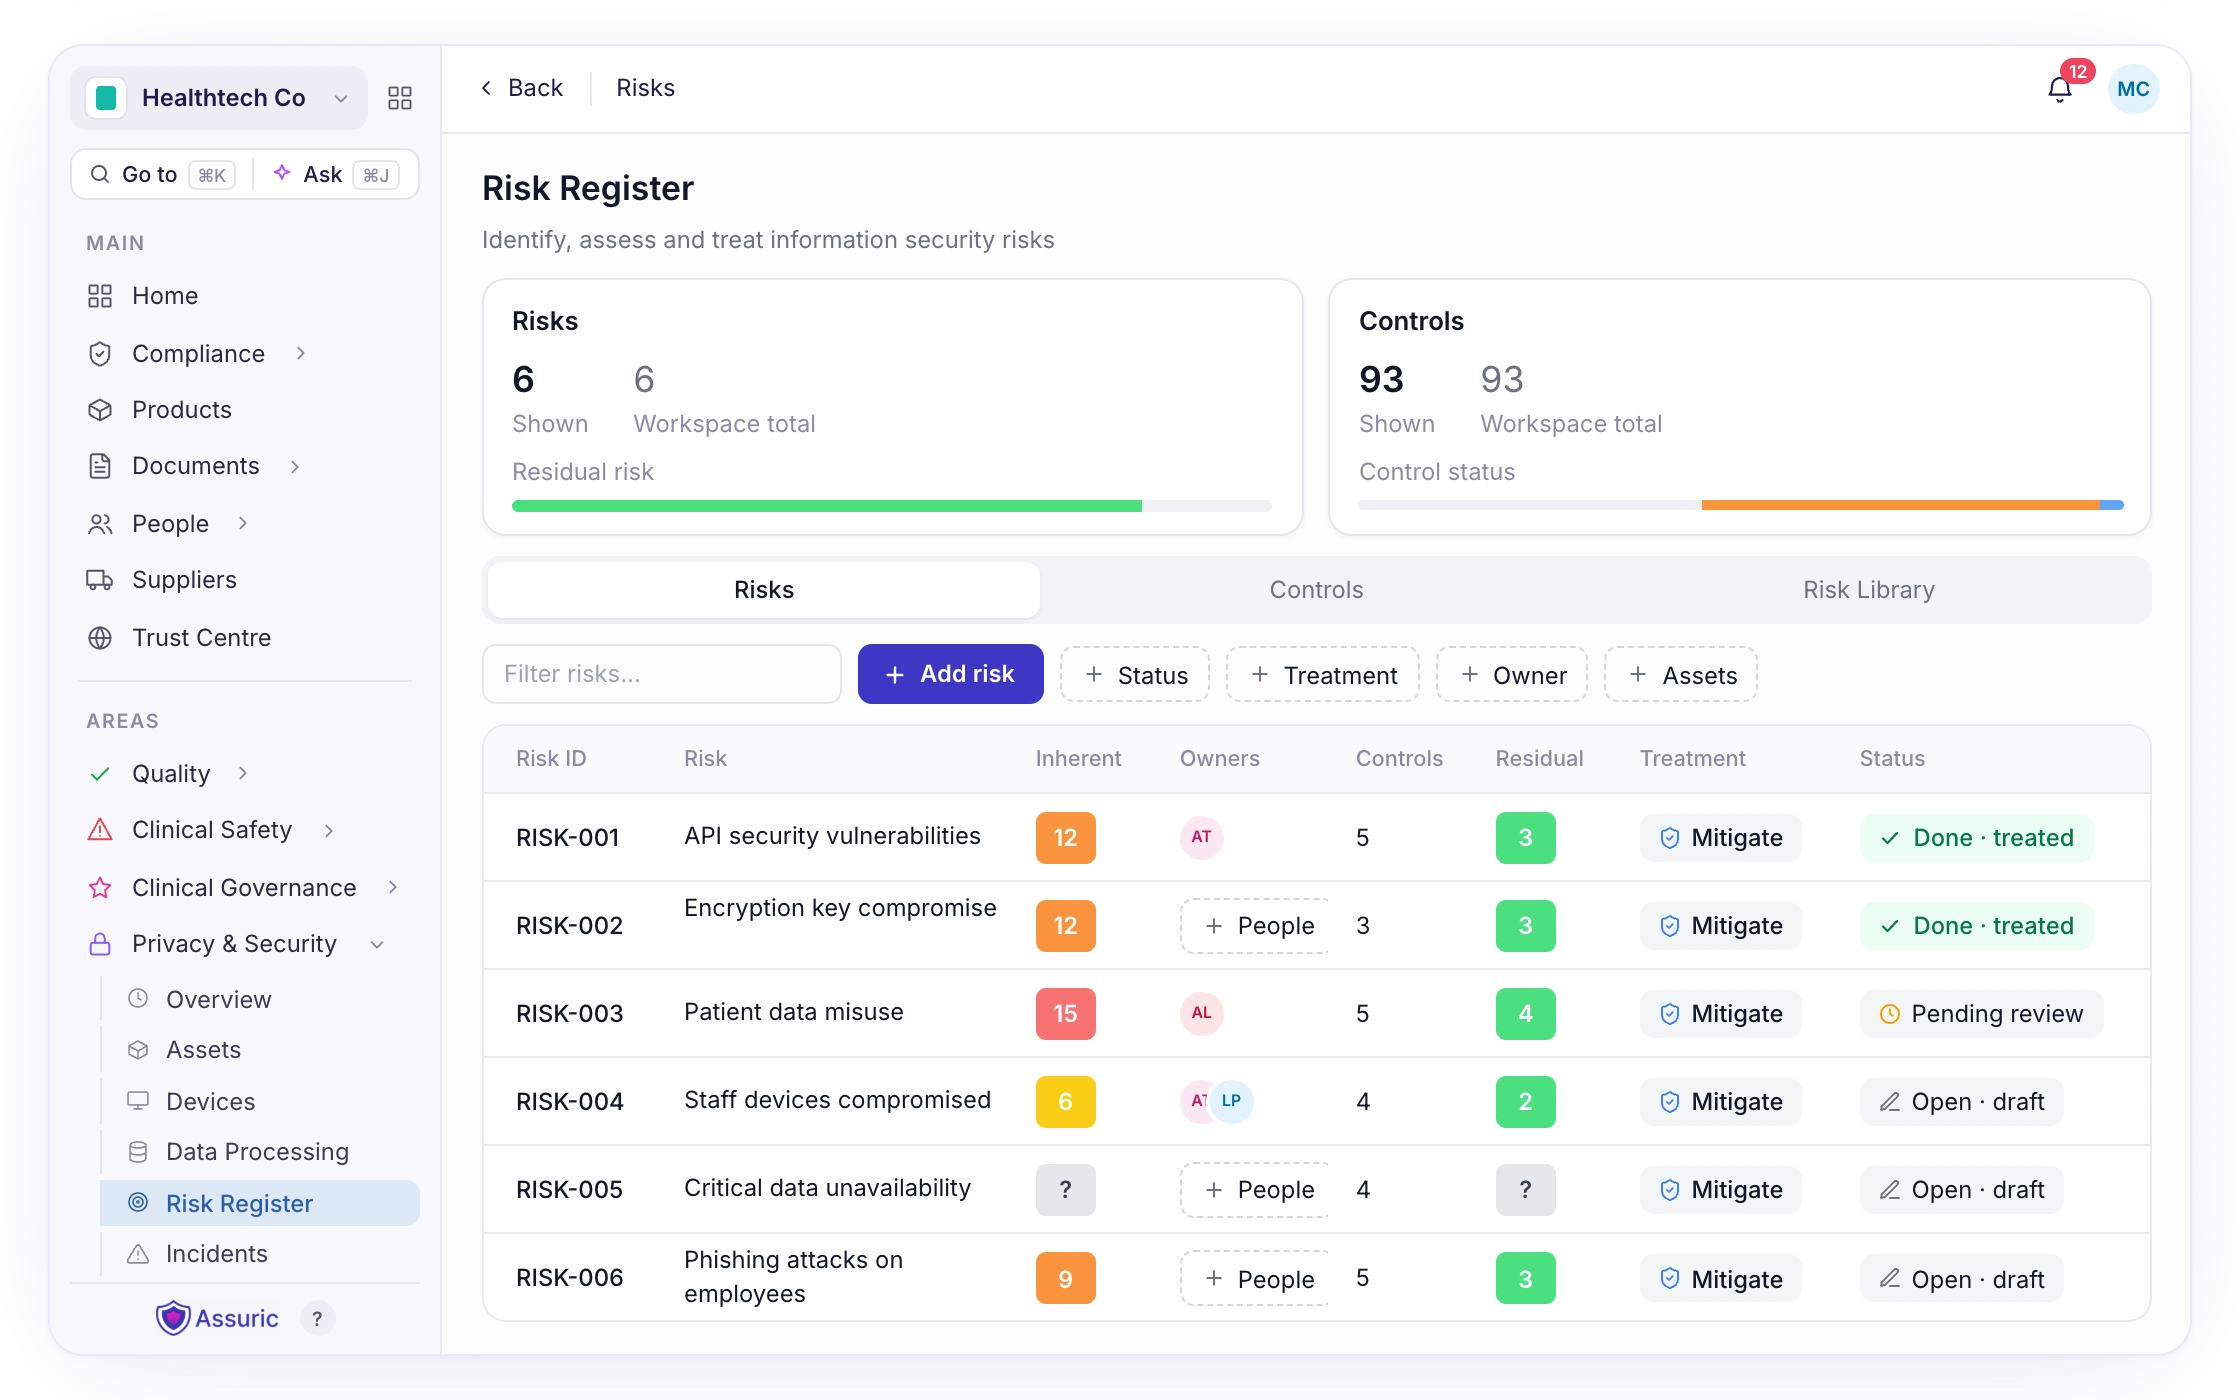
One live risk register for your information security, connected to your assets, controls and evidence, so you can reduce risk and stay ready for any audit.
Trusted bysecurity teams


Features
Record each risk with its category, owner and affected assets, and track it from identification through to treatment or closure.
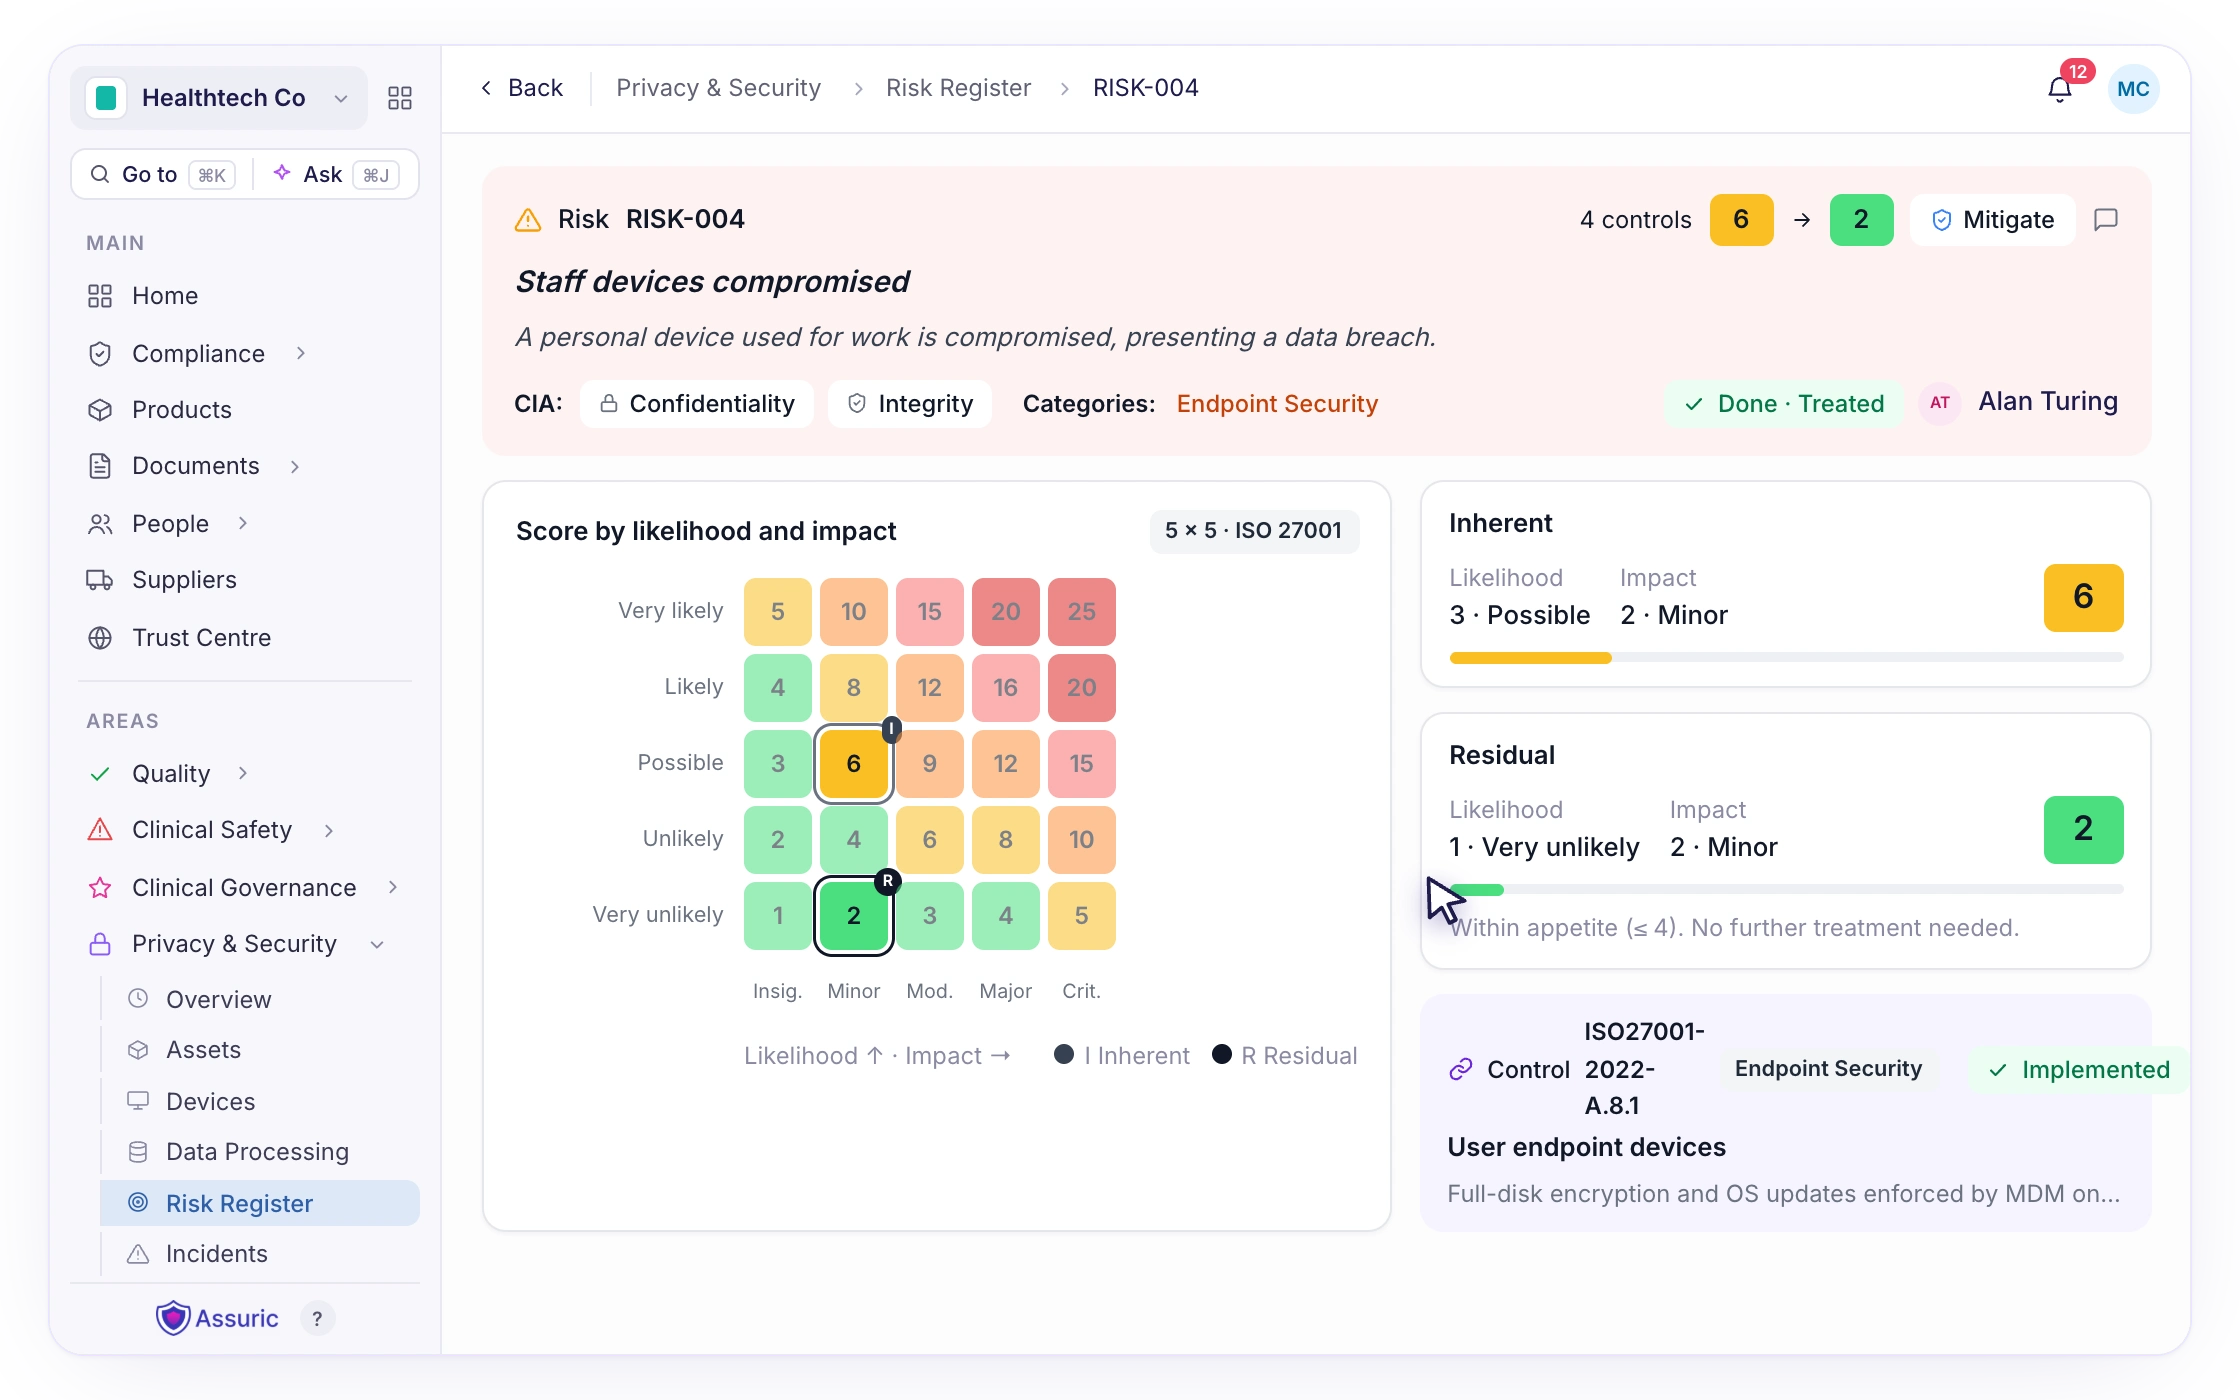
Score each risk based on a customisable matrix before and after controls are applied. Then choose to mitigate, transfer, avoid or accept it, assign owners and actions, and track progress until closure.
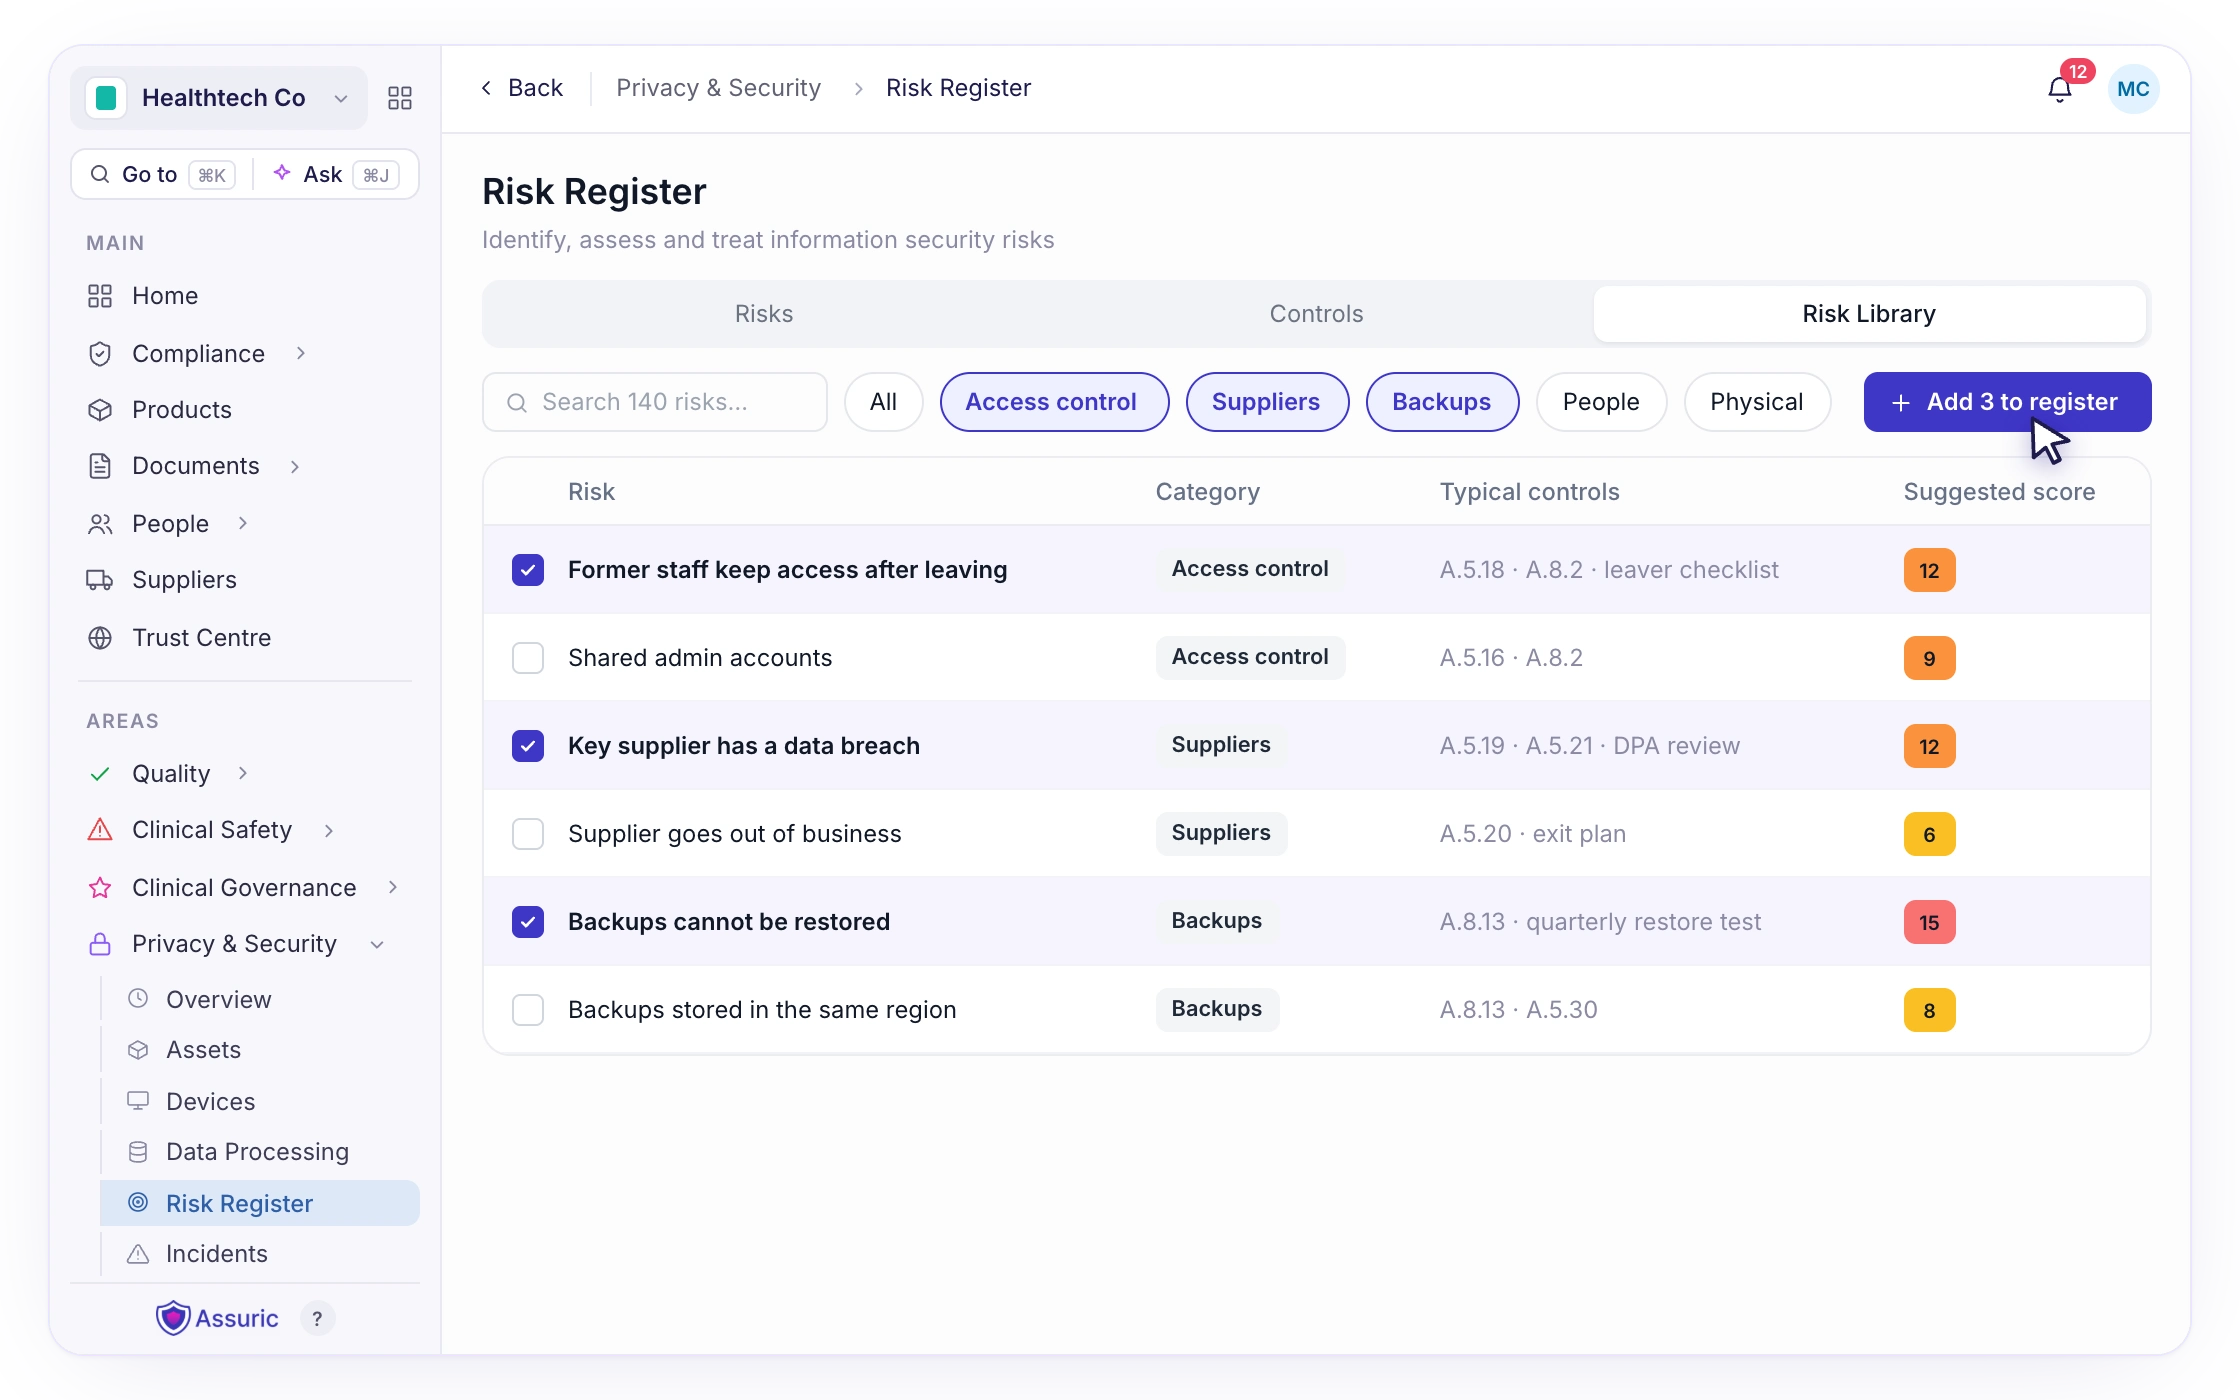
Add risks from a built-in library of common information security risks, so you never start from a blank page.
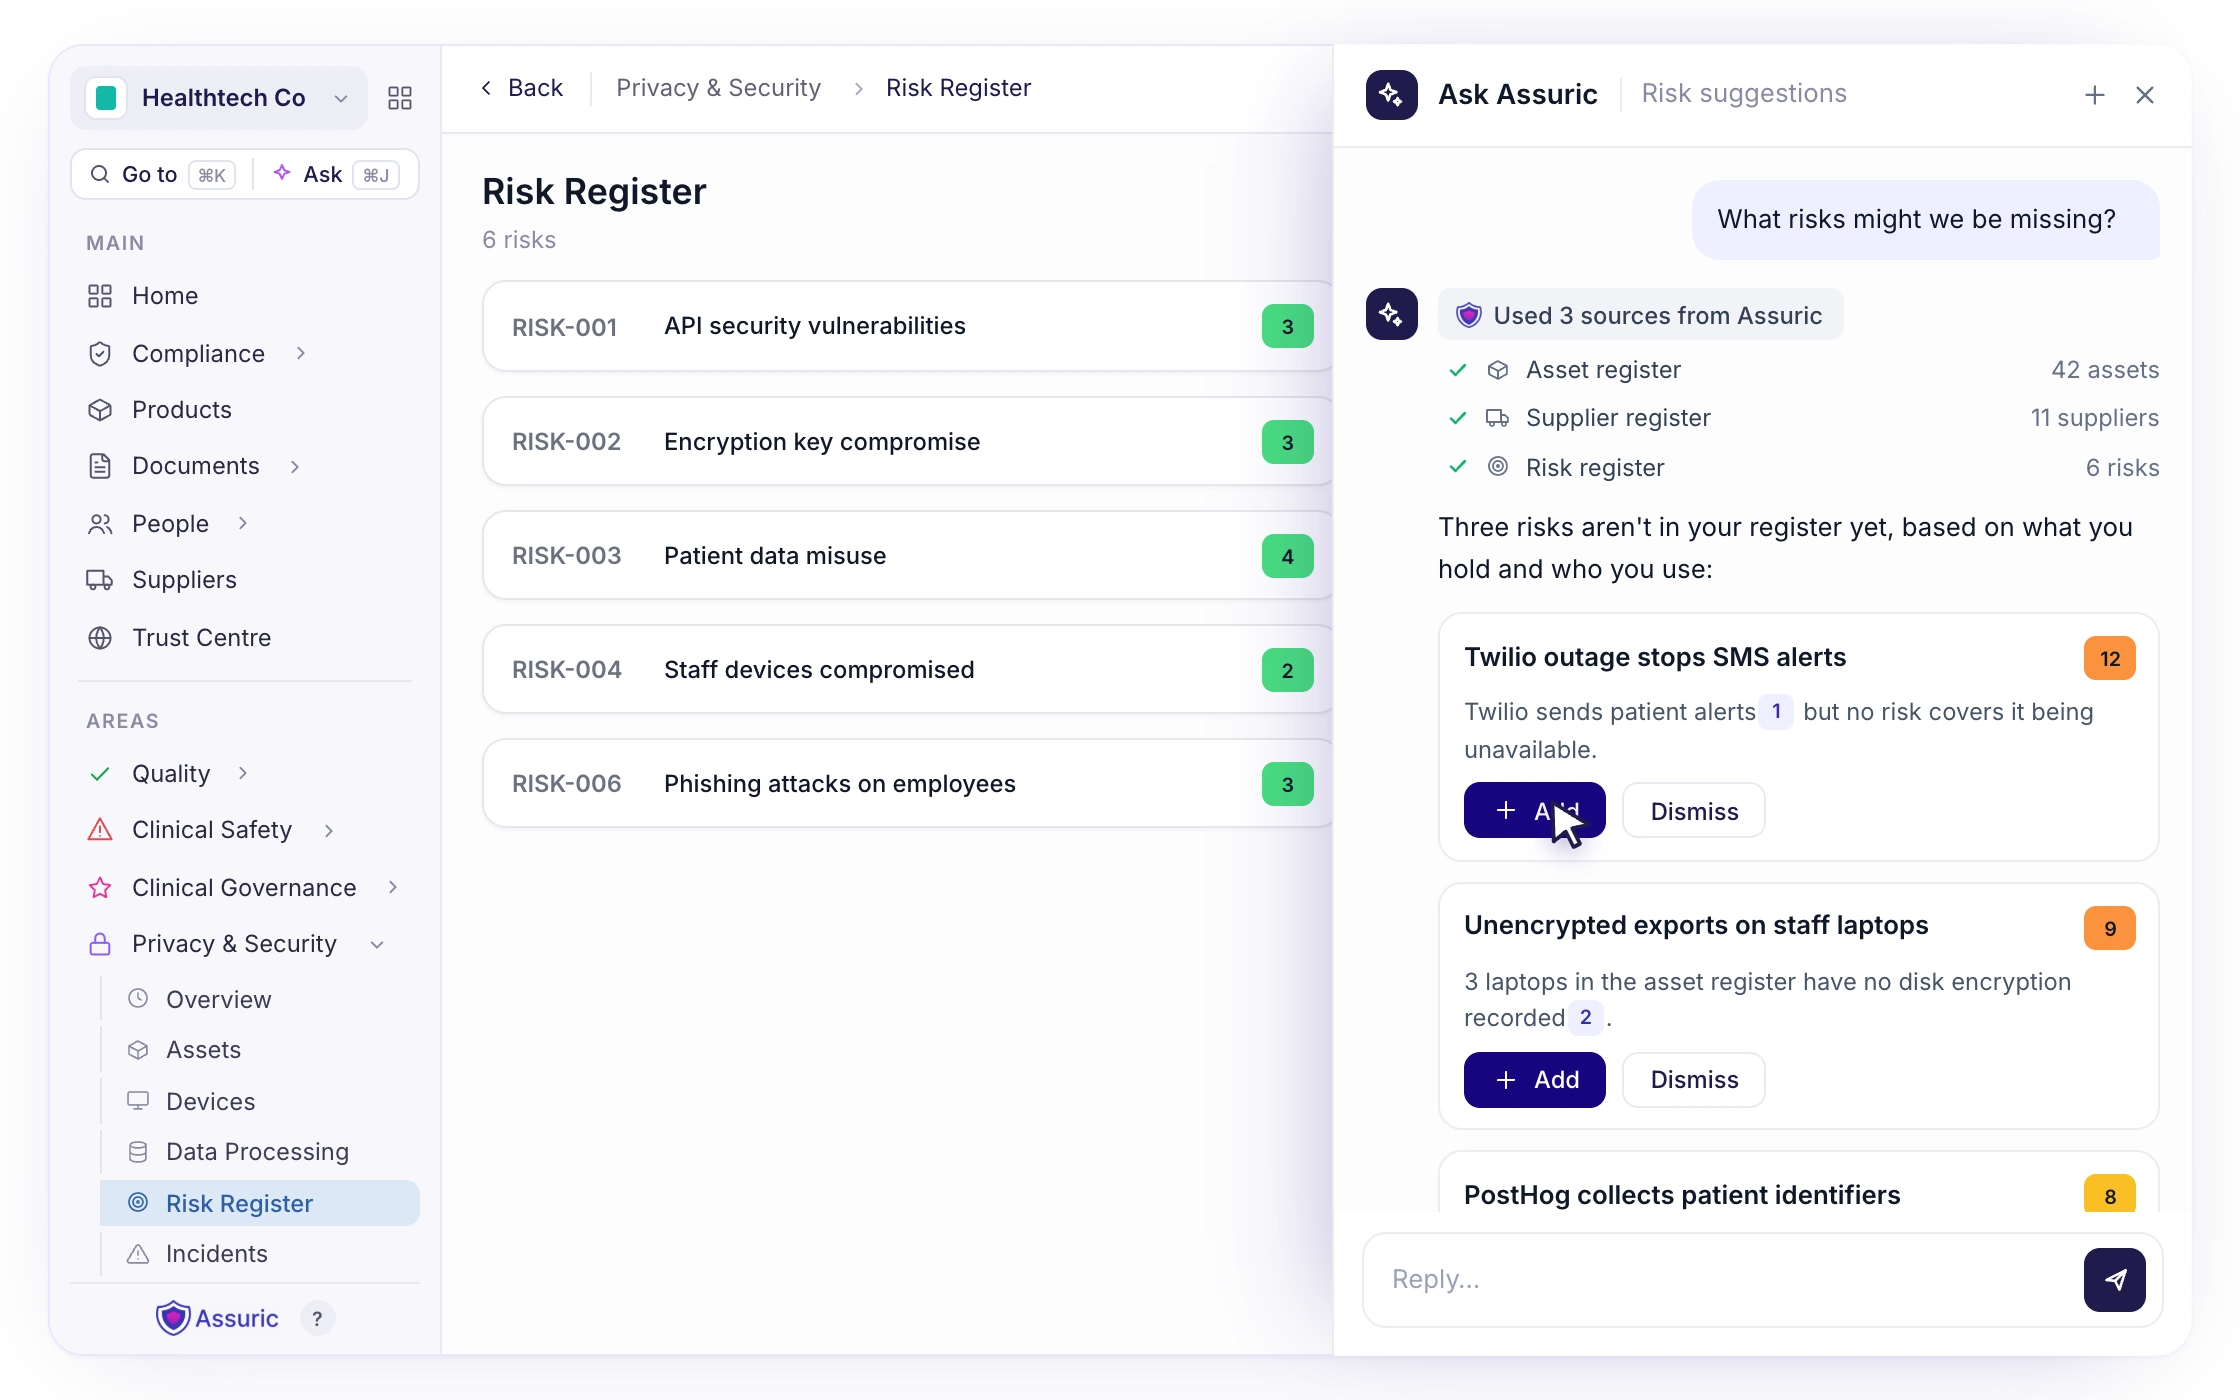
Assuric’s AI suggests relevant risks based on your assets, suppliers, processing activities and frameworks, so your register reflects how you actually work.
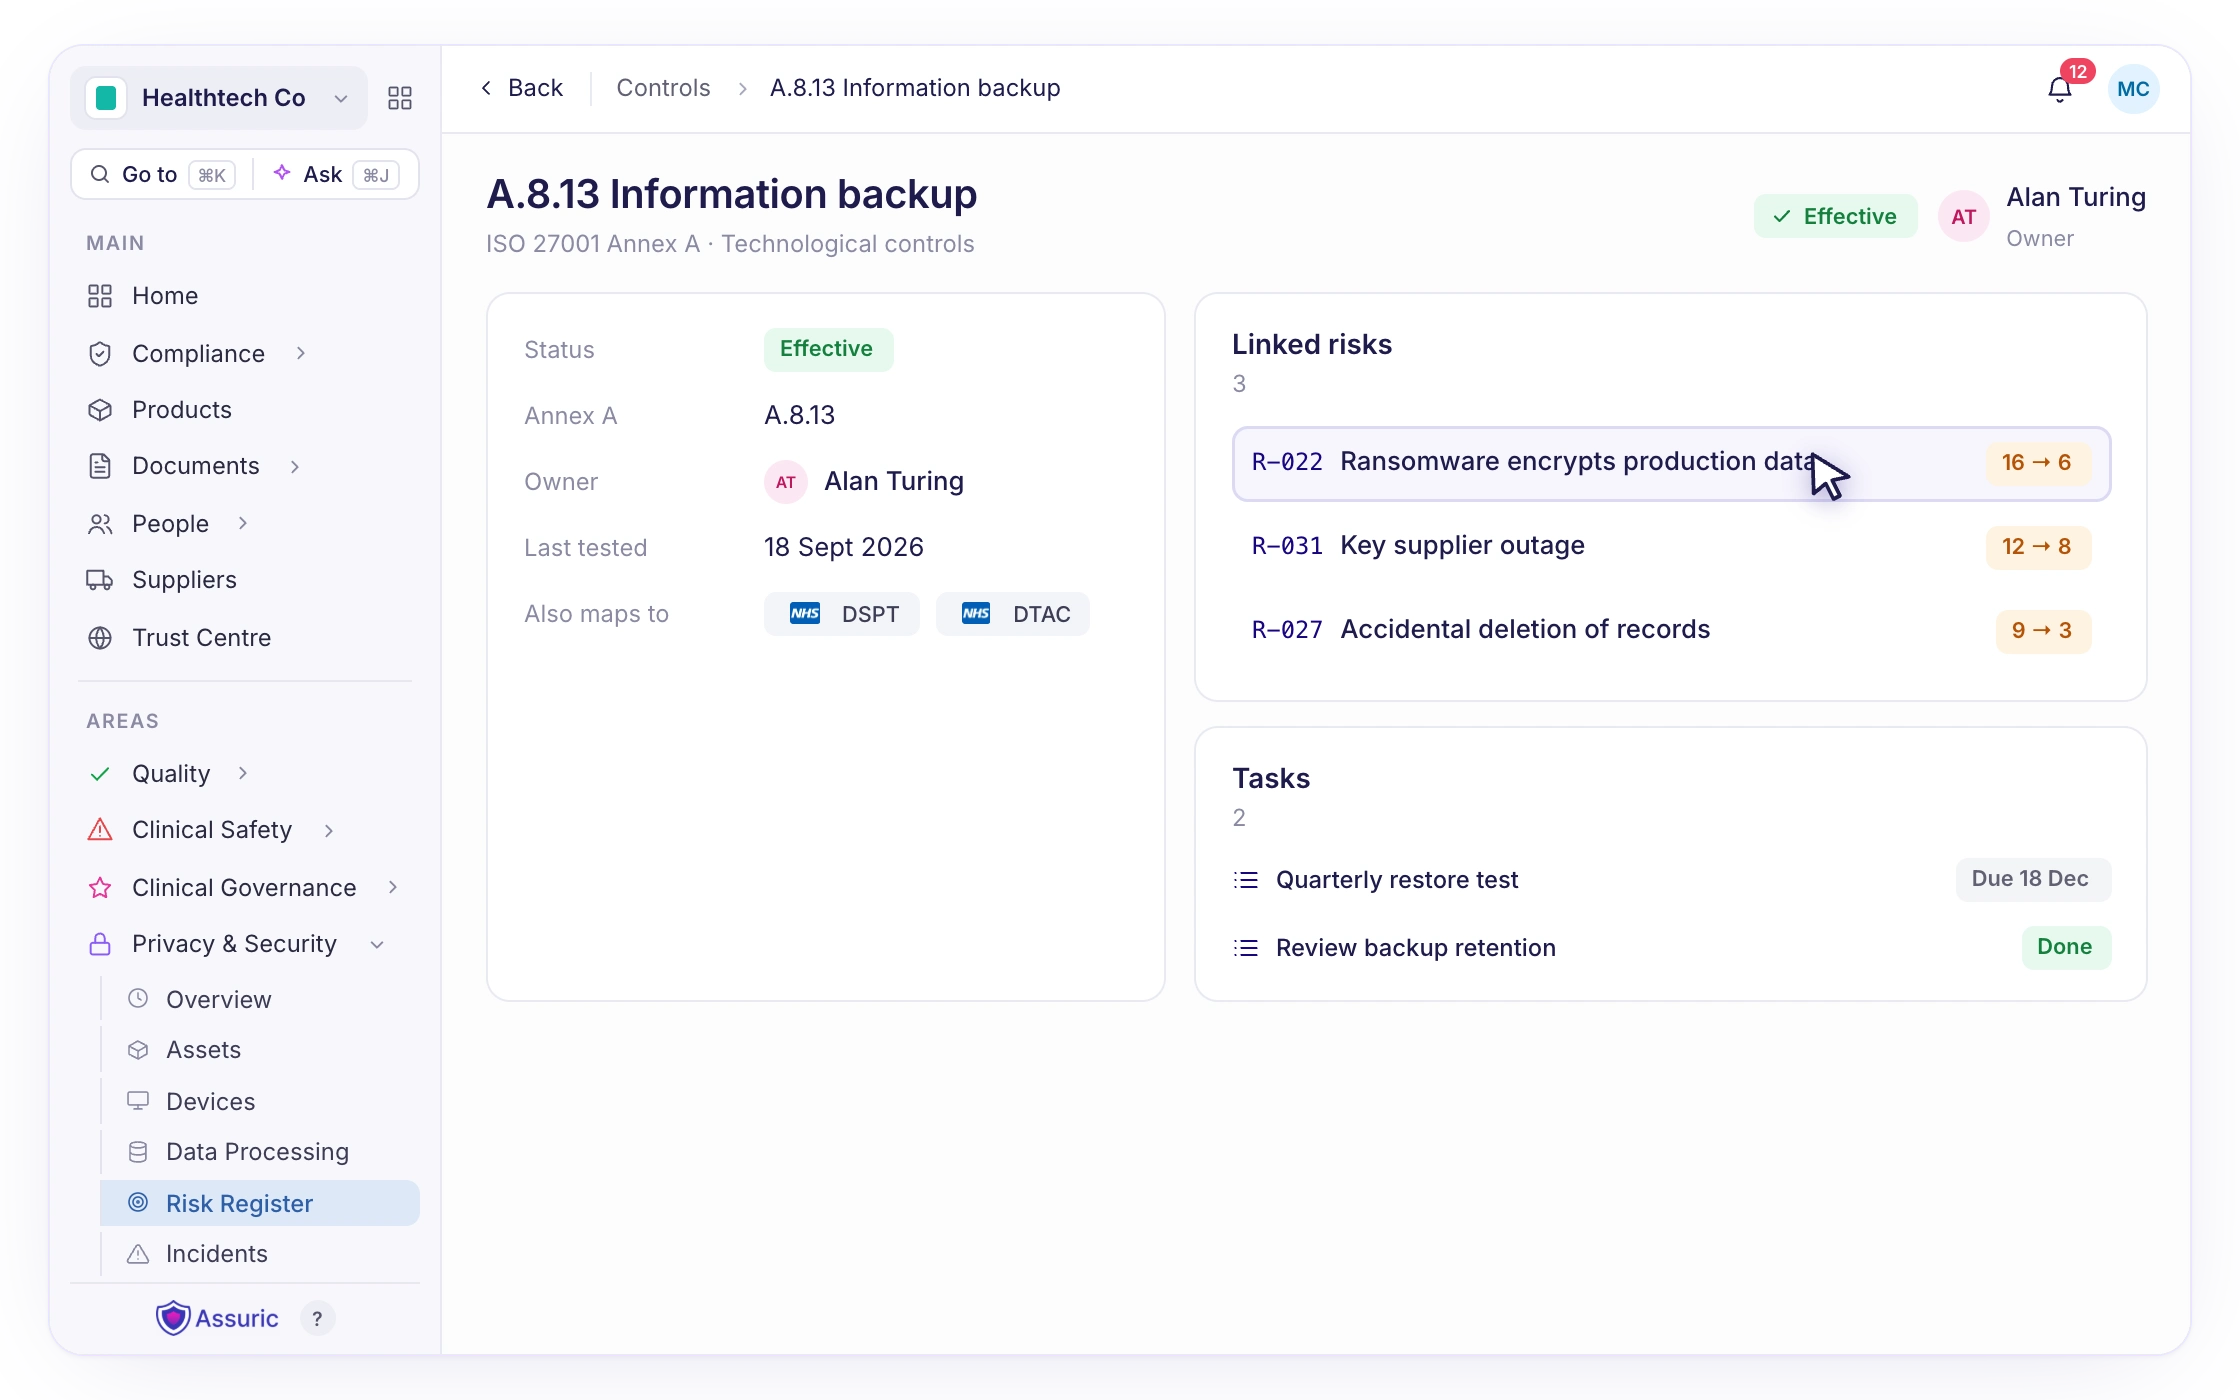
Connect each risk to the information assets and suppliers it affects and the controls that address it, with full traceability across your workspace.
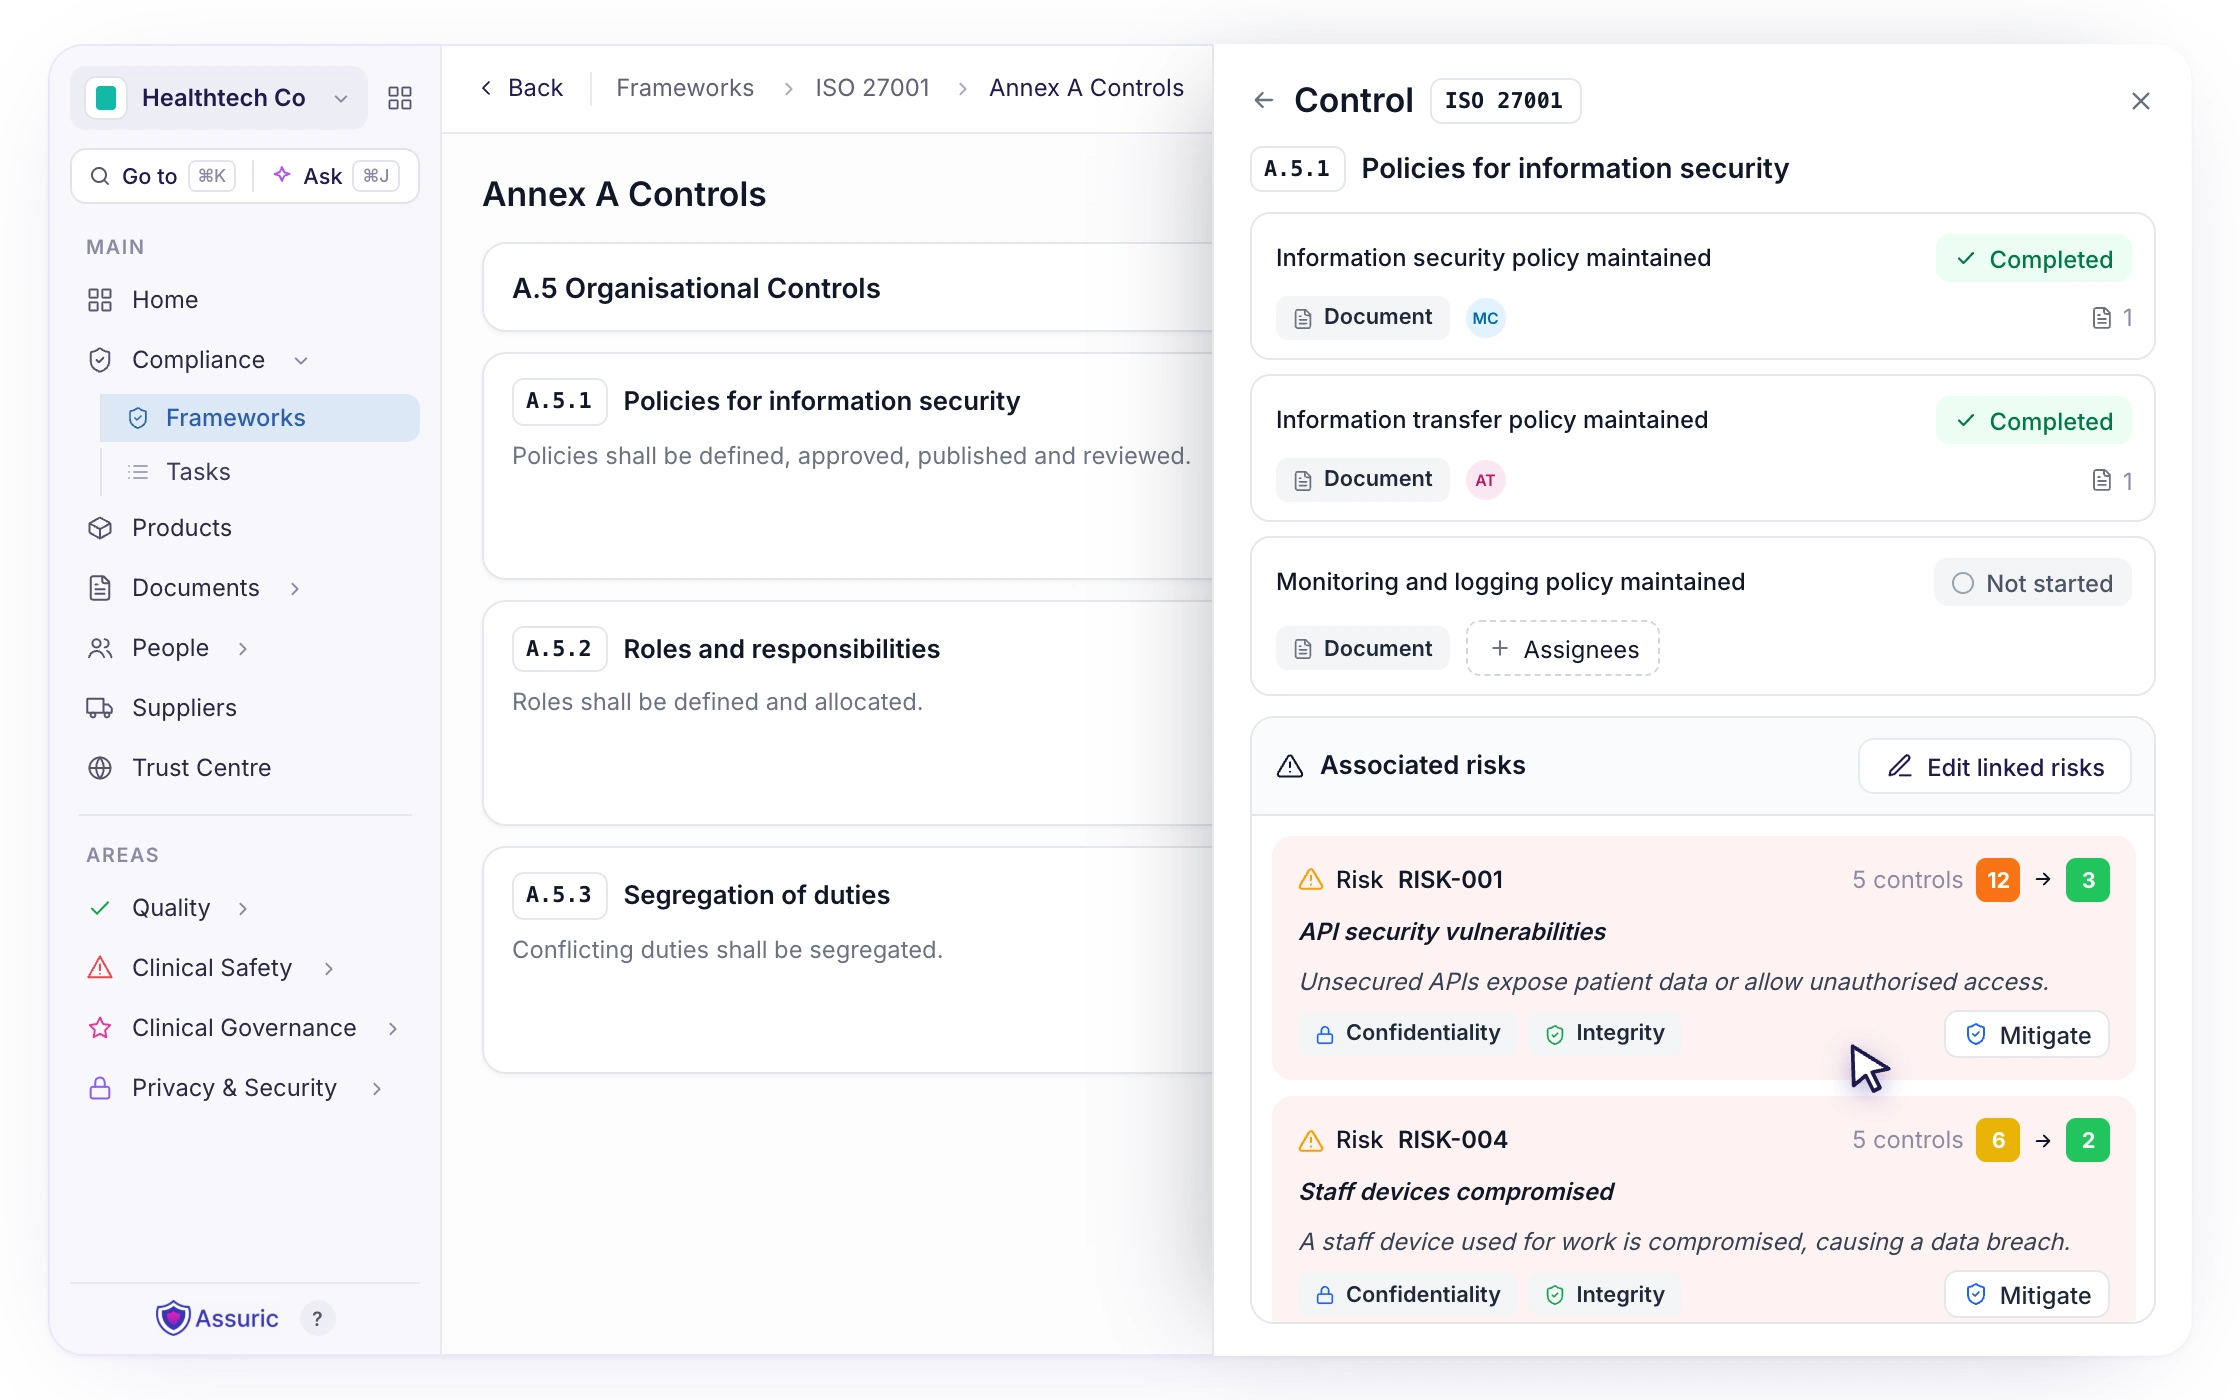
Link each control to the risks it treats and the evidence that proves it works. Your ISO 27001 Statement of Applicability is linked automatically, so there’s nothing to reconcile before an audit.
Benefits
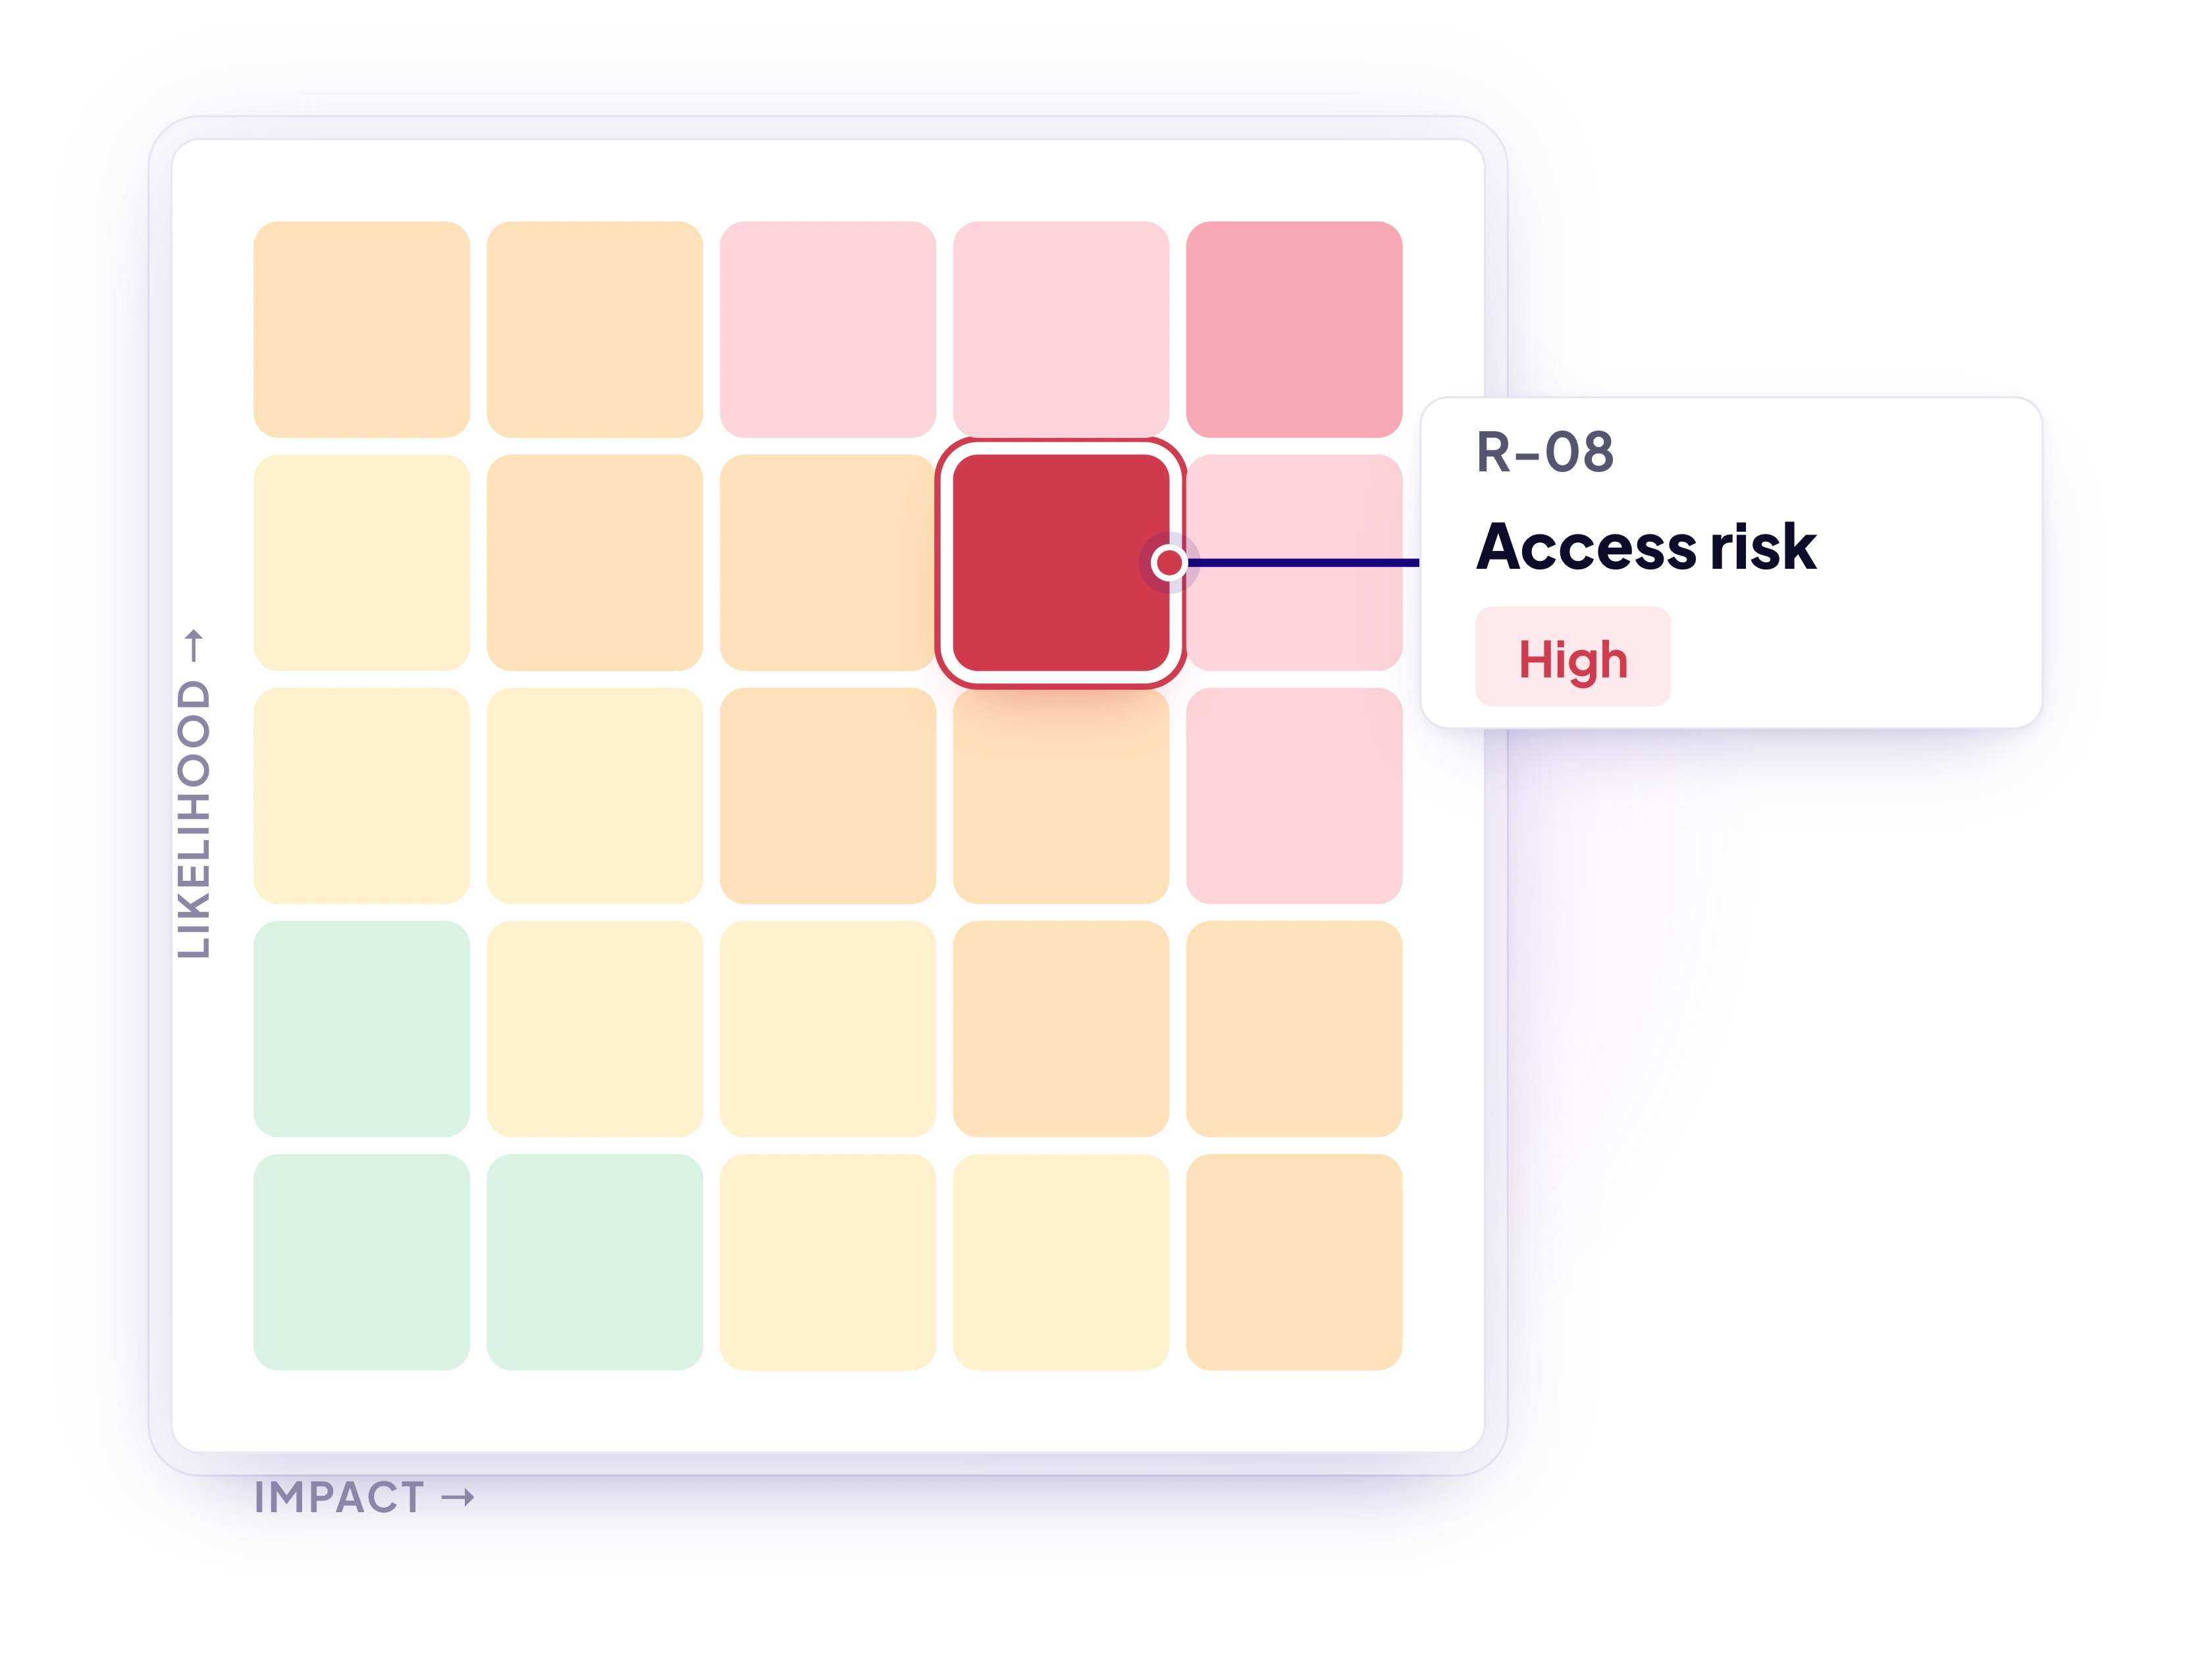
Every risk, score, treatment, owner and action in one live view, so you can see which risks need attention first and nothing falls through the cracks.
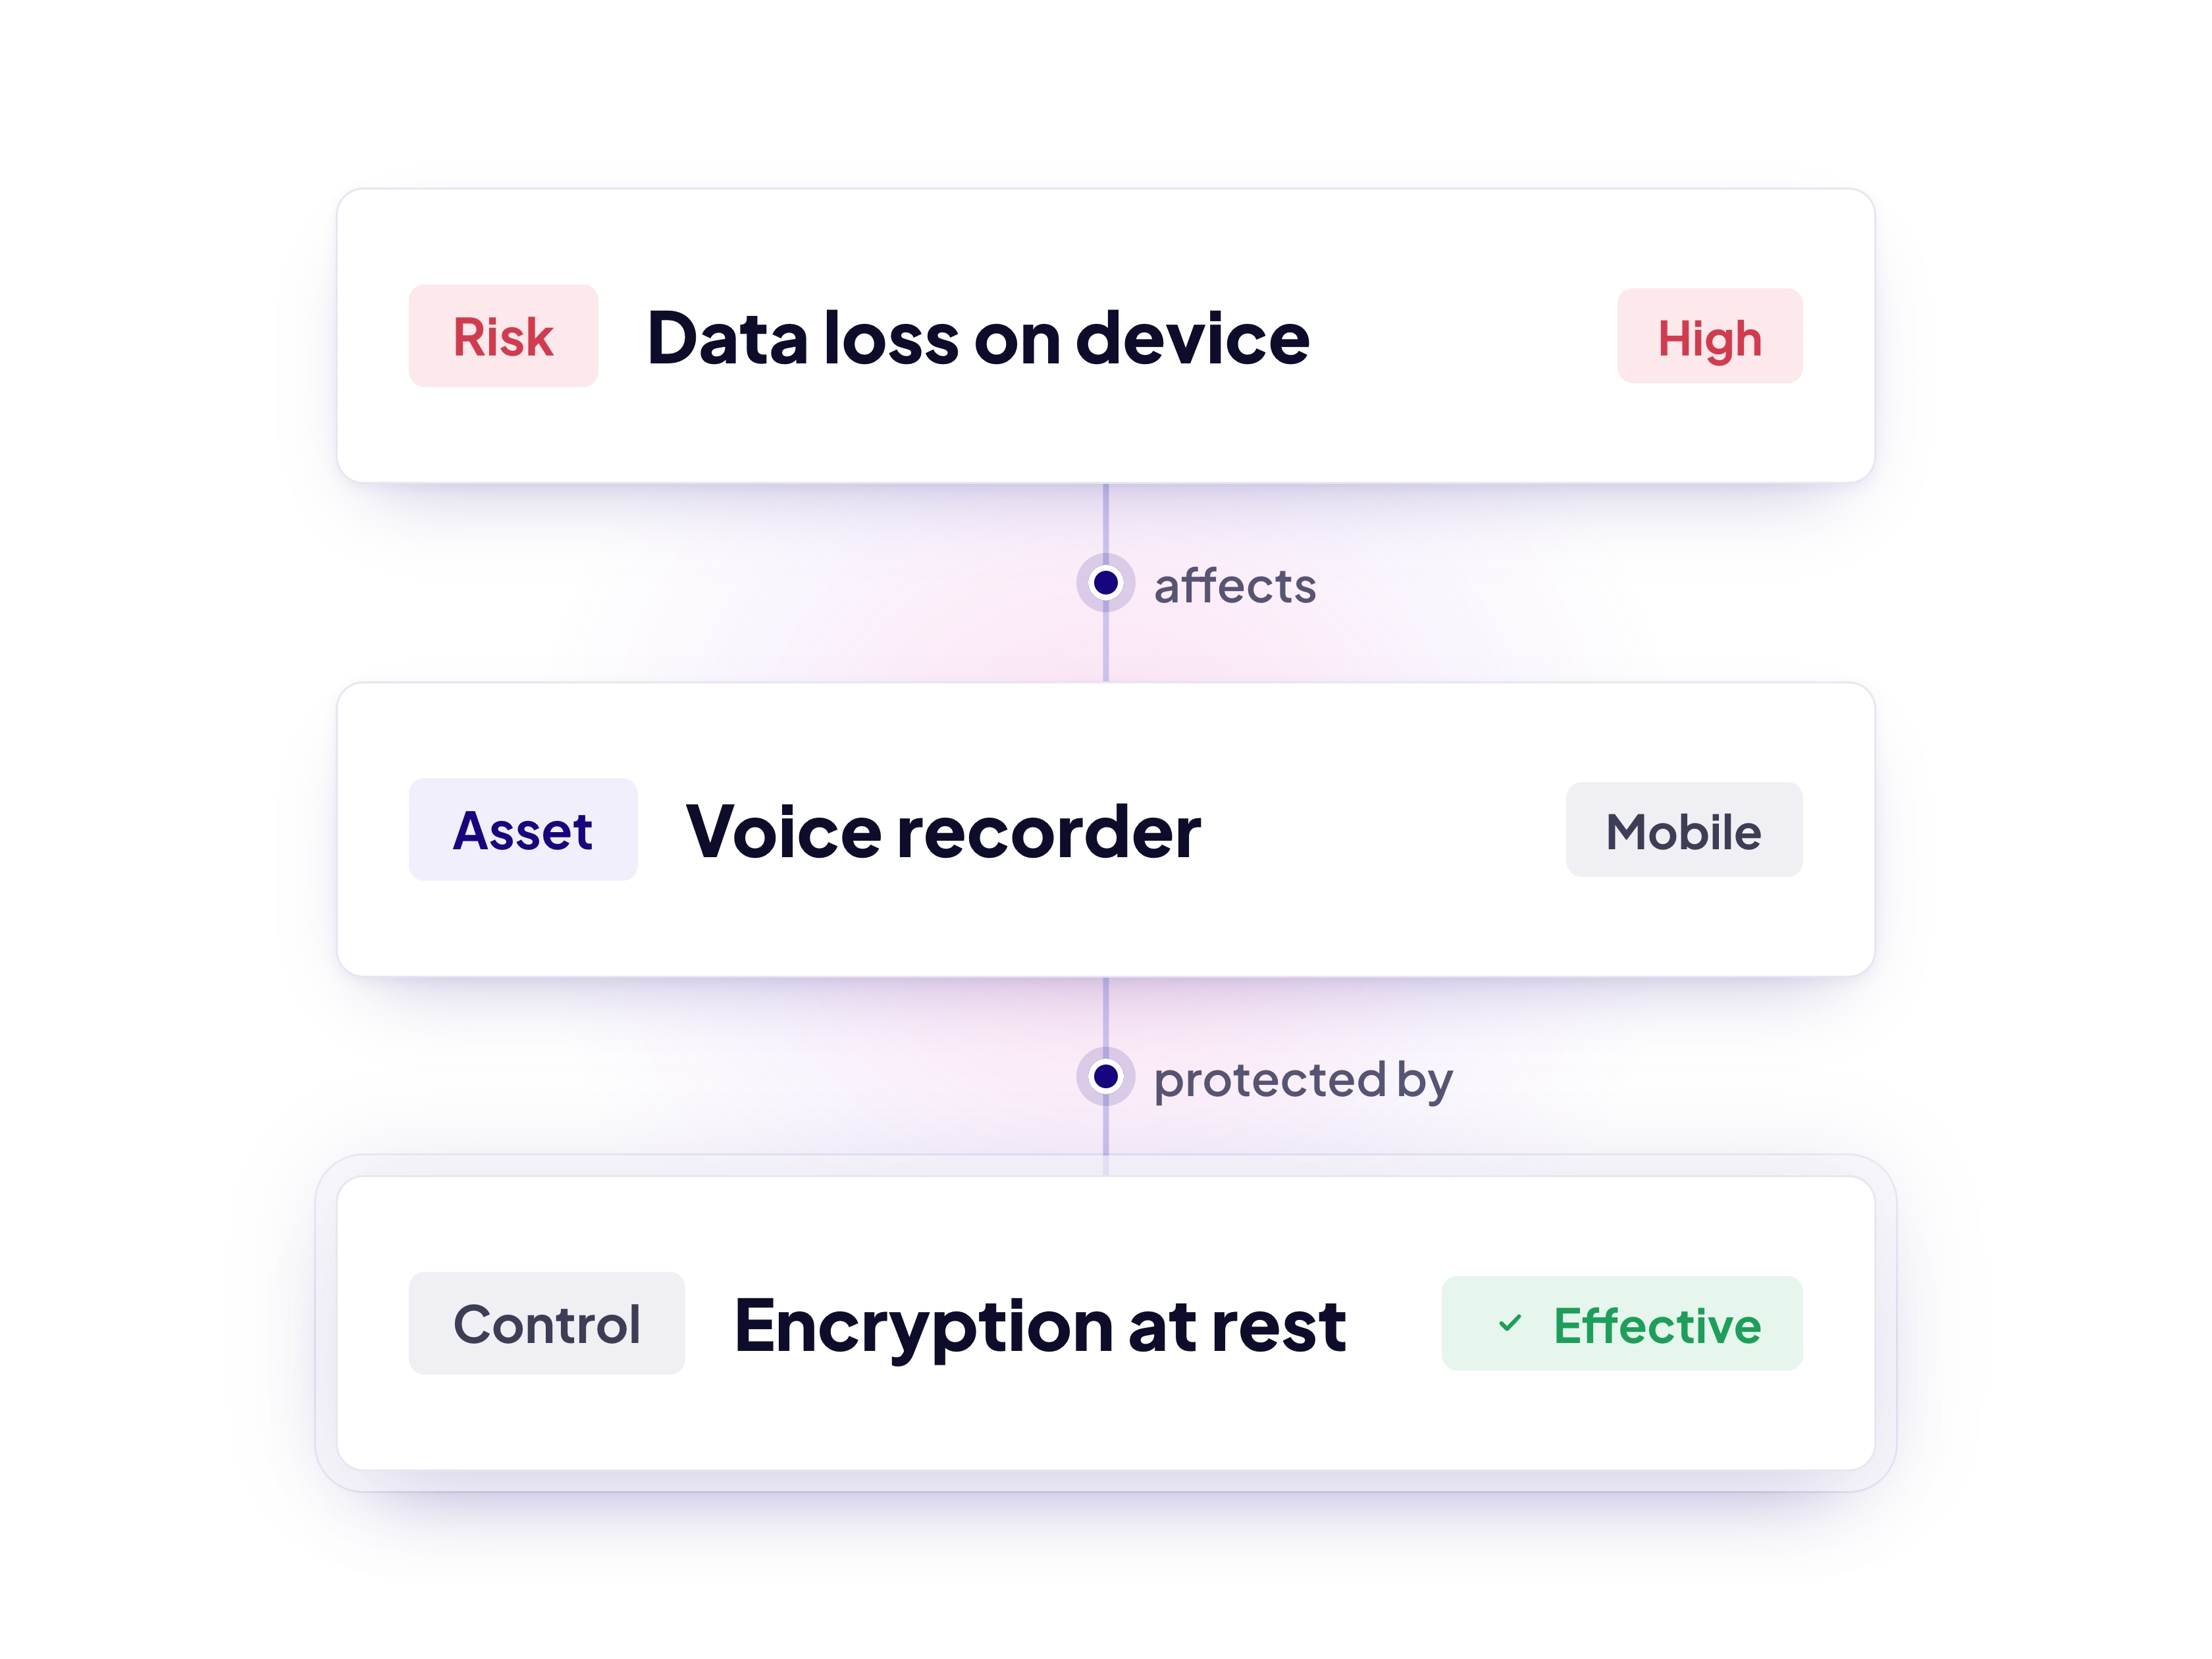
The risk library, AI suggestions and automatic SoA linking take care of the repetitive work, so keeping your register current takes minutes, not a quarterly clean-up.
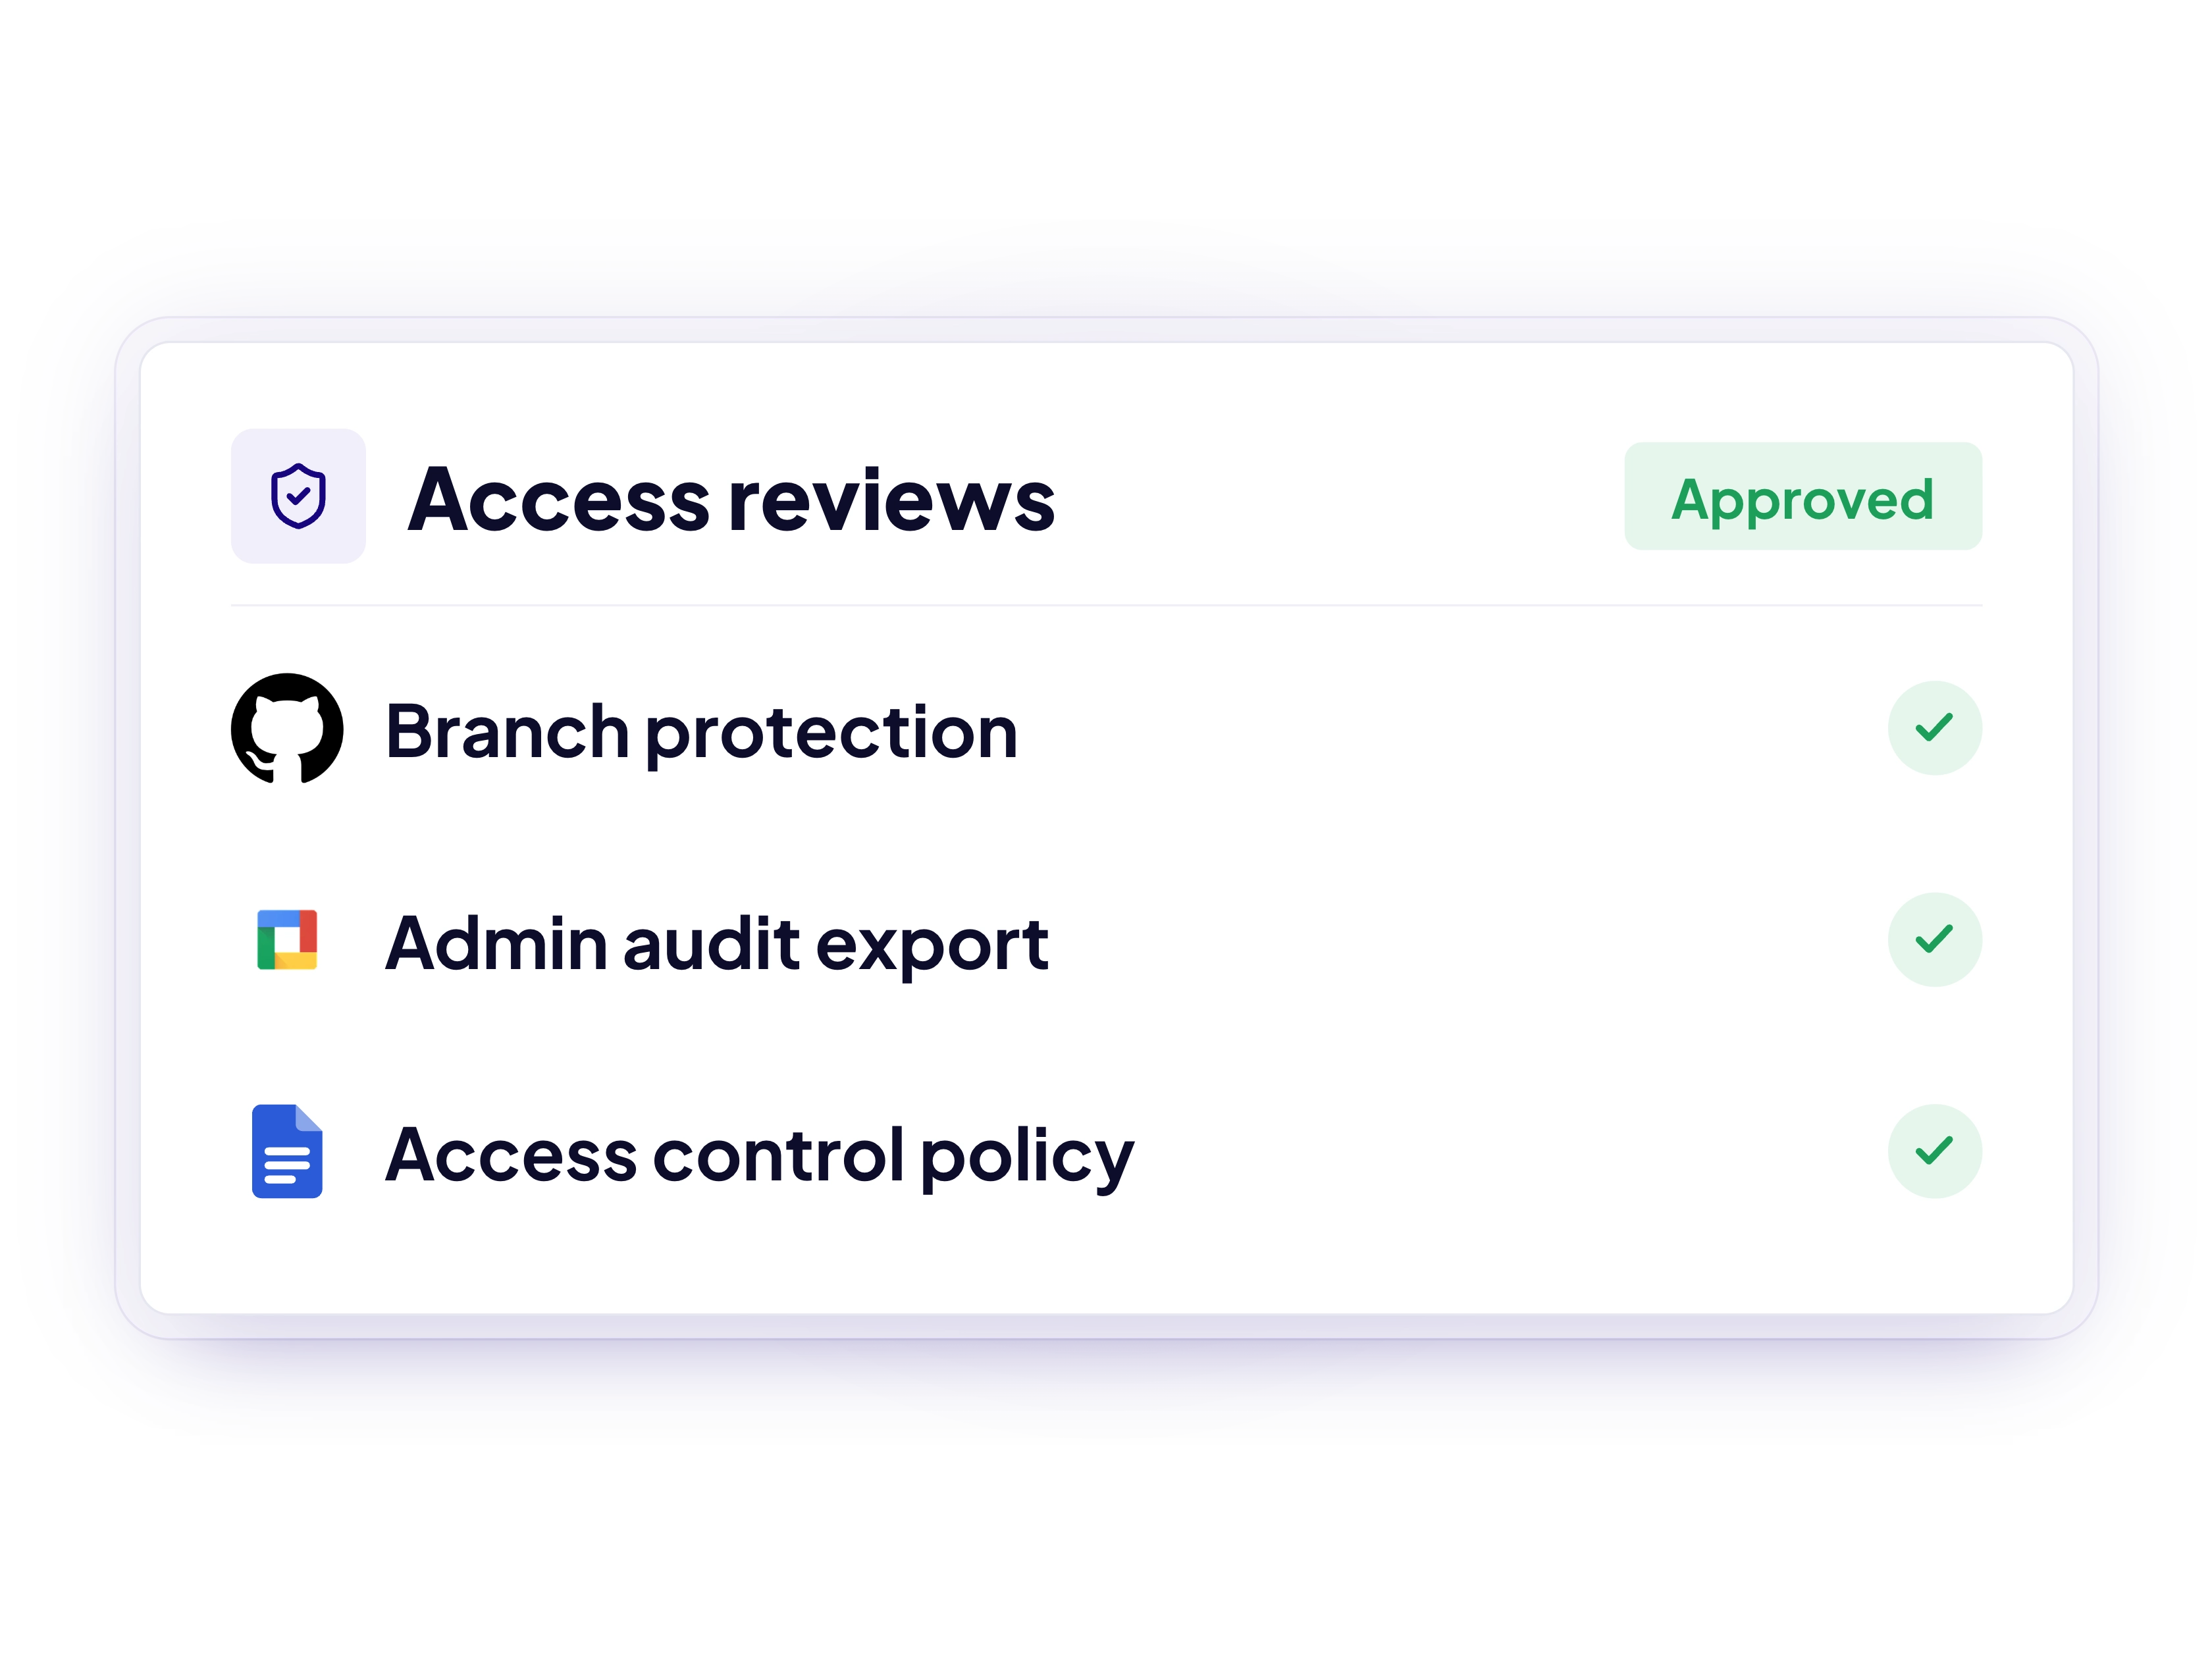
Your risks, controls, Statement of Applicability and evidence stay linked and up to date, so ISO 27001 and SOC 2 audits are a review of what’s already in Assuric, not a last-minute scramble.
Show a mature, well-managed approach to information security when NHS buyers, the DSPT or partners ask how you manage risk.
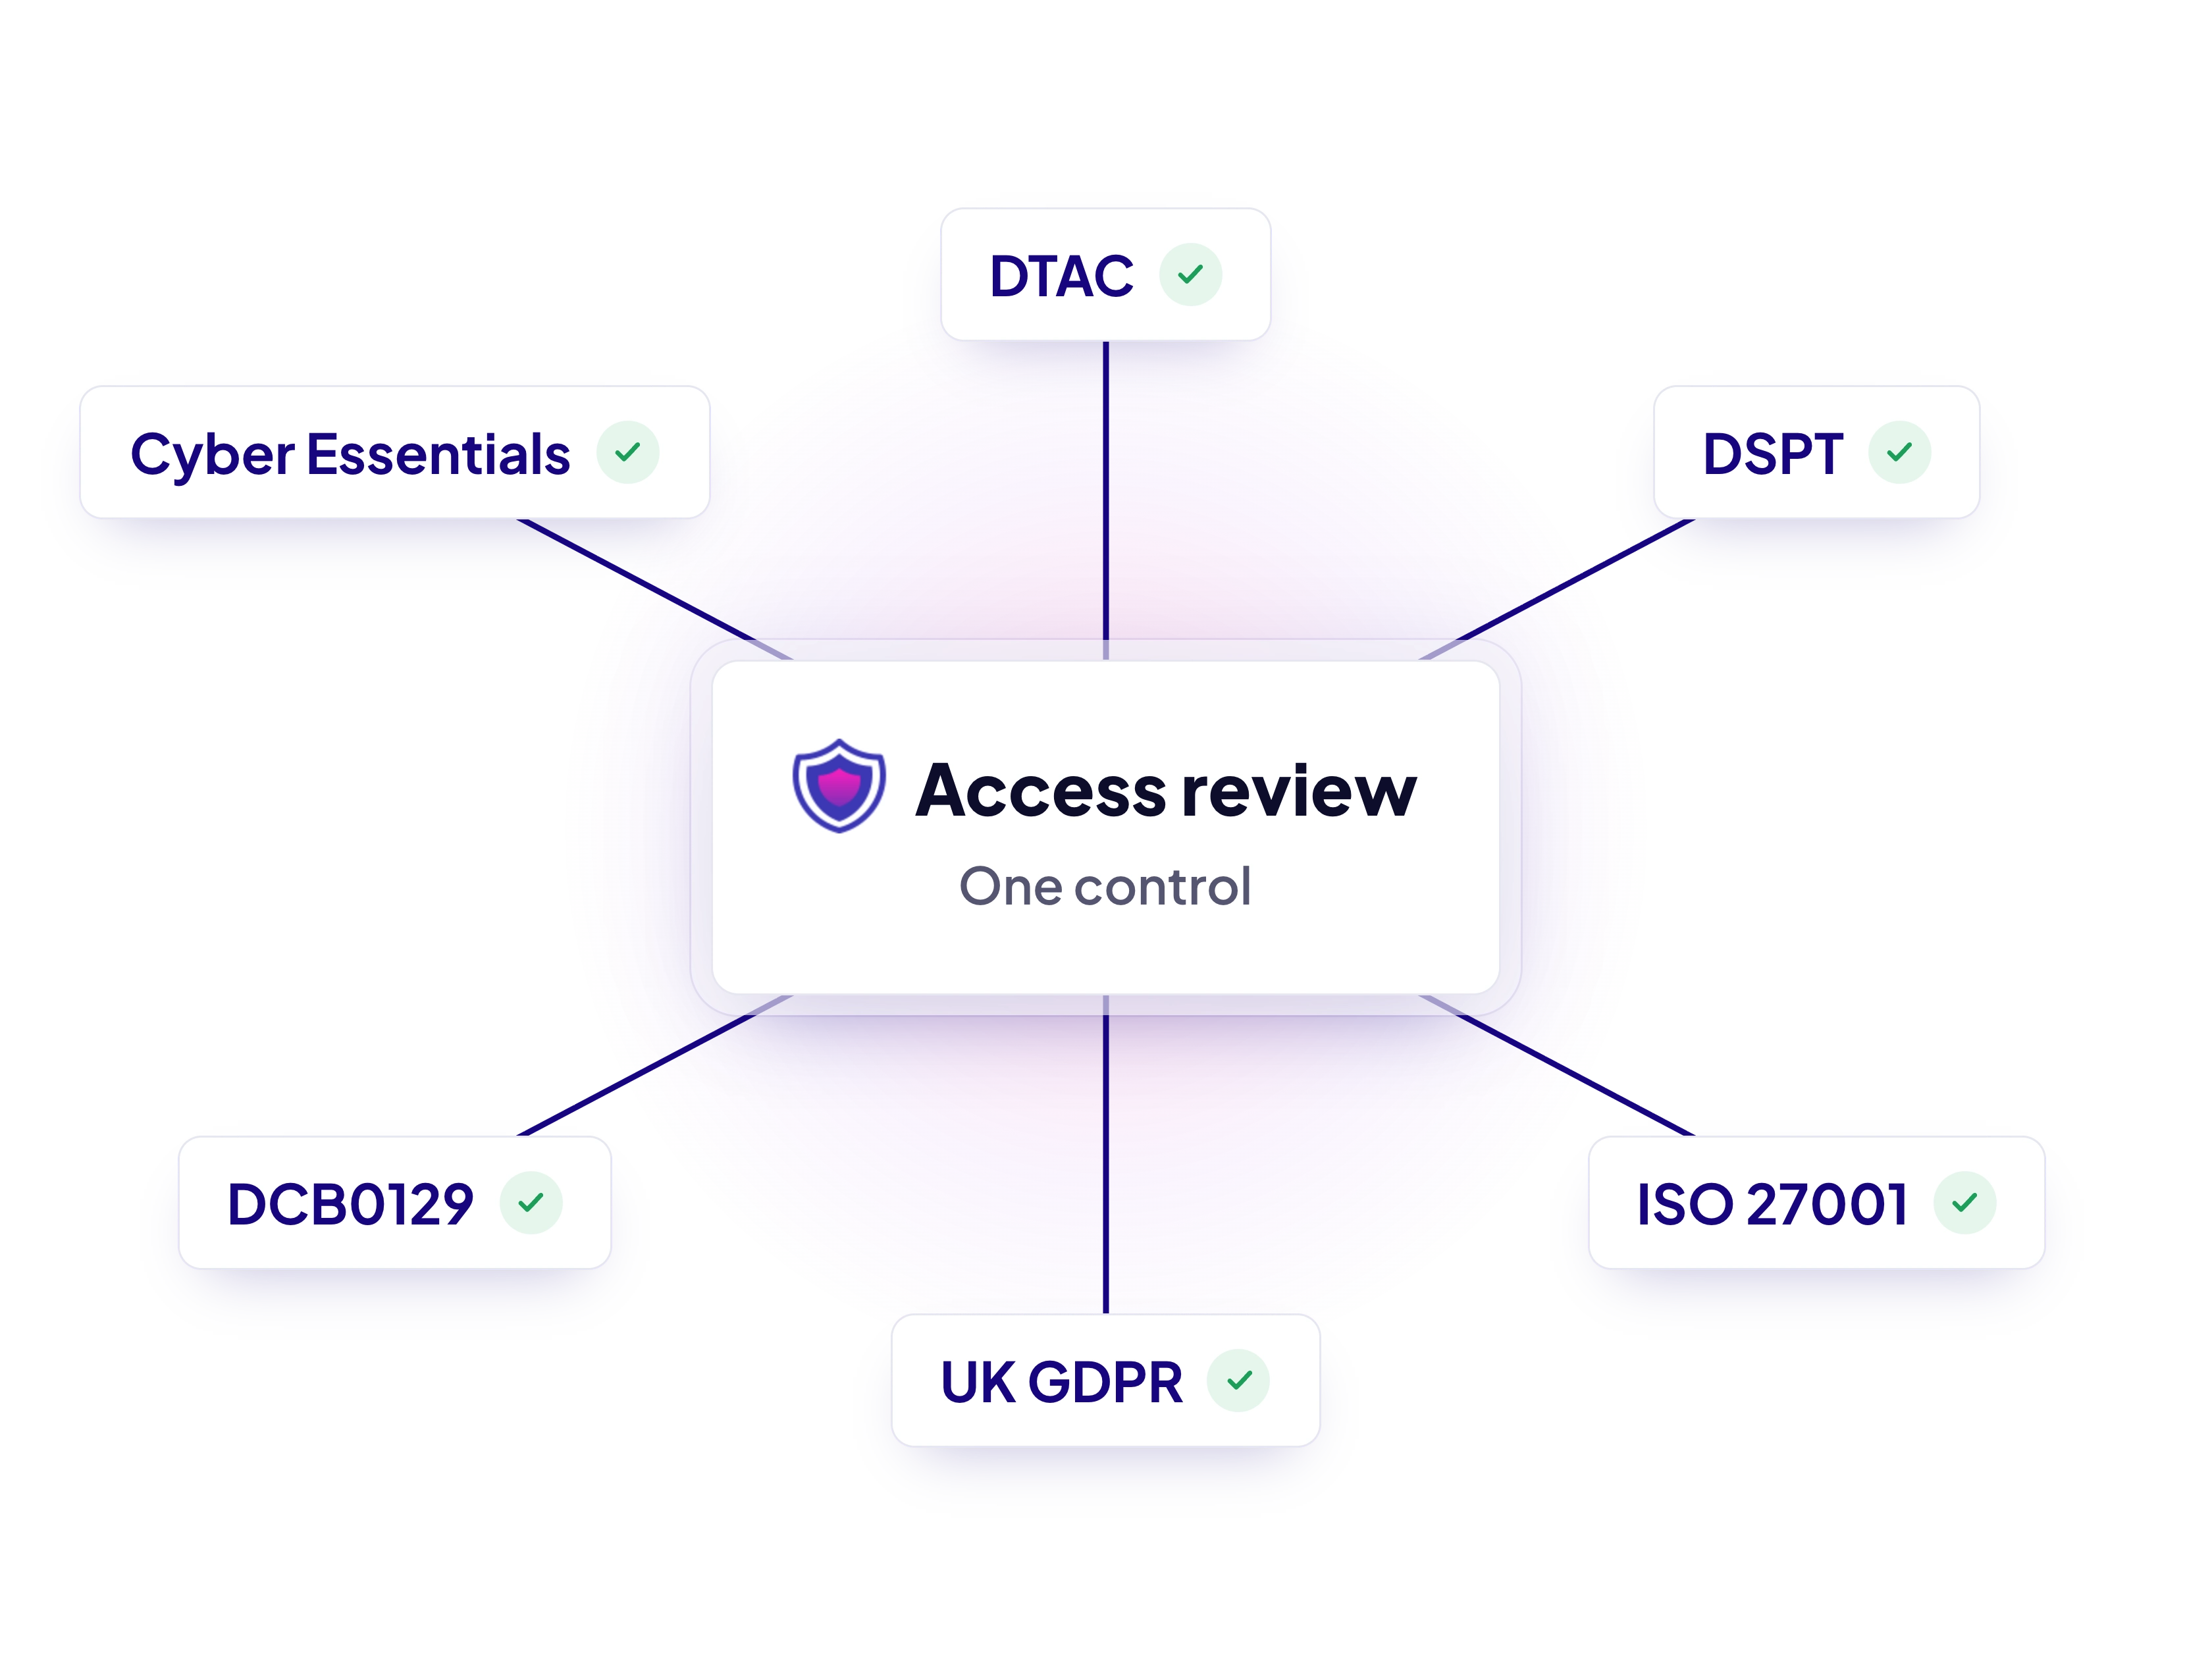
Cover information security alongside UK and EU MDR, NHS compliance, CQC and more, reusing evidence across frameworks instead of starting again.

“We couldn't speak highly enough of both the Assuric team and the platform itself, which is incredibly easy to use, and with the skill and hardworking nature of the Assuric team. They've been a key component in accelerating our progress and deployments!”
Maks Kozarzewski
COO, VitVio

“The Assuric platform is a game changer in the clinical risk management field. It has been carefully designed to make the job of a CSO significantly more streamlined. The team are excellent and responsive to any product suggestions I have requested, and it has been a pleasure to work with them.”
Paul Llewellyn
CCIO, Accenture

“Assuric has been fantastic in helping us quickly and safely navigate regulatory compliance in the UK. From completing Cybersecurity requirements to DSPT, DCB0129, and DTAC, the team was supportive, extremely knowledgeable, and the platform made everything quick and straightforward. A separate regulatory company we consulted at the beginning even remarked on how quickly we achieved compliance!”
Katie Baker
Director UK & Ireland, Tandem
Overlapping requirements and evidence are mapped across frameworks automatically, so you never do the same work twice.
It's how you find, assess and deal with risks to the information your organisation holds. You record each risk, score how likely and serious it is, decide how to handle it and track it until it's closed.
Each risk is scored on likelihood and impact using a customisable matrix, before and after controls are applied, so you can see the effect of your controls. You then choose to mitigate, transfer, avoid or accept it, and track the actions through to closure.
Yes. ISO 27001 requires you to carry out information security risk assessments, record how each risk will be treated and produce a Statement of Applicability. The NHS Data Security and Protection Toolkit (DSPT) also expects you to show how you identify and manage information security risks, and a risk register is the usual way to evidence it.
ISO 27001, including Annex A controls and your Statement of Applicability, which is linked to your risk register automatically. You can also manage controls for SOC 2, the DSPT, Cyber Essentials and other frameworks, each with a status and owner.
Yes. Alongside information security, you can manage broader corporate risks in Assuric, such as operational, financial, commercial or regulatory risks, using your own categories and scoring matrix. If you need to, you can also set up separate risk registers for different teams or departments, so each one manages its own risks in one platform.
Yes. We offer a full migration service, and Assuric’s AI can import an existing risk register, so you don’t start from scratch.
No. This page covers information security risks. Clinical safety risks under DCB0129 and DCB0160 are managed in the hazard log, and medical device risks under ISO 14971 have their own risk management.
See how Assuric helps you record, score and treat information security risks in one place.


