Spend less time on admin
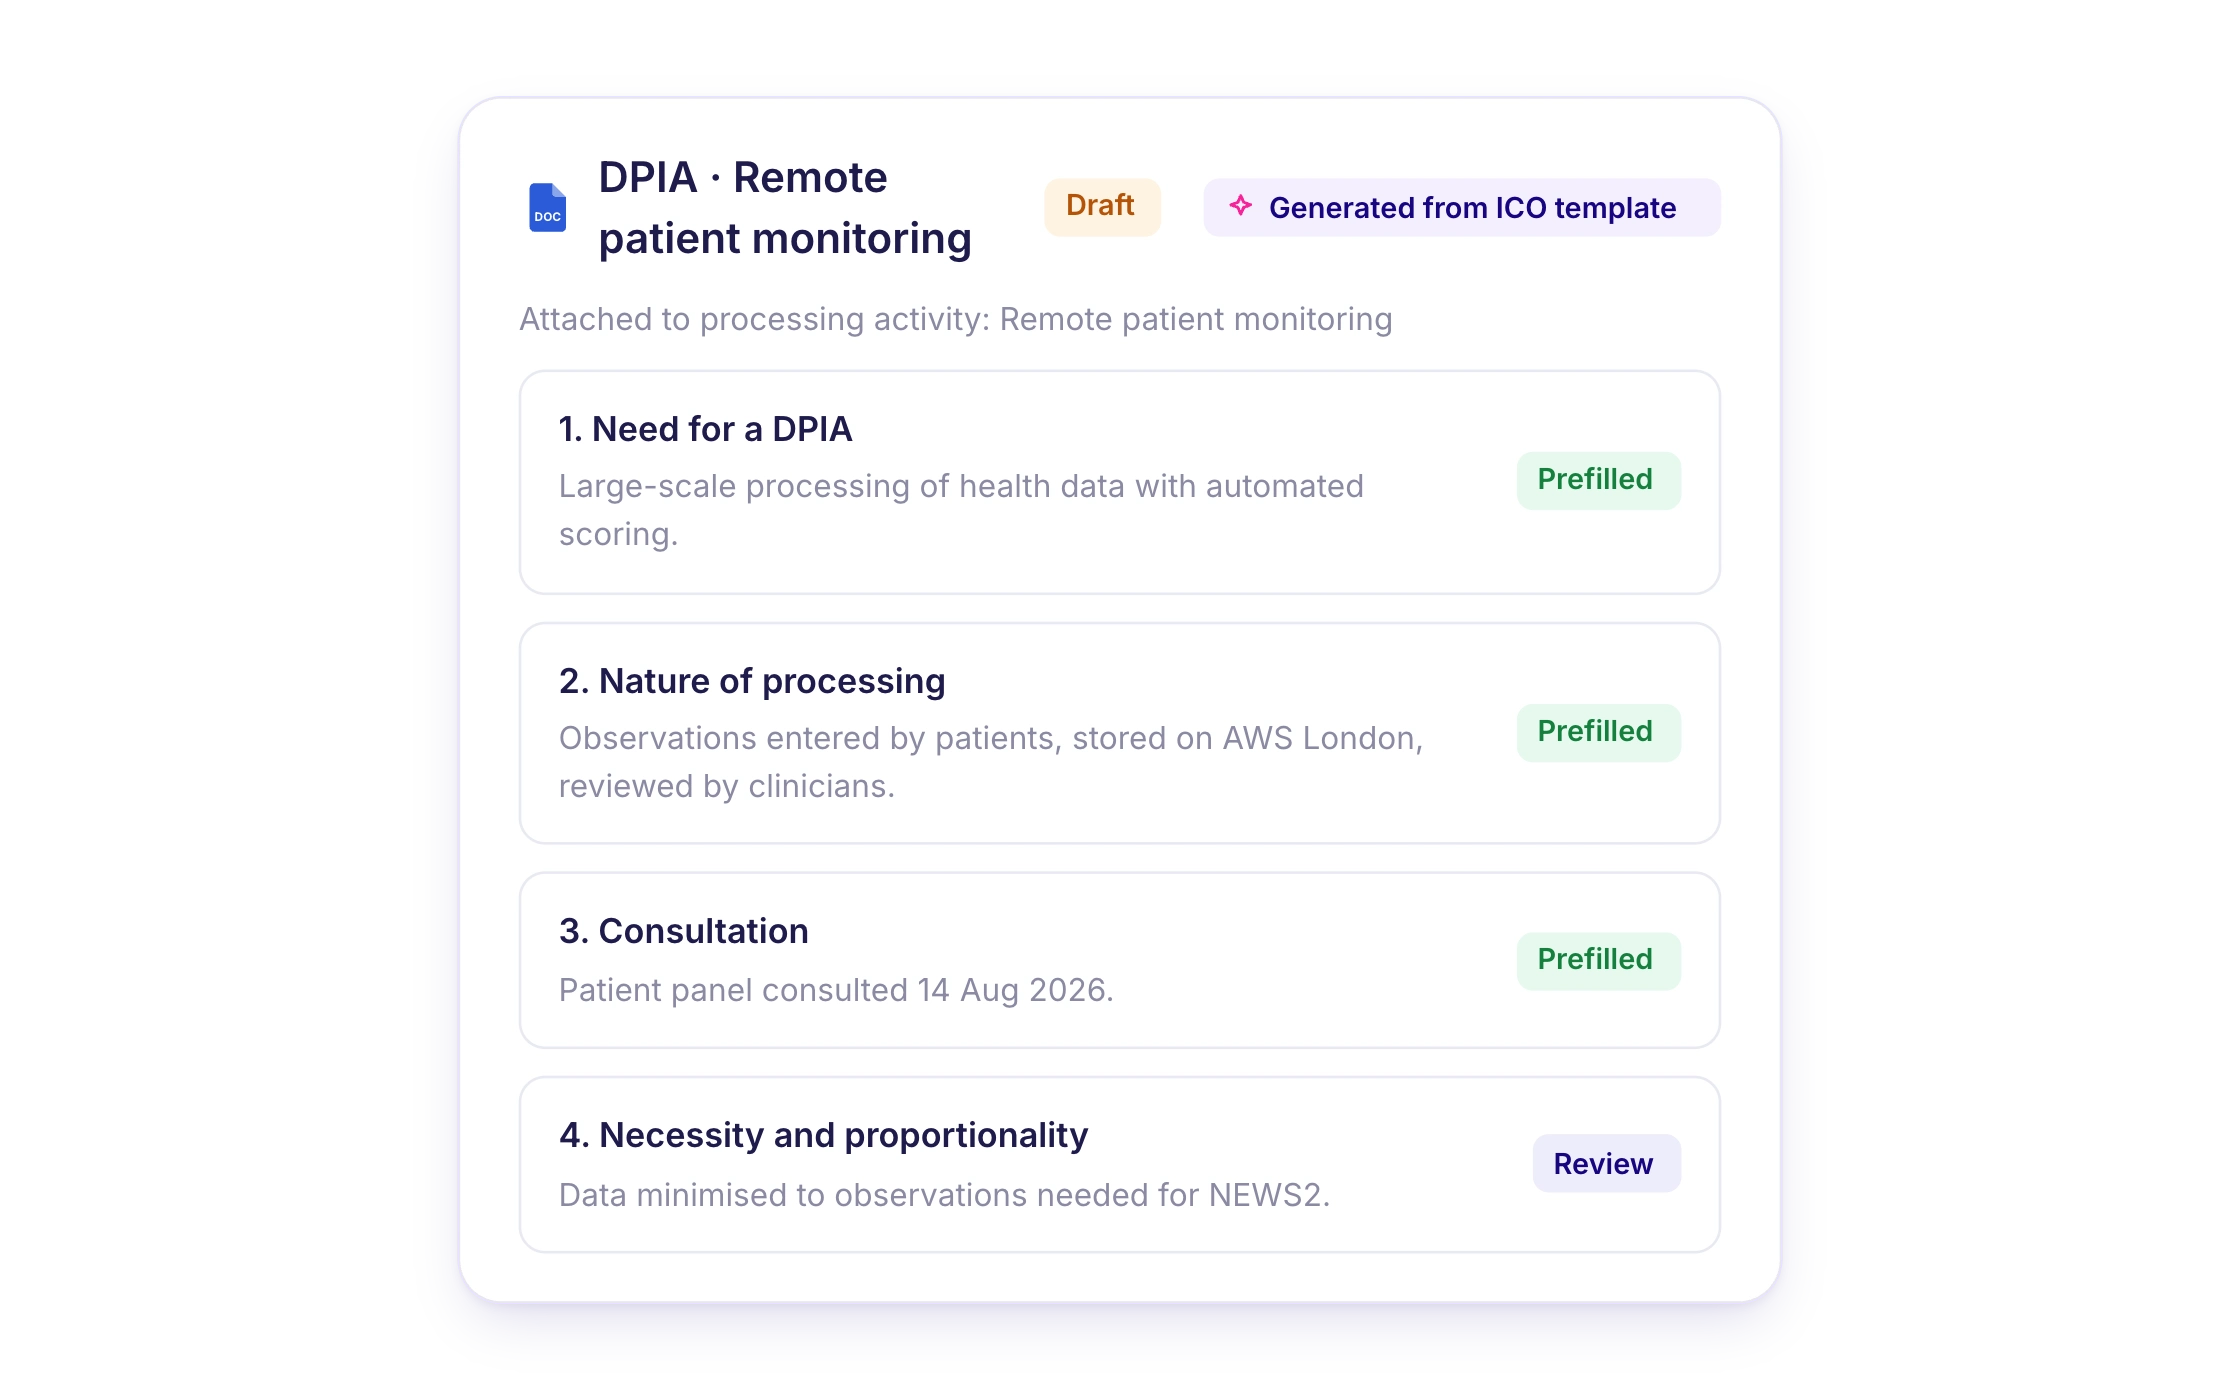
Templates, automation and AI take care of the repetitive work, so keeping your RoPA, DPIAs and policies current takes minutes, not a quarterly clean-up.
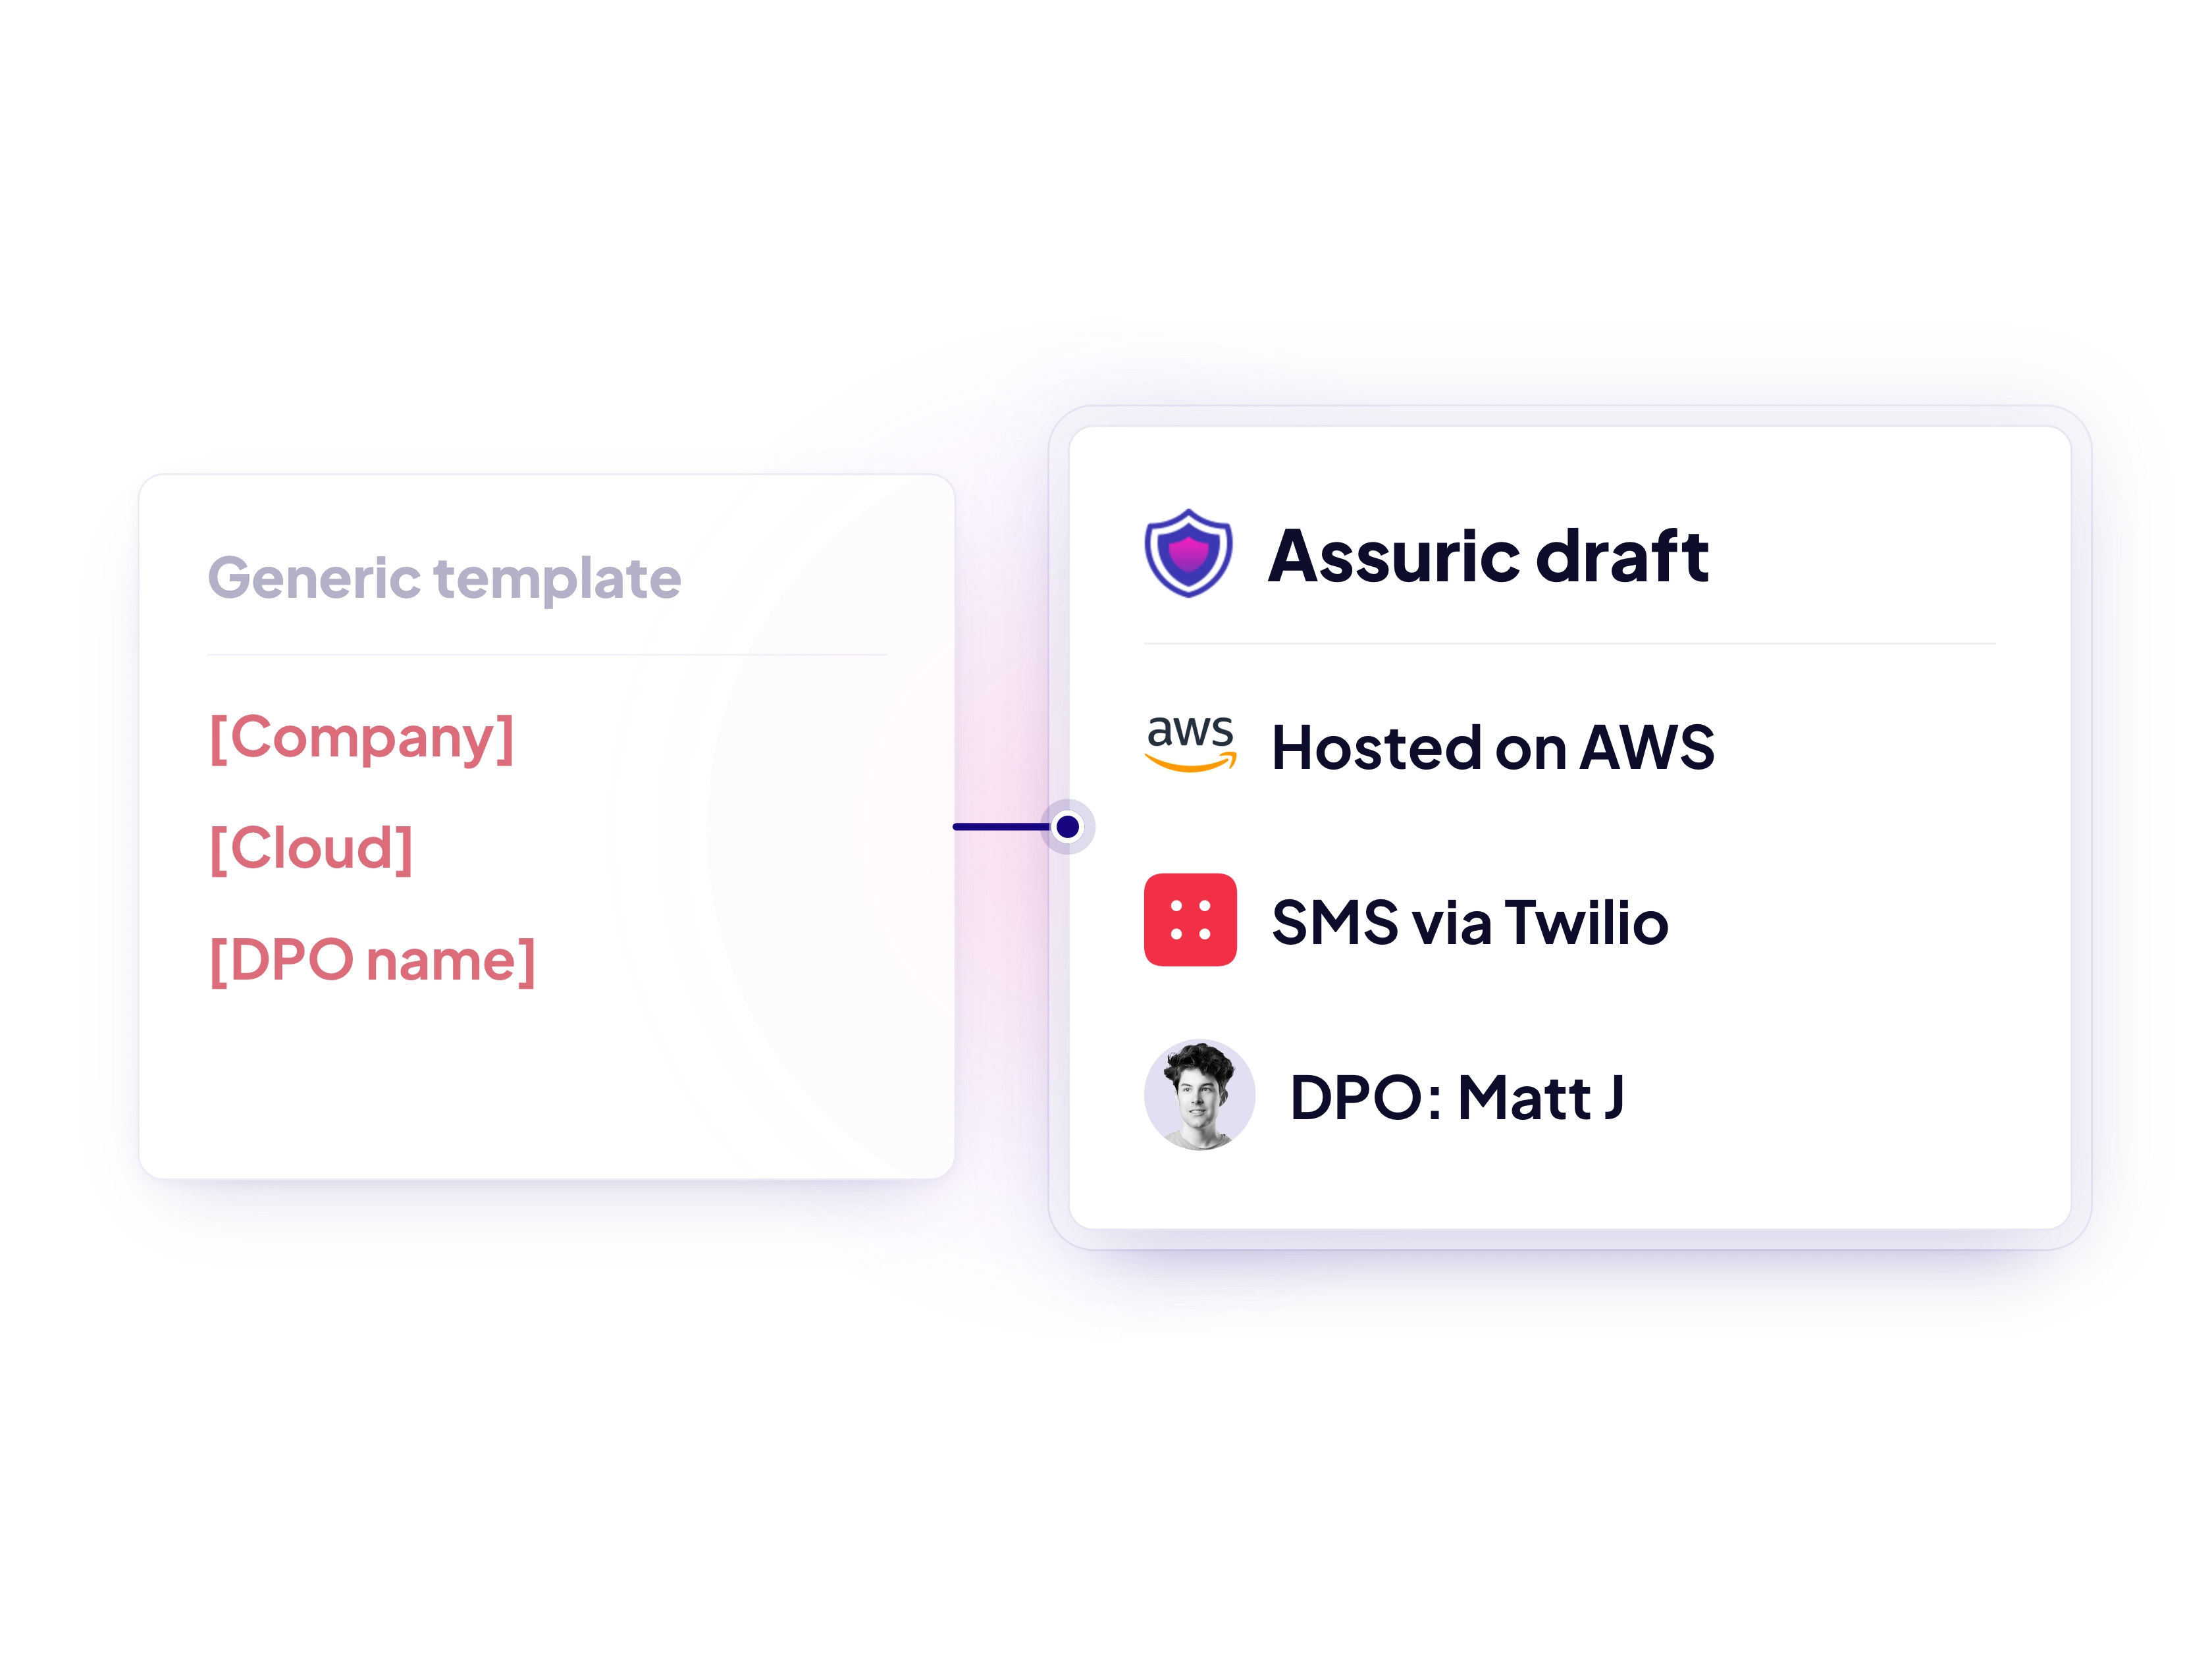
Assuric gives you the RoPA, DPIAs and DPO support to meet UK GDPR with health data, all in one place.
Trusted by data protection teams


Features
Automated compliance tracking
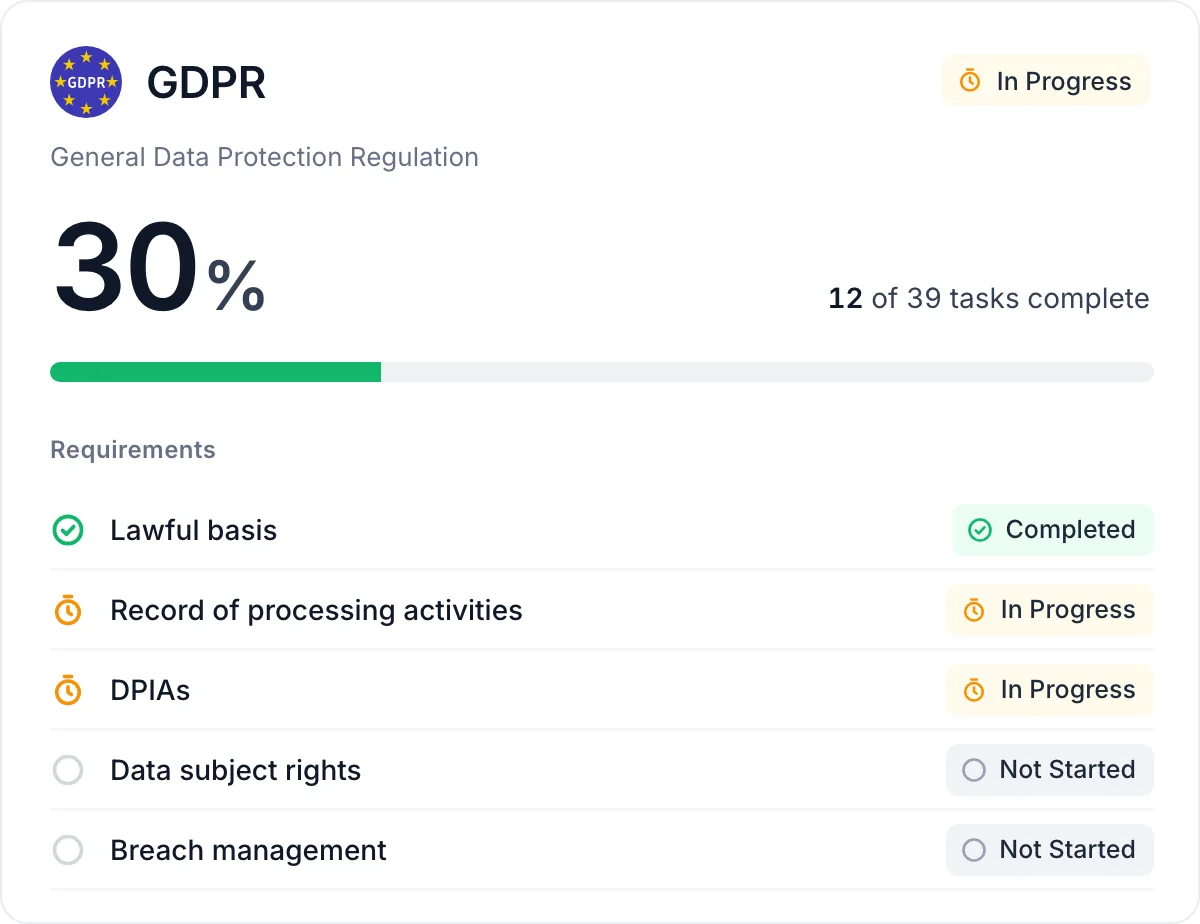
Fill any gaps, automate tasks, track compliance and get proactive alerts, so every requirement is met and stays met.
Document & policy management
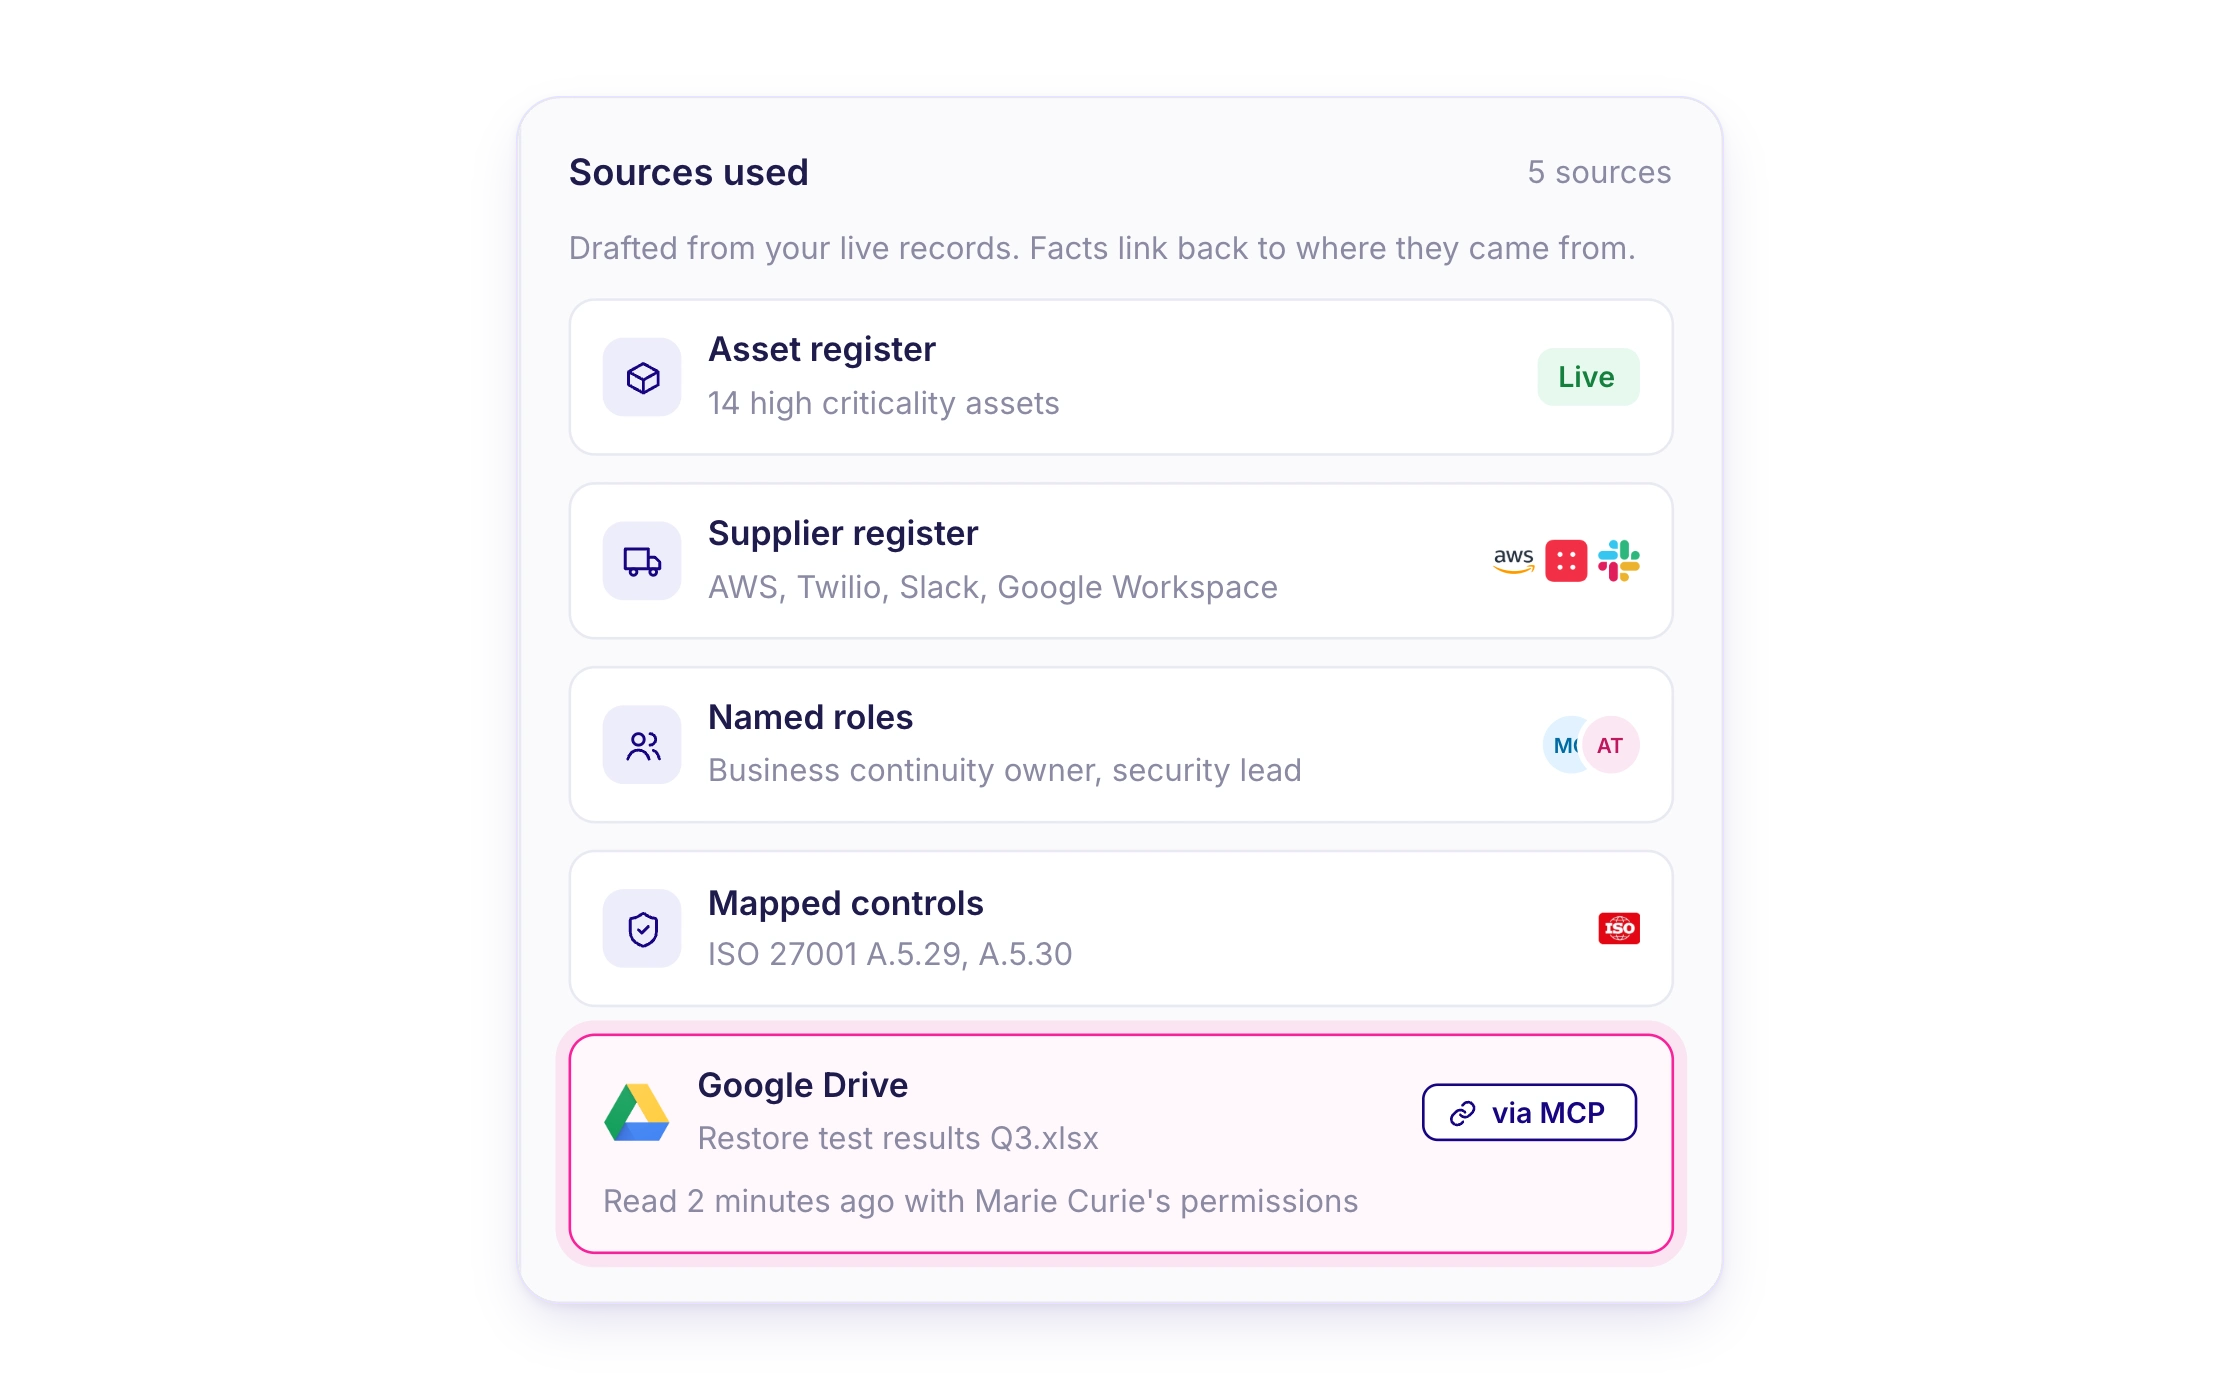
Create mandatory policies including automatic creation of Privacy Notices and Data Protection Impact Assessments.
DPIA, RoPA & risk management
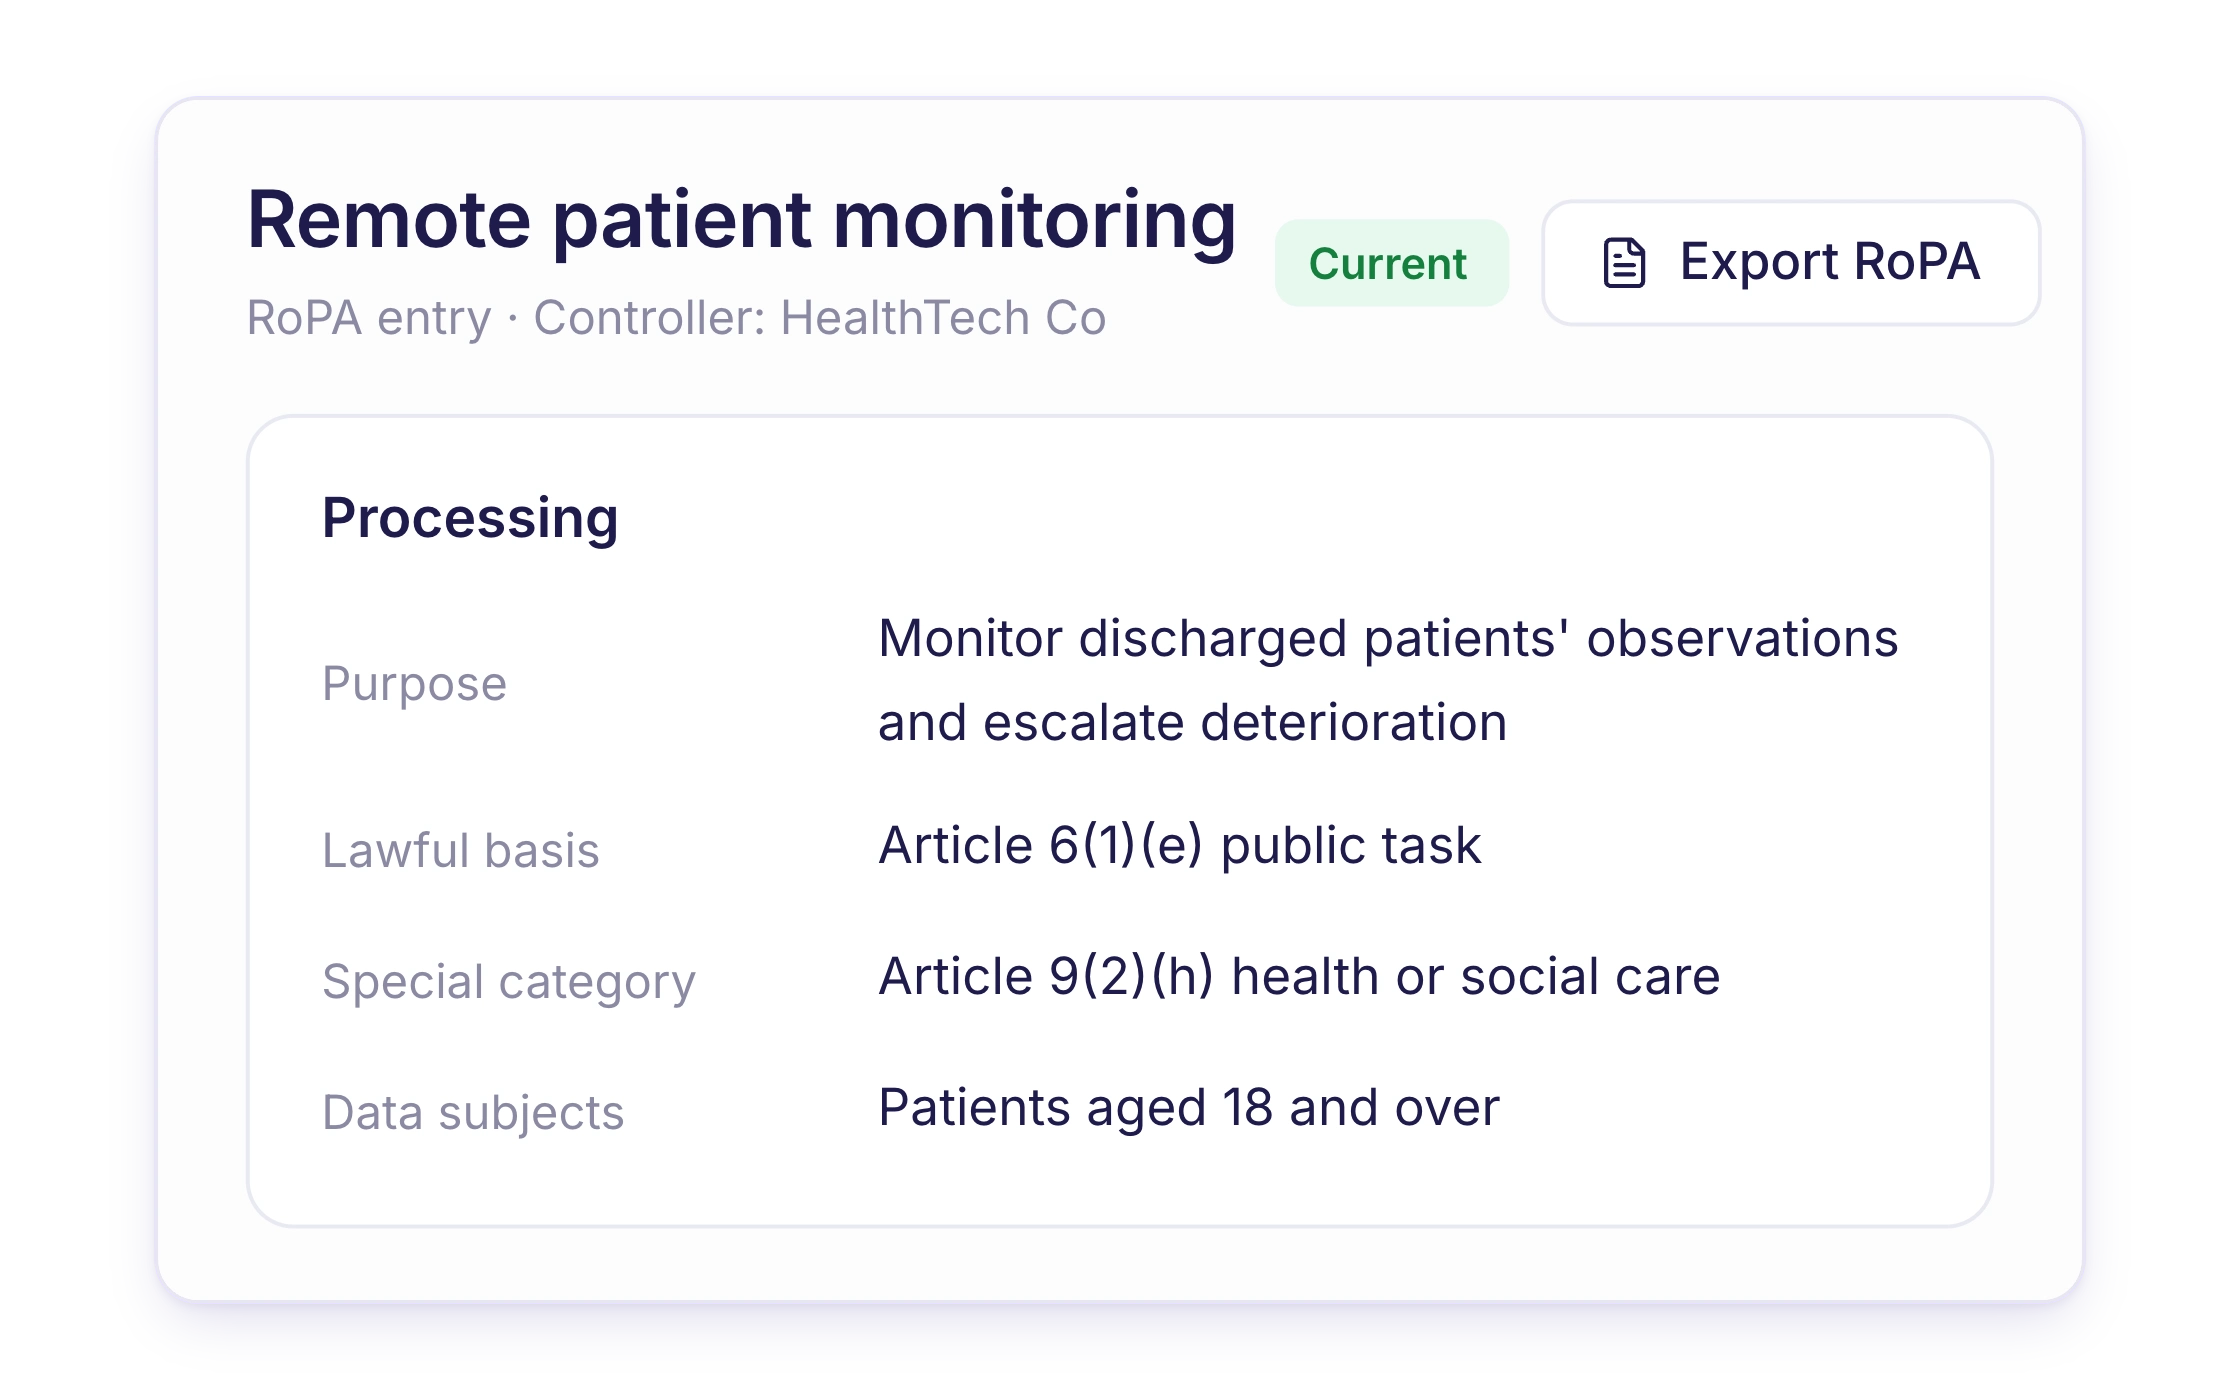
Document each processing activity with its purpose, lawful basis, special category condition, recipients and retention period, alongside the information assets it uses.
Third-party supplier management
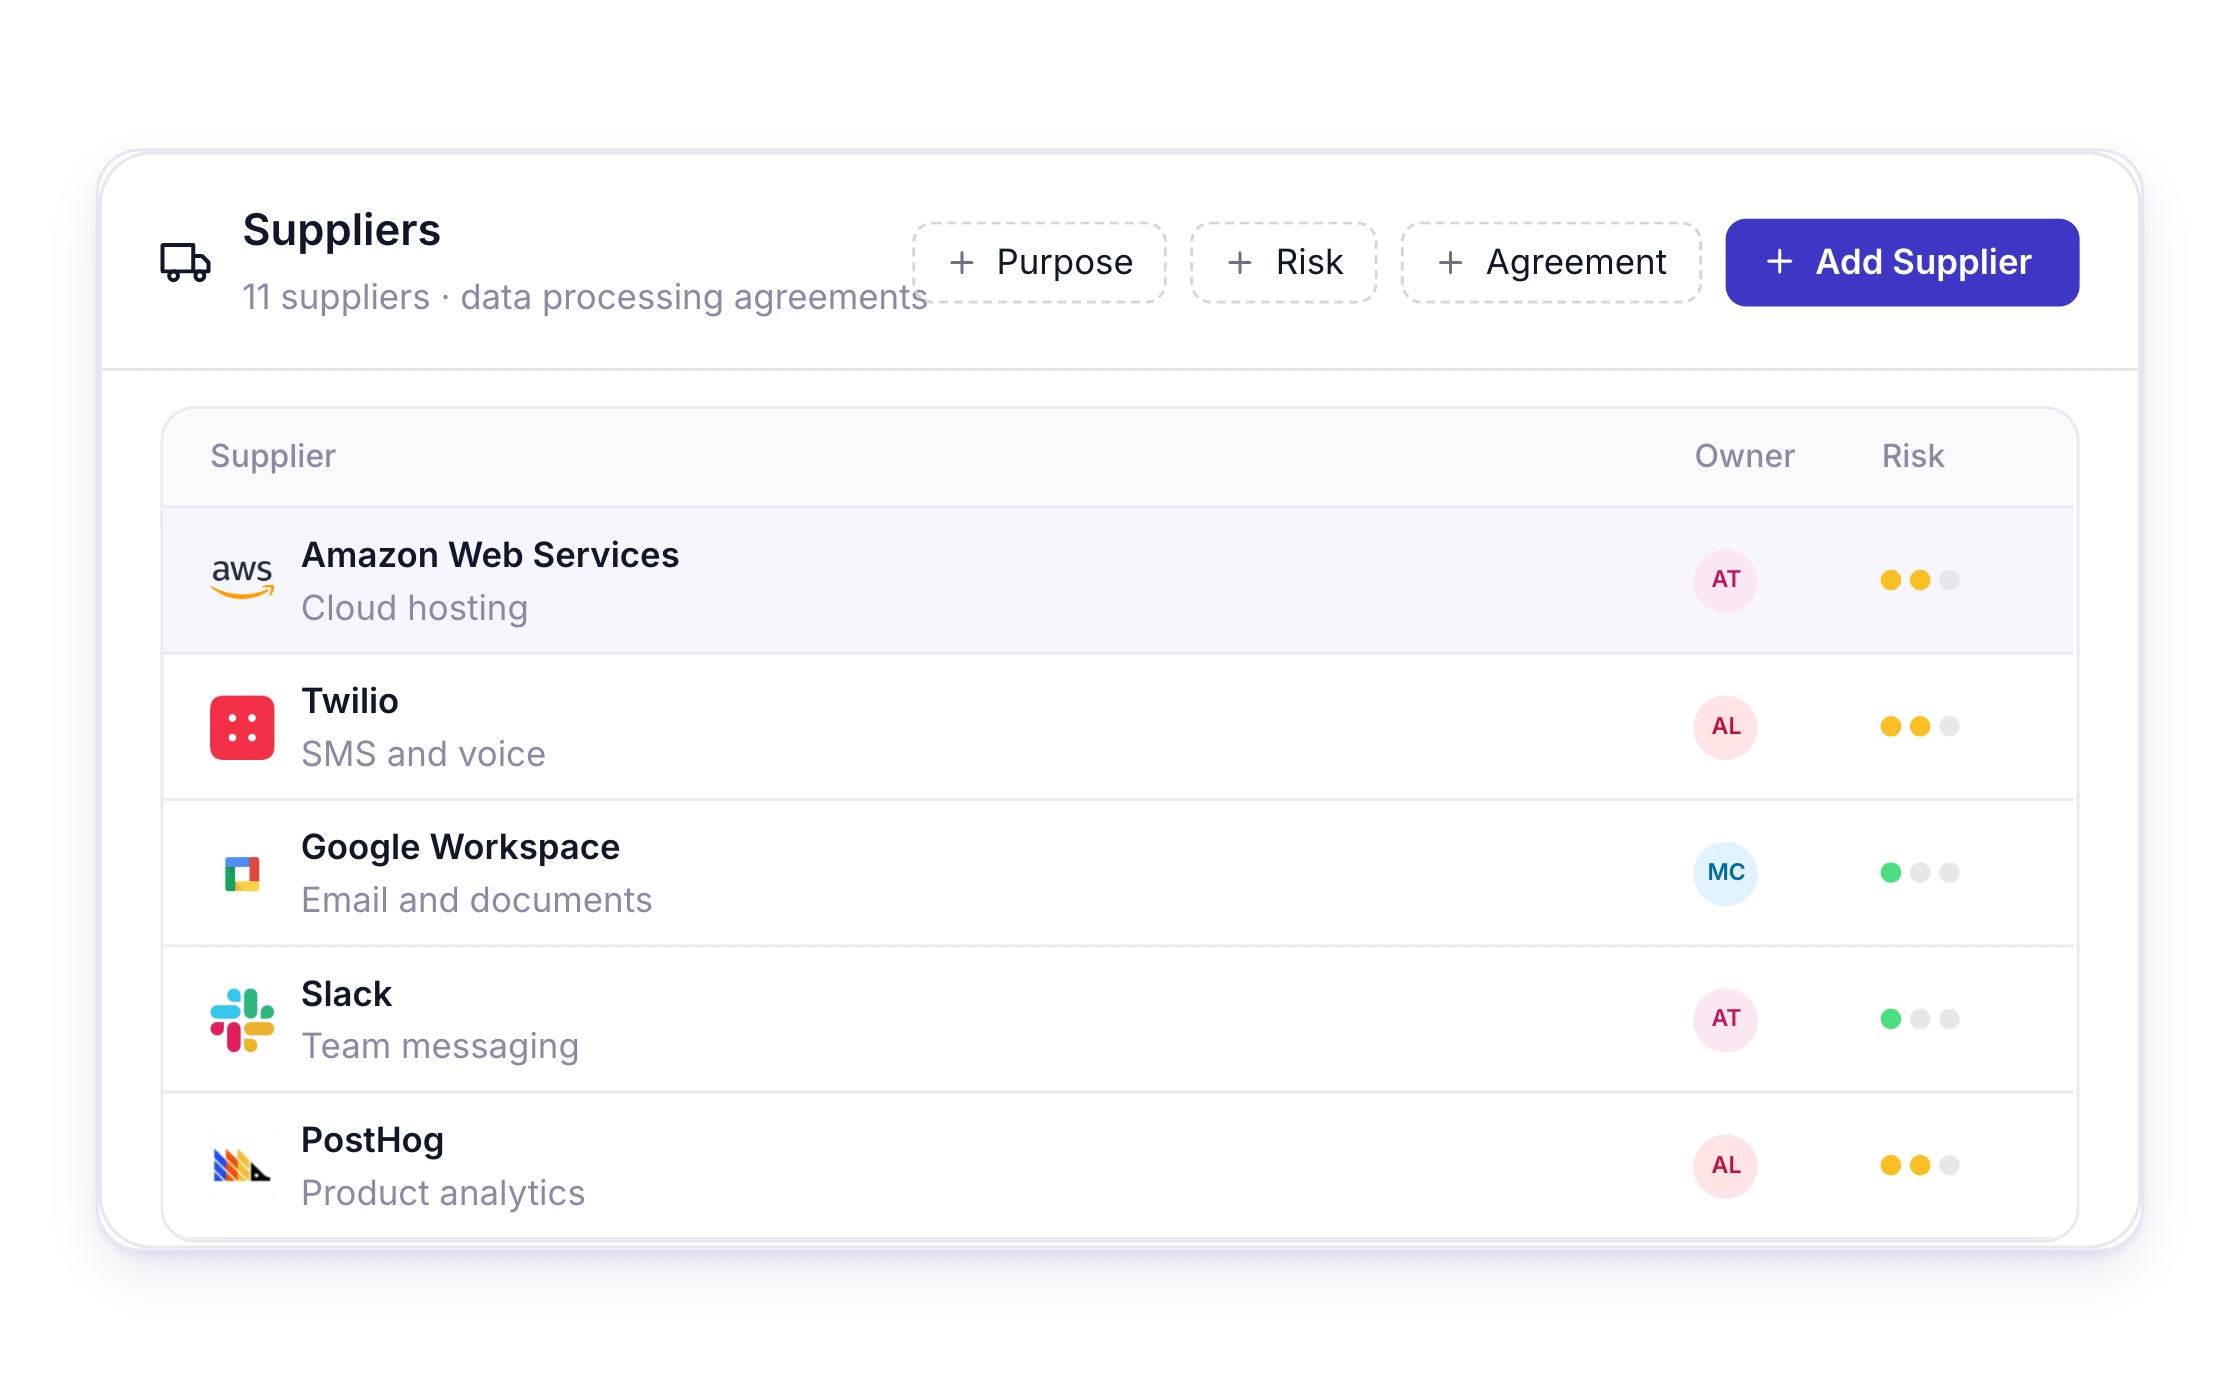
Record all third party suppliers and sub-processors who process or store personal data on behalf of your organisation, and make sure they meet your data protection requirements.
Benefits
Templates, automation and AI take care of the repetitive work, so keeping your RoPA, DPIAs and policies current takes minutes, not a quarterly clean-up.
Know exactly what personal data you process, why, where it goes and how long you keep it, without chasing colleagues for answers.
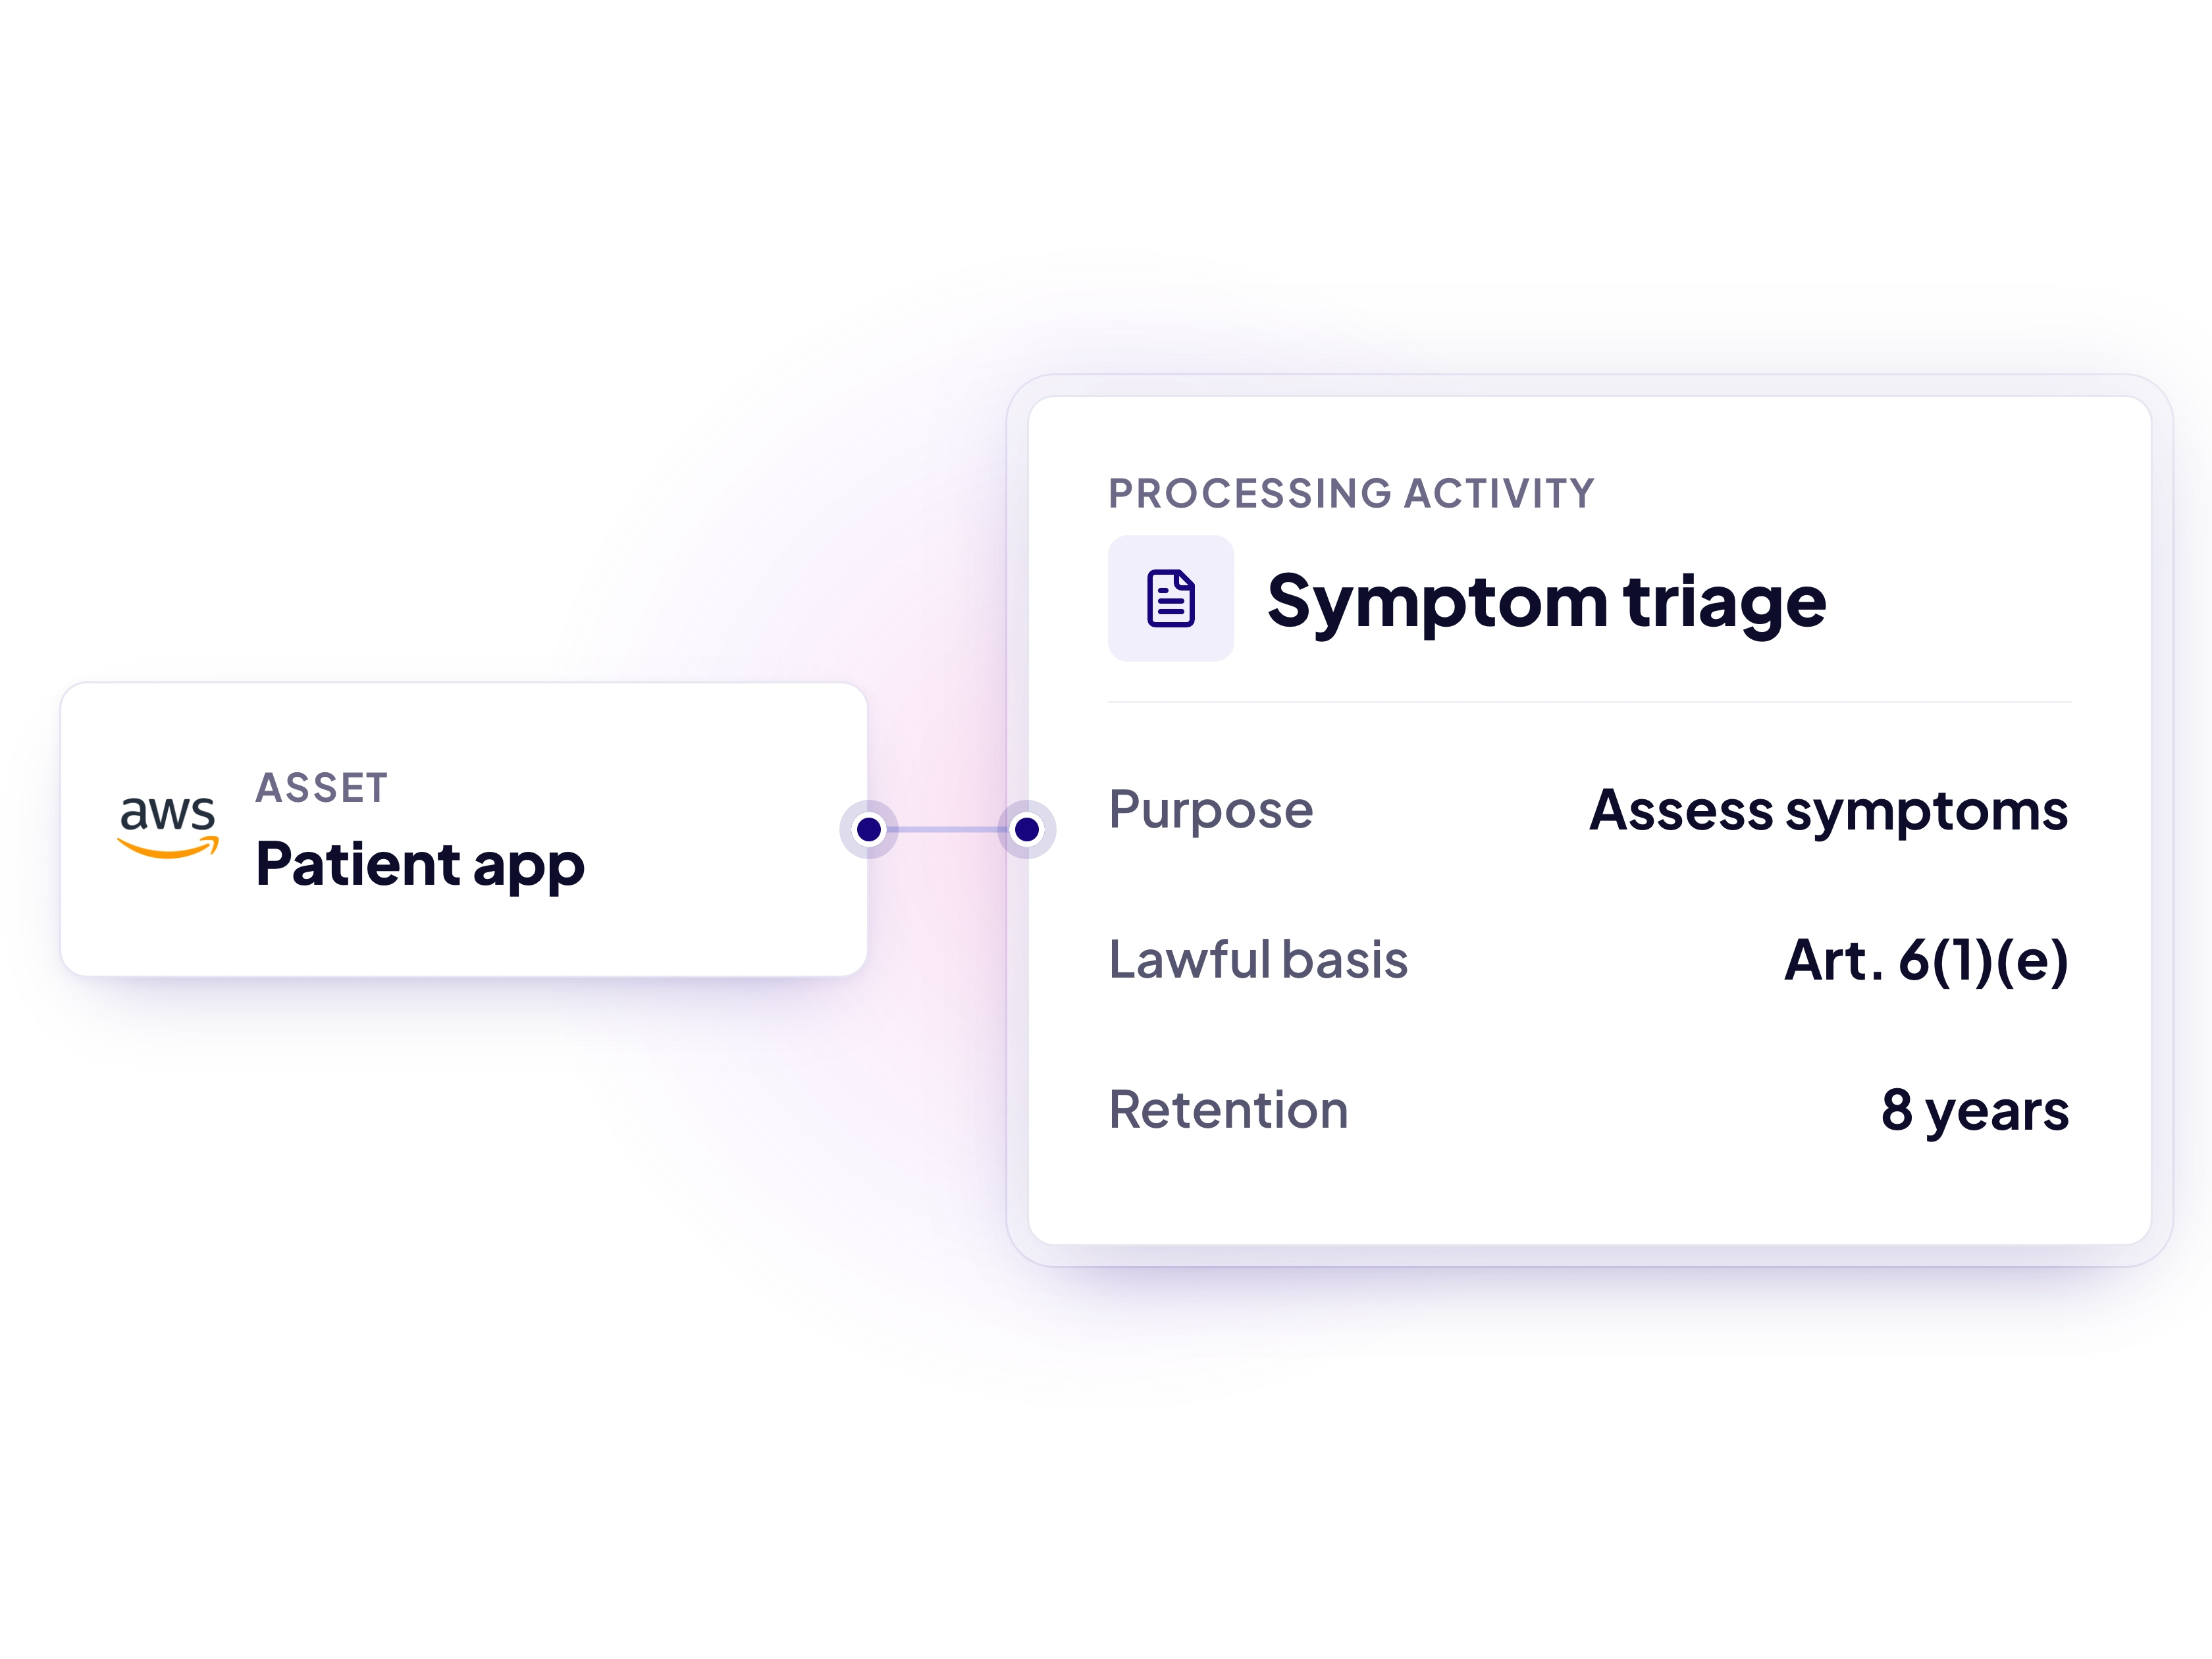
Spot high-risk processing early, with DPIAs and risks linked to each activity, so issues are dealt with before they reach a regulator.
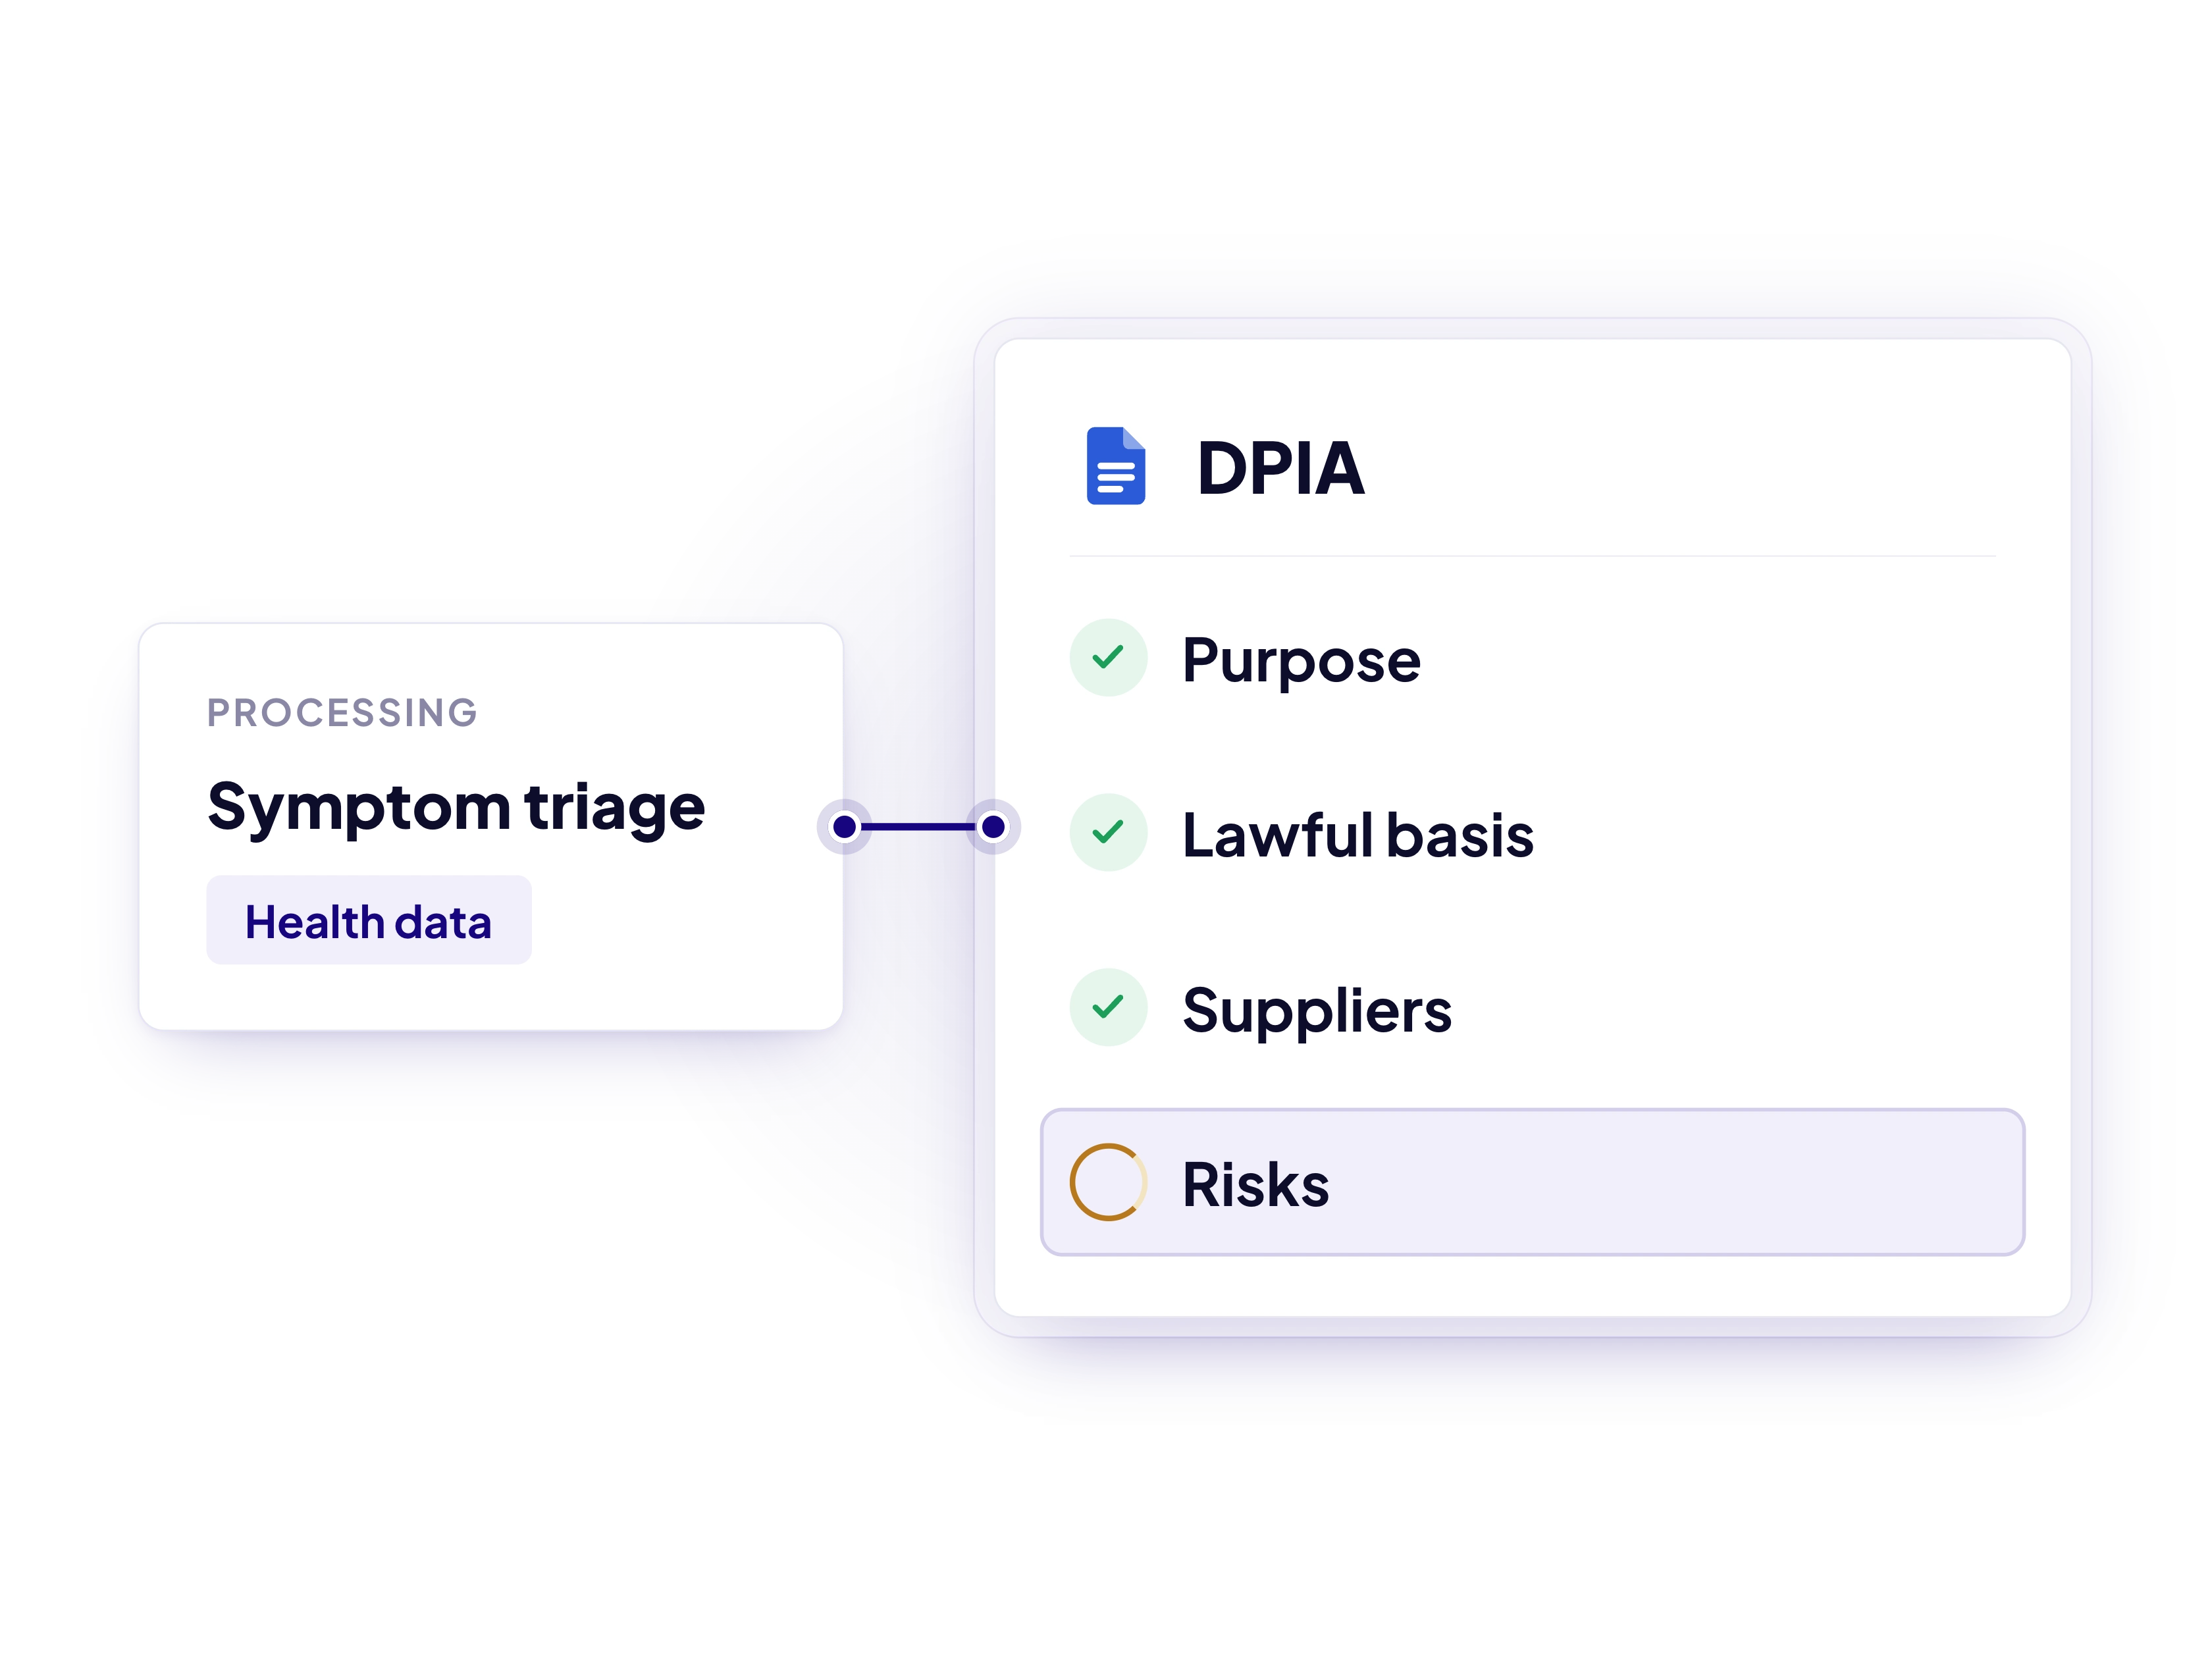
Have your RoPA, DPIAs and supporting evidence ready when an NHS buyer, the DSPT or an assessor asks, rather than pulling them together at the last minute.
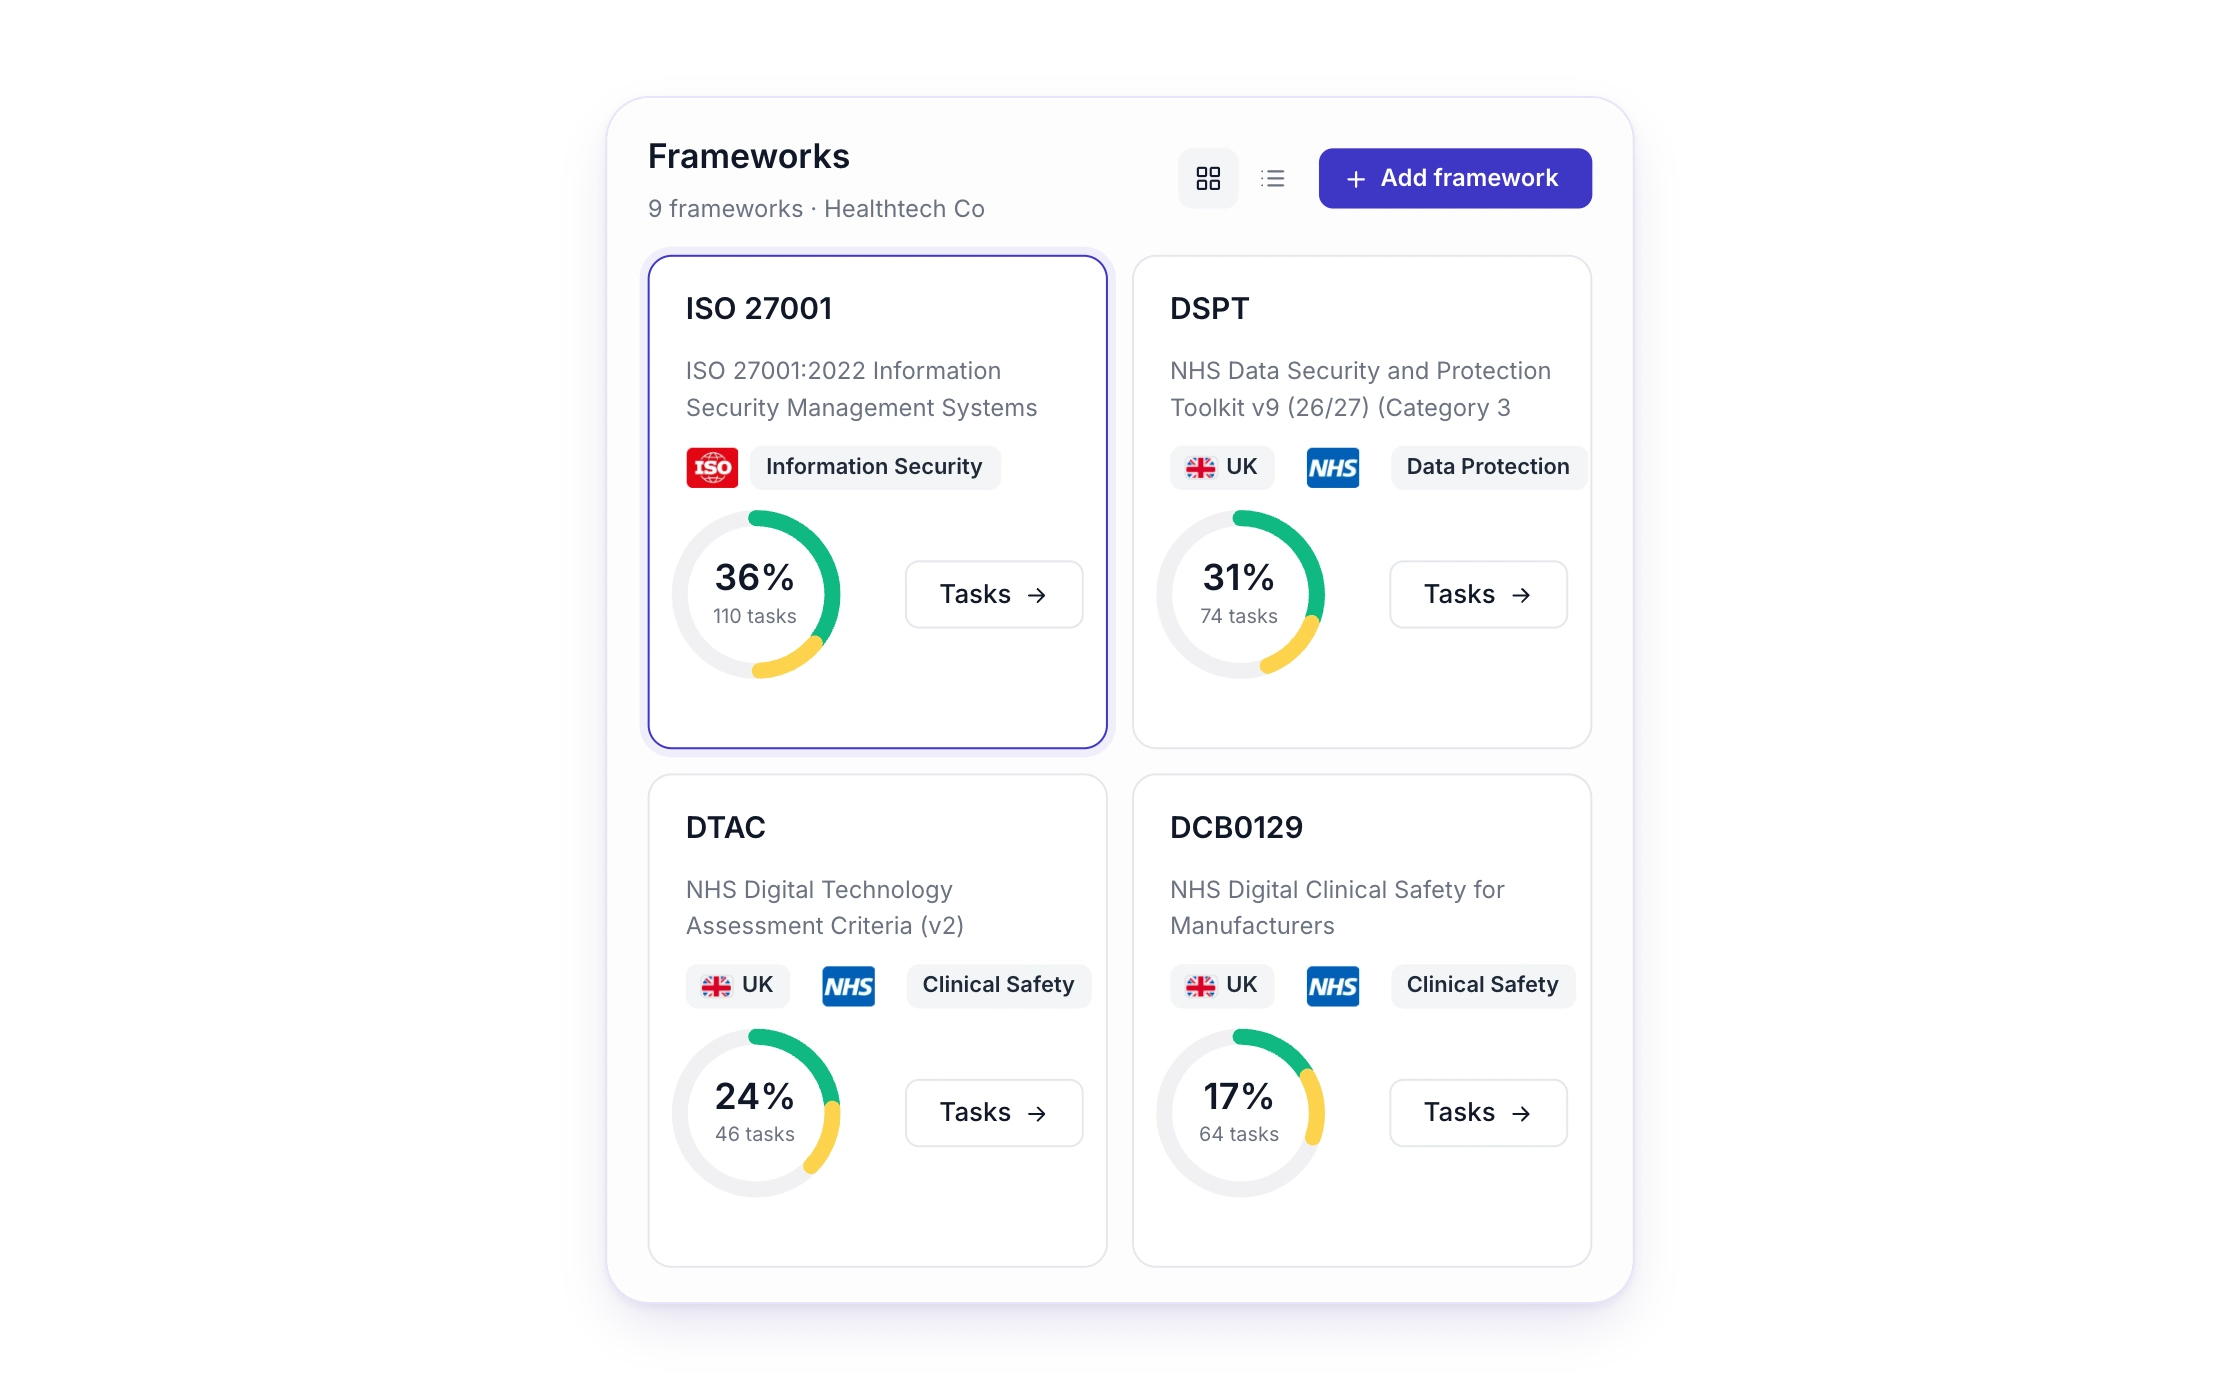
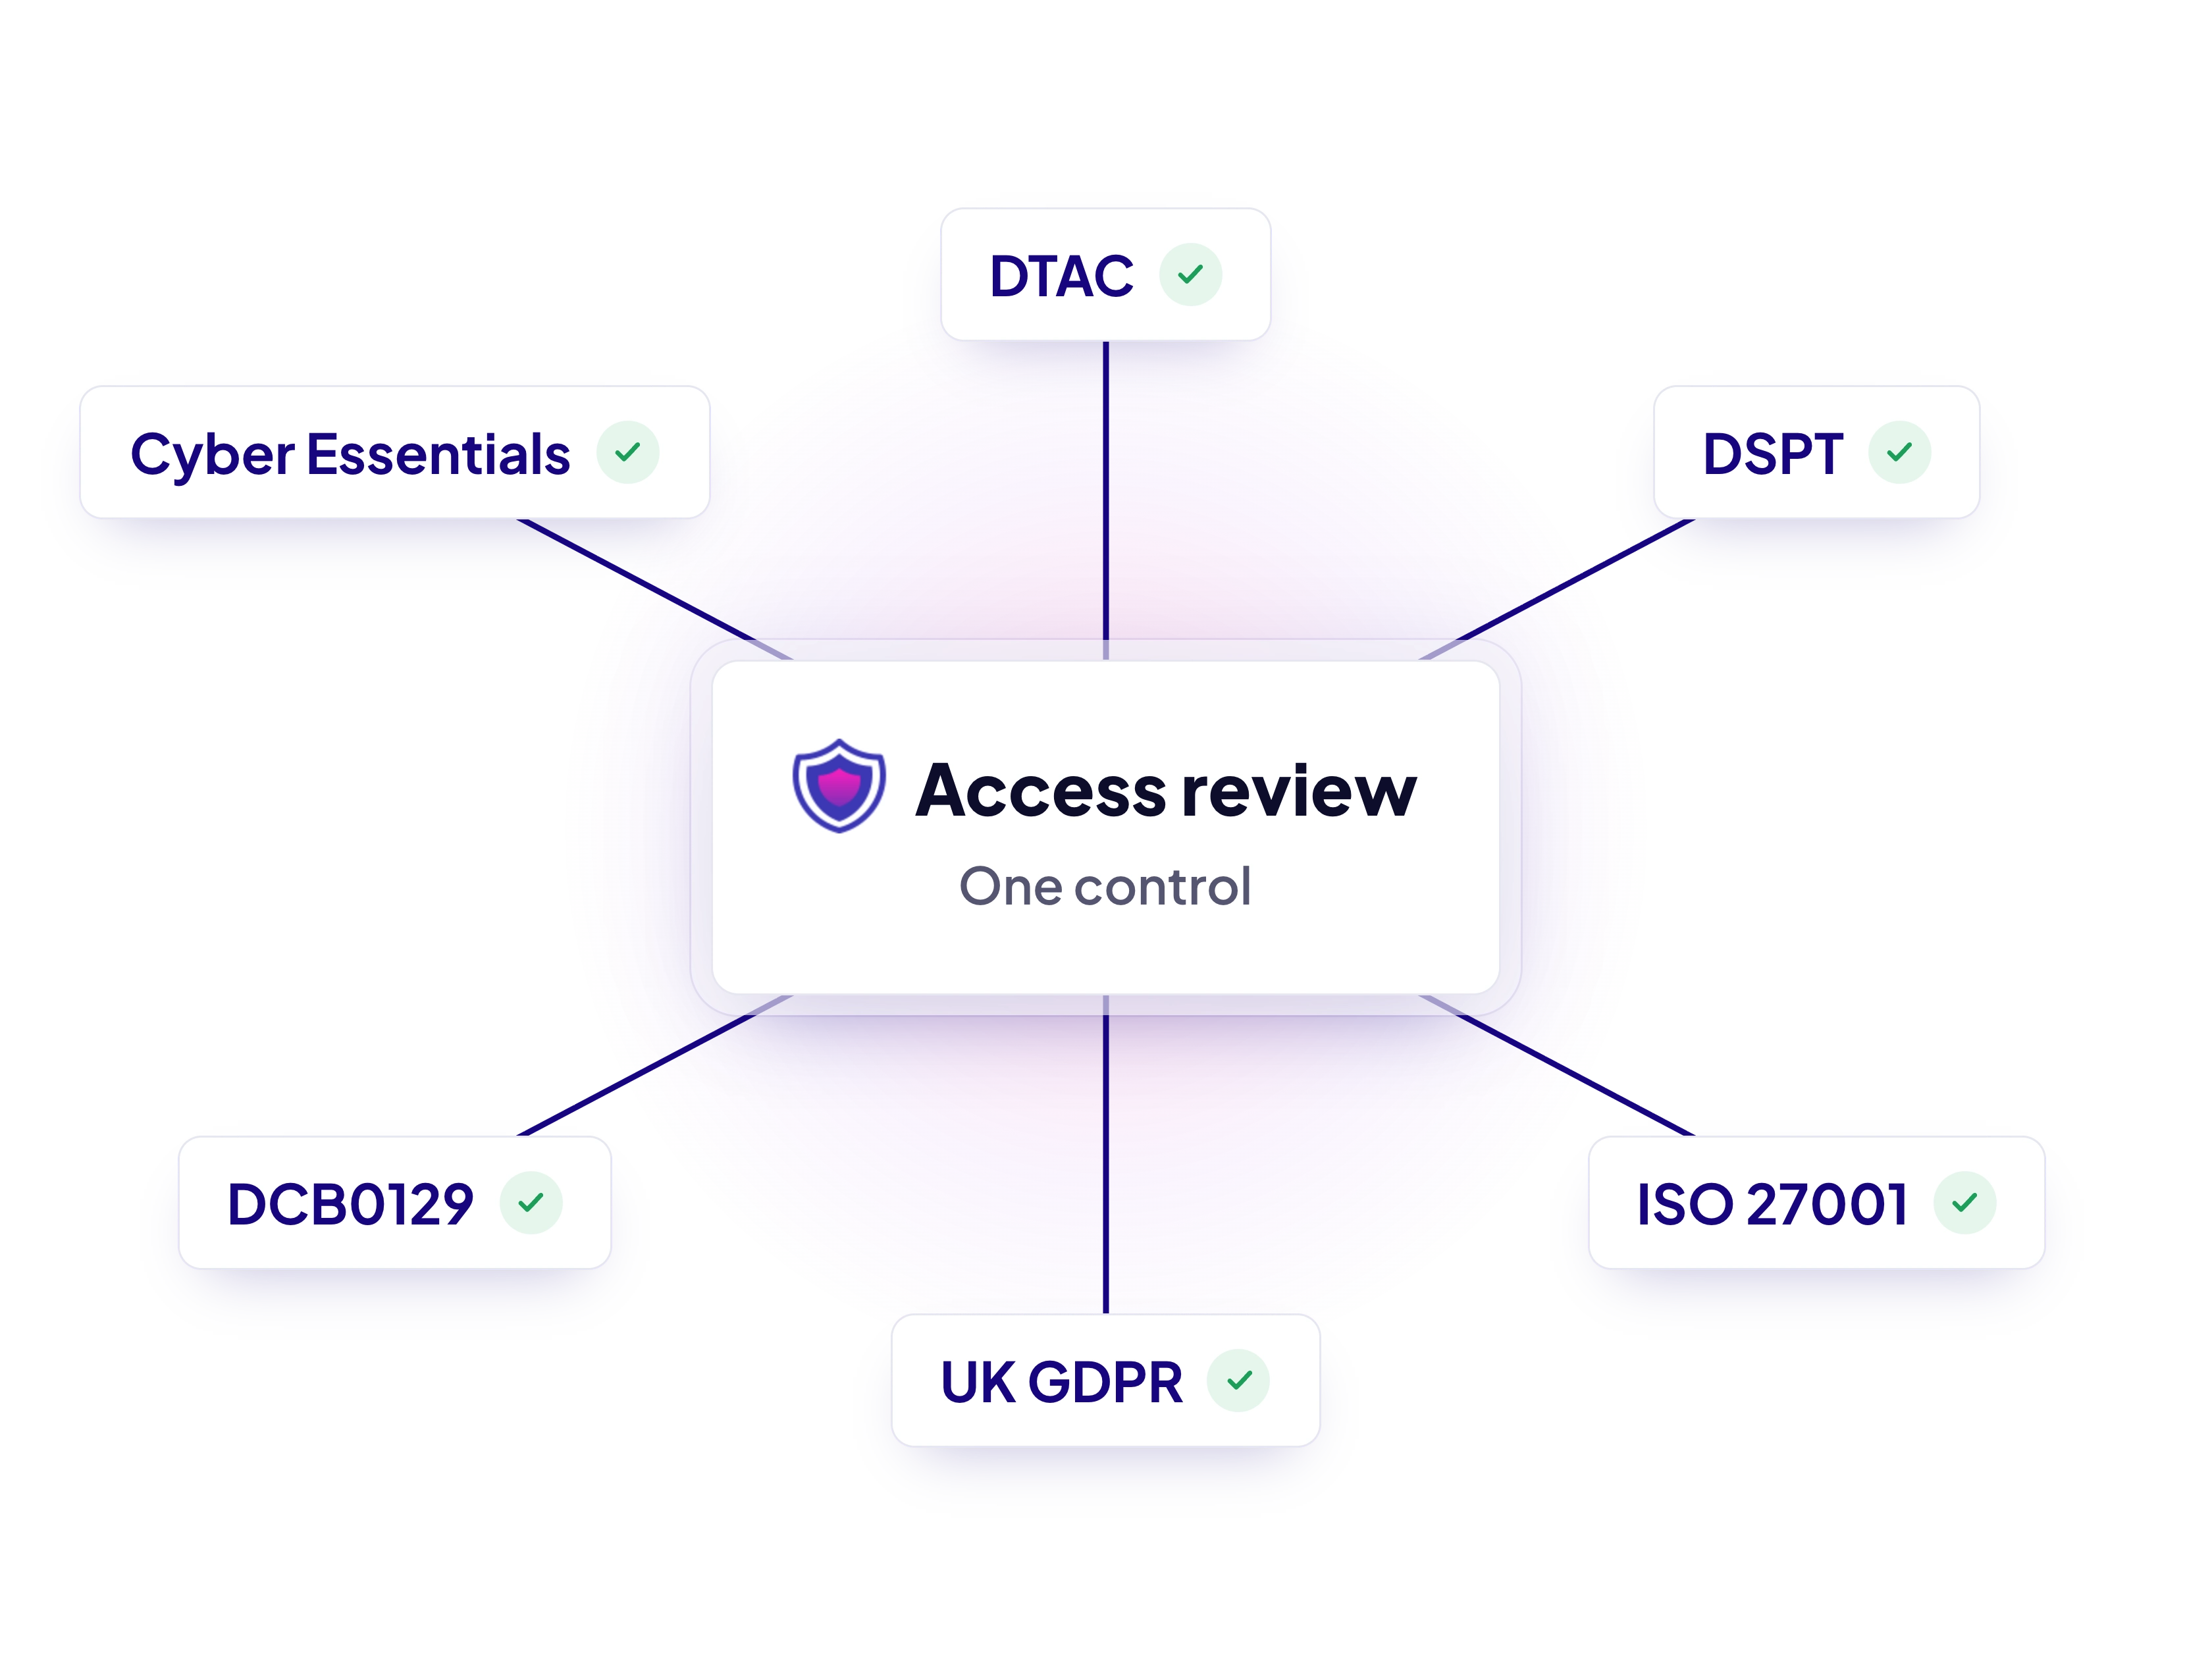
Cover UK GDPR alongside the DSPT, DTAC, ISO 27001 and more, reusing evidence across frameworks instead of starting again.
Assuric’s AI and automation take care of the routine data protection work, so your DPO’s time goes on expert advice, not admin.
Frameworks
Overlapping requirements and evidence are mapped across frameworks automatically, so you never do the same work twice.

“We couldn't speak highly enough of both the Assuric team and the platform itself, which is incredibly easy to use, and with the skill and hardworking nature of the Assuric team. They've been a key component in accelerating our progress and deployments!”
Maks Kozarzewski
COO, VitVio

“The Assuric platform is a game changer in the clinical risk management field. It has been carefully designed to make the job of a CSO significantly more streamlined. The team are excellent and responsive to any product suggestions I have requested, and it has been a pleasure to work with them.”
Paul Llewellyn
CCIO, Accenture

“Assuric has been fantastic in helping us quickly and safely navigate regulatory compliance in the UK. From completing Cybersecurity requirements to DSPT, DCB0129, and DTAC, the team was supportive, extremely knowledgeable, and the platform made everything quick and straightforward. A separate regulatory company we consulted at the beginning even remarked on how quickly we achieved compliance!”
Katie Baker
Director UK & Ireland, Tandem
UK GDPR, alongside the Data Protection Act 2018, is the law that governs how organisations in the UK process personal data. If your healthtech business processes personal data, such as patient or staff information, it applies to you. If you also process the personal data of people in the EU, the EU GDPR can apply too.
Fines are imposed by the data protection regulator: the Information Commissioner's Office (ICO) in the UK, and national supervisory authorities in the EU. The most serious breaches can lead to fines of up to £17.5 million under UK GDPR, or €20 million under EU GDPR, or 4% of annual global turnover if higher. Other infringements, such as failing to keep records or report a breach, carry a lower maximum of £8.7 million or €10 million, or 2% of turnover. Businesses may also face legal claims and reputational damage.
You must appoint a Data Protection Officer if you’re a public authority, if your core activities involve large-scale, regular and systematic monitoring of people, or if they involve large-scale processing of special category data such as health data. Most healthtech companies handling patient data meet that last test. The DPO oversees compliance, advises on processing and DPIAs, and is the point of contact for the regulator. Assuric offers fractional DPO services to meet this requirement cost-effectively.
Under UK GDPR, you must report a personal data breach to the ICO within 72 hours of becoming aware of it, unless it's unlikely to result in a risk to people's rights and freedoms. If the risk is high, you must also tell the people affected without undue delay. Our fractional DPOs guide you through breach assessments and any reporting to the ICO.
Under Article 35 of the UK and EU GDPR, a DPIA is required before any processing likely to result in a high risk to people’s rights and freedoms, for example large-scale processing of health data or new technology that uses personal data. Most healthtech products meet that test, and NHS buyers ask for a DPIA through DTAC regardless. Where it isn’t strictly required, it’s still good practice for any product that processes personal data.
Health data is special category data, so as well as a lawful basis under Article 6, you need a condition under Article 9. Explicit consent is one option, but healthtech companies often rely on others, such as the provision of health or social care. In the UK, most of these conditions also need a matching condition from Schedule 1 of the Data Protection Act 2018. You’ll usually need a DPIA, along with appropriate security, strict access controls and clear records of your processing. If you work with the NHS, you’ll also need to complete the Data Security and Protection Toolkit (DSPT), which checks your data protection and security practices against NHS standards.
It is important to be clear that being a data processor or controller is activity based, not company based. For example, every company will be a controller for employee information. Controllers are the main decision-makers. They have overall control over the purposes and means of the processing of personal information and data. If two or more controllers jointly determine the purposes and means of the processing of the same personal information, they are joint controllers. However, they are not joint controllers if they are processing the same data for different purposes. Processors act on behalf of, and only on the instructions of, the relevant controller. Our experts can help advise you on this.
Yes, in some cases. The EU GDPR applies to an organisation outside the EU if it offers goods or services to people in the EU, or monitors their behaviour there, for example by tracking how they use an app. What matters is where the people are, not their nationality or where the data is stored. A UK company serving patients in the EU will usually need to meet the EU GDPR as well as the UK GDPR, and may need to appoint a representative in the EU.
Yes. After Brexit the EU GDPR was kept in UK law as the UK GDPR, which sits alongside the Data Protection Act 2018 and is enforced by the Information Commissioner’s Office (ICO). It has since been amended by the Data (Use and Access) Act 2025, so the UK and EU versions are now similar but no longer identical.
UK GDPR began as the EU GDPR retained in UK law after Brexit, and the core principles are the same. UK GDPR is enforced by the ICO, while the EU GDPR is enforced by each member state’s supervisory authority, coordinated by the European Data Protection Board (EDPB). The Data (Use and Access) Act 2025 has since changed the UK version. Most changes took effect on 5 February 2026, including recognised legitimate interests, more room for automated decision-making with safeguards, and "reasonable and proportionate" searches for subject access requests. Since 19 June 2026, controllers must also have a way to handle data protection complaints and acknowledge them within 30 days. International transfer rules also differ.
See how Assuric helps you meet GDPR for patient data, from your first DPIA to your next contract.