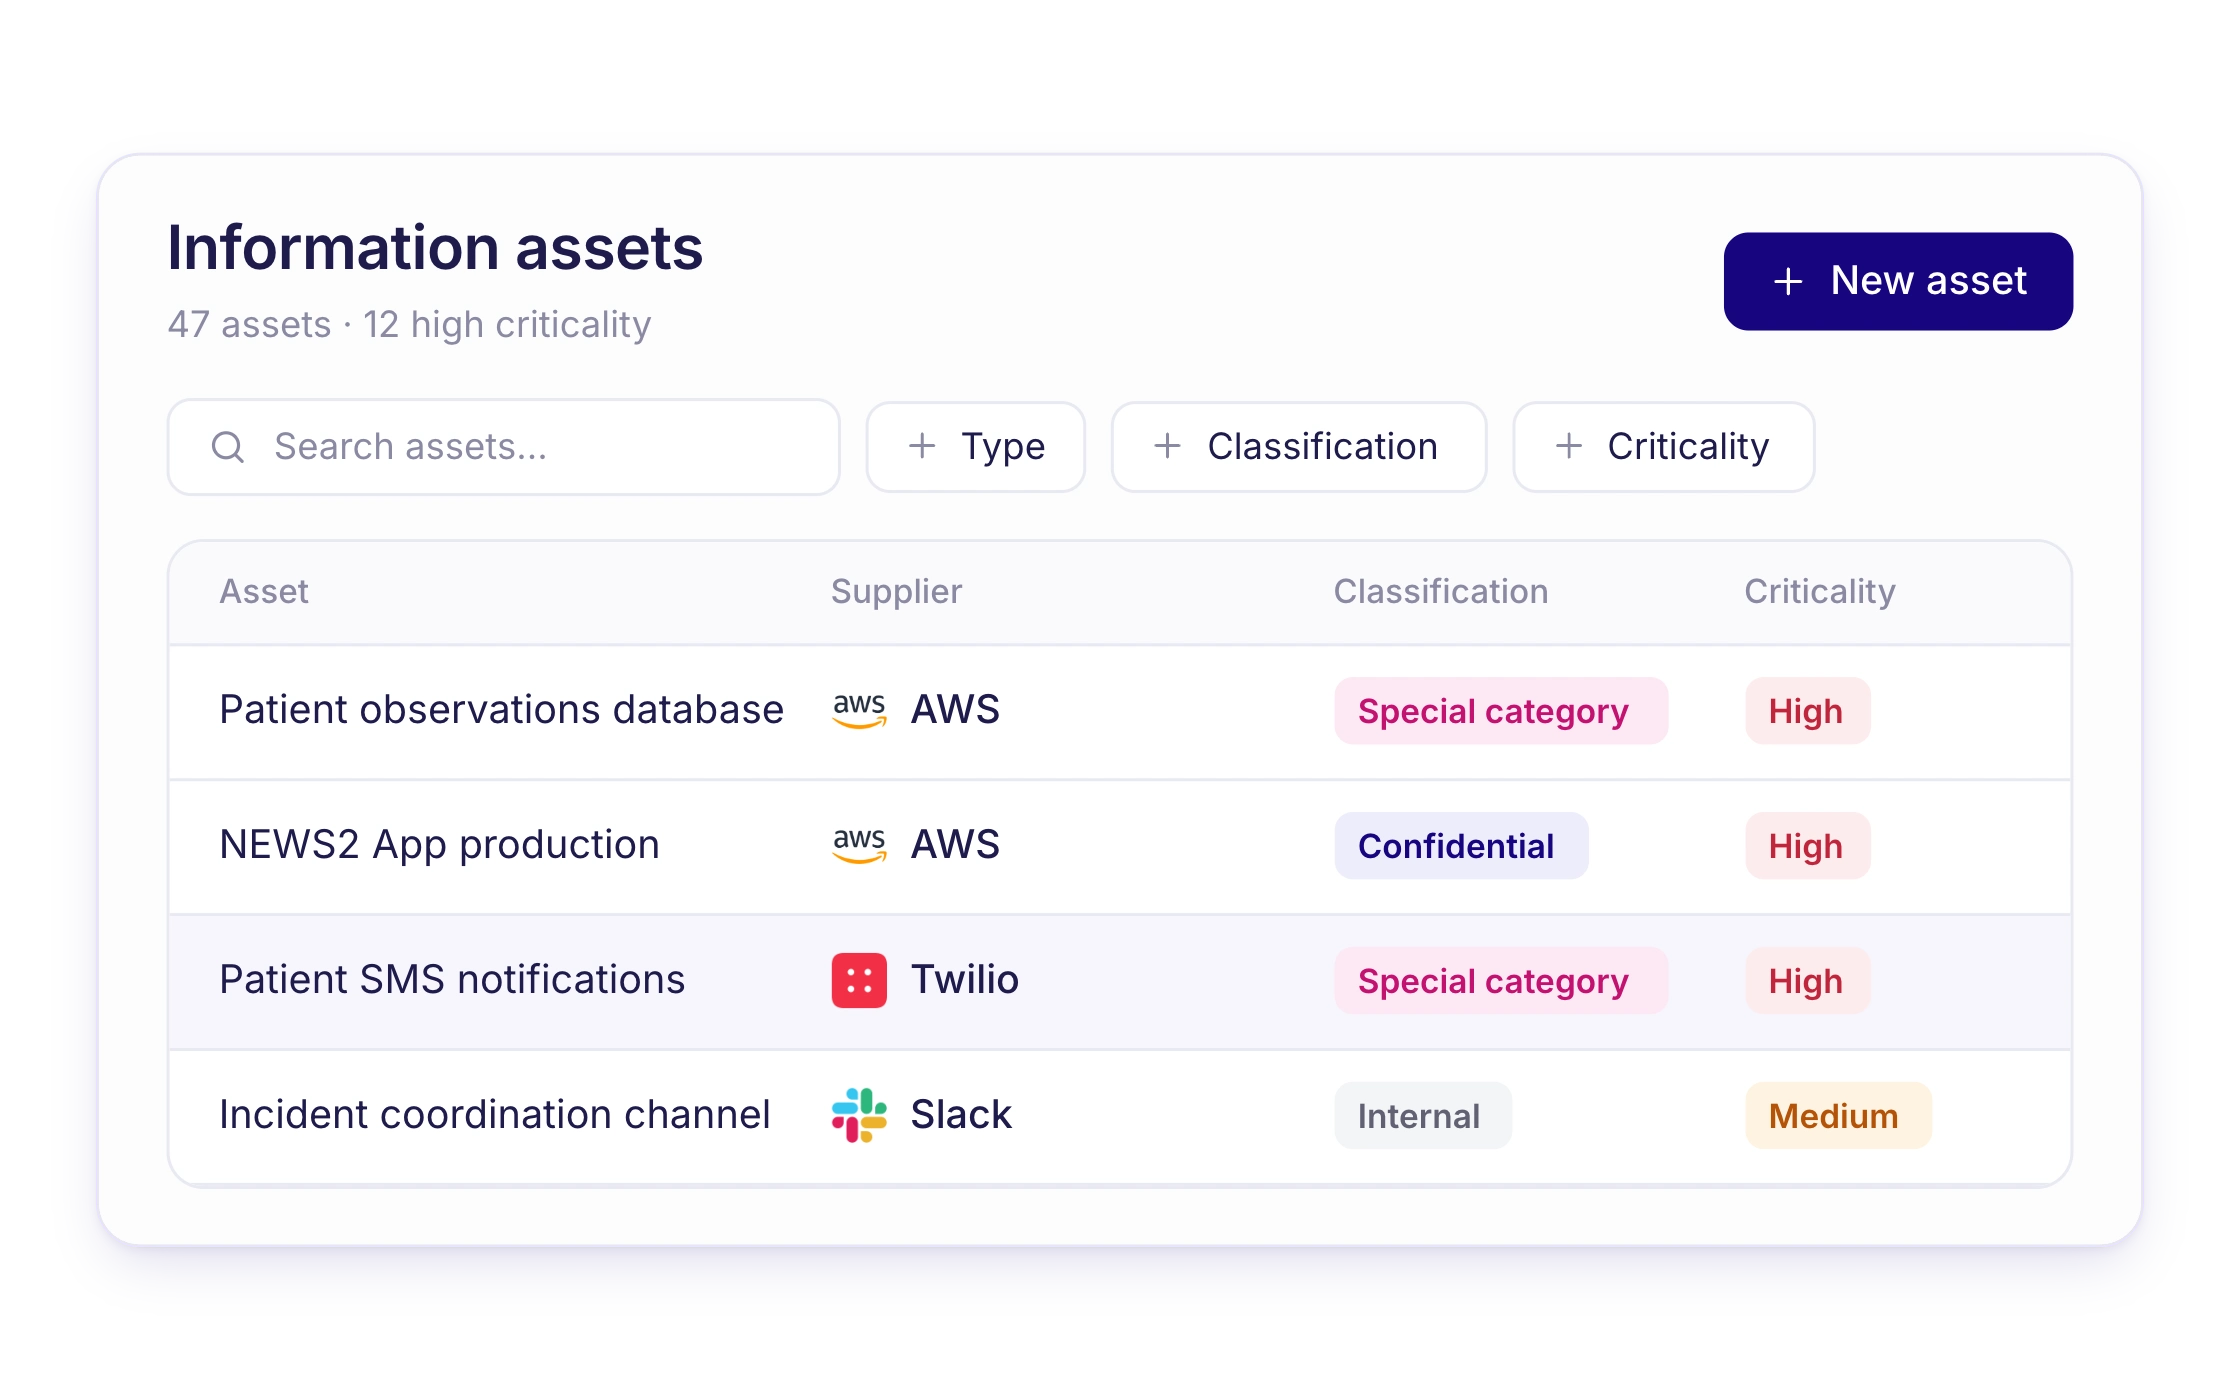
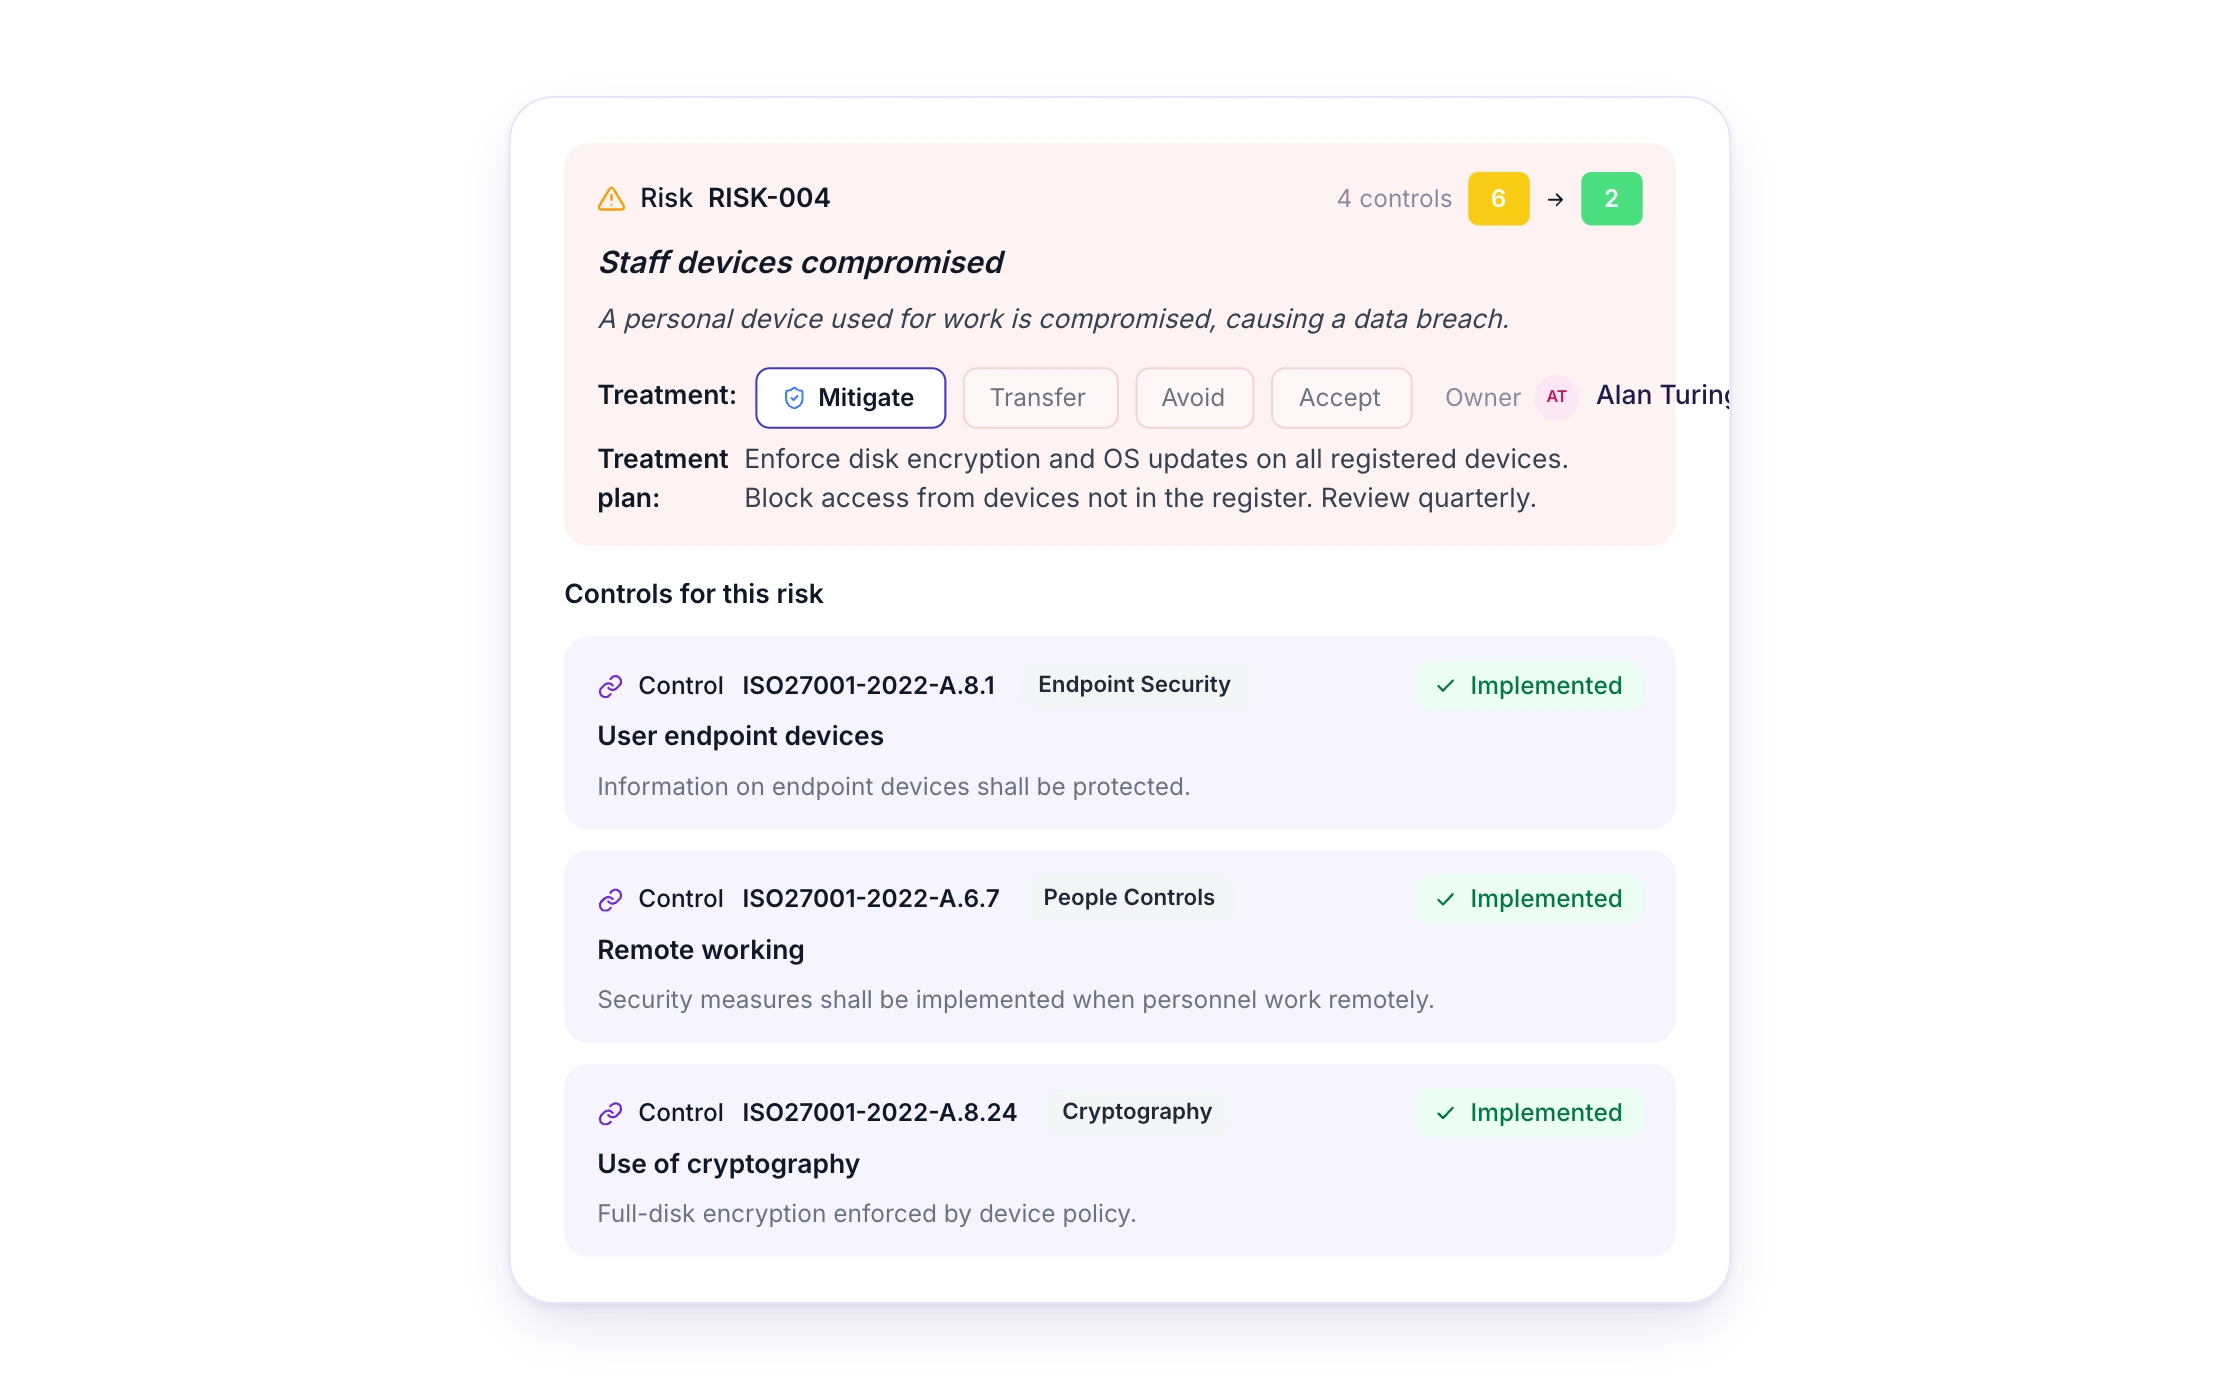
Focus on what’s in scope
Scope HIPAA to the systems, users and data that handle PHI for the covered entities you work with, so effort goes where it counts.
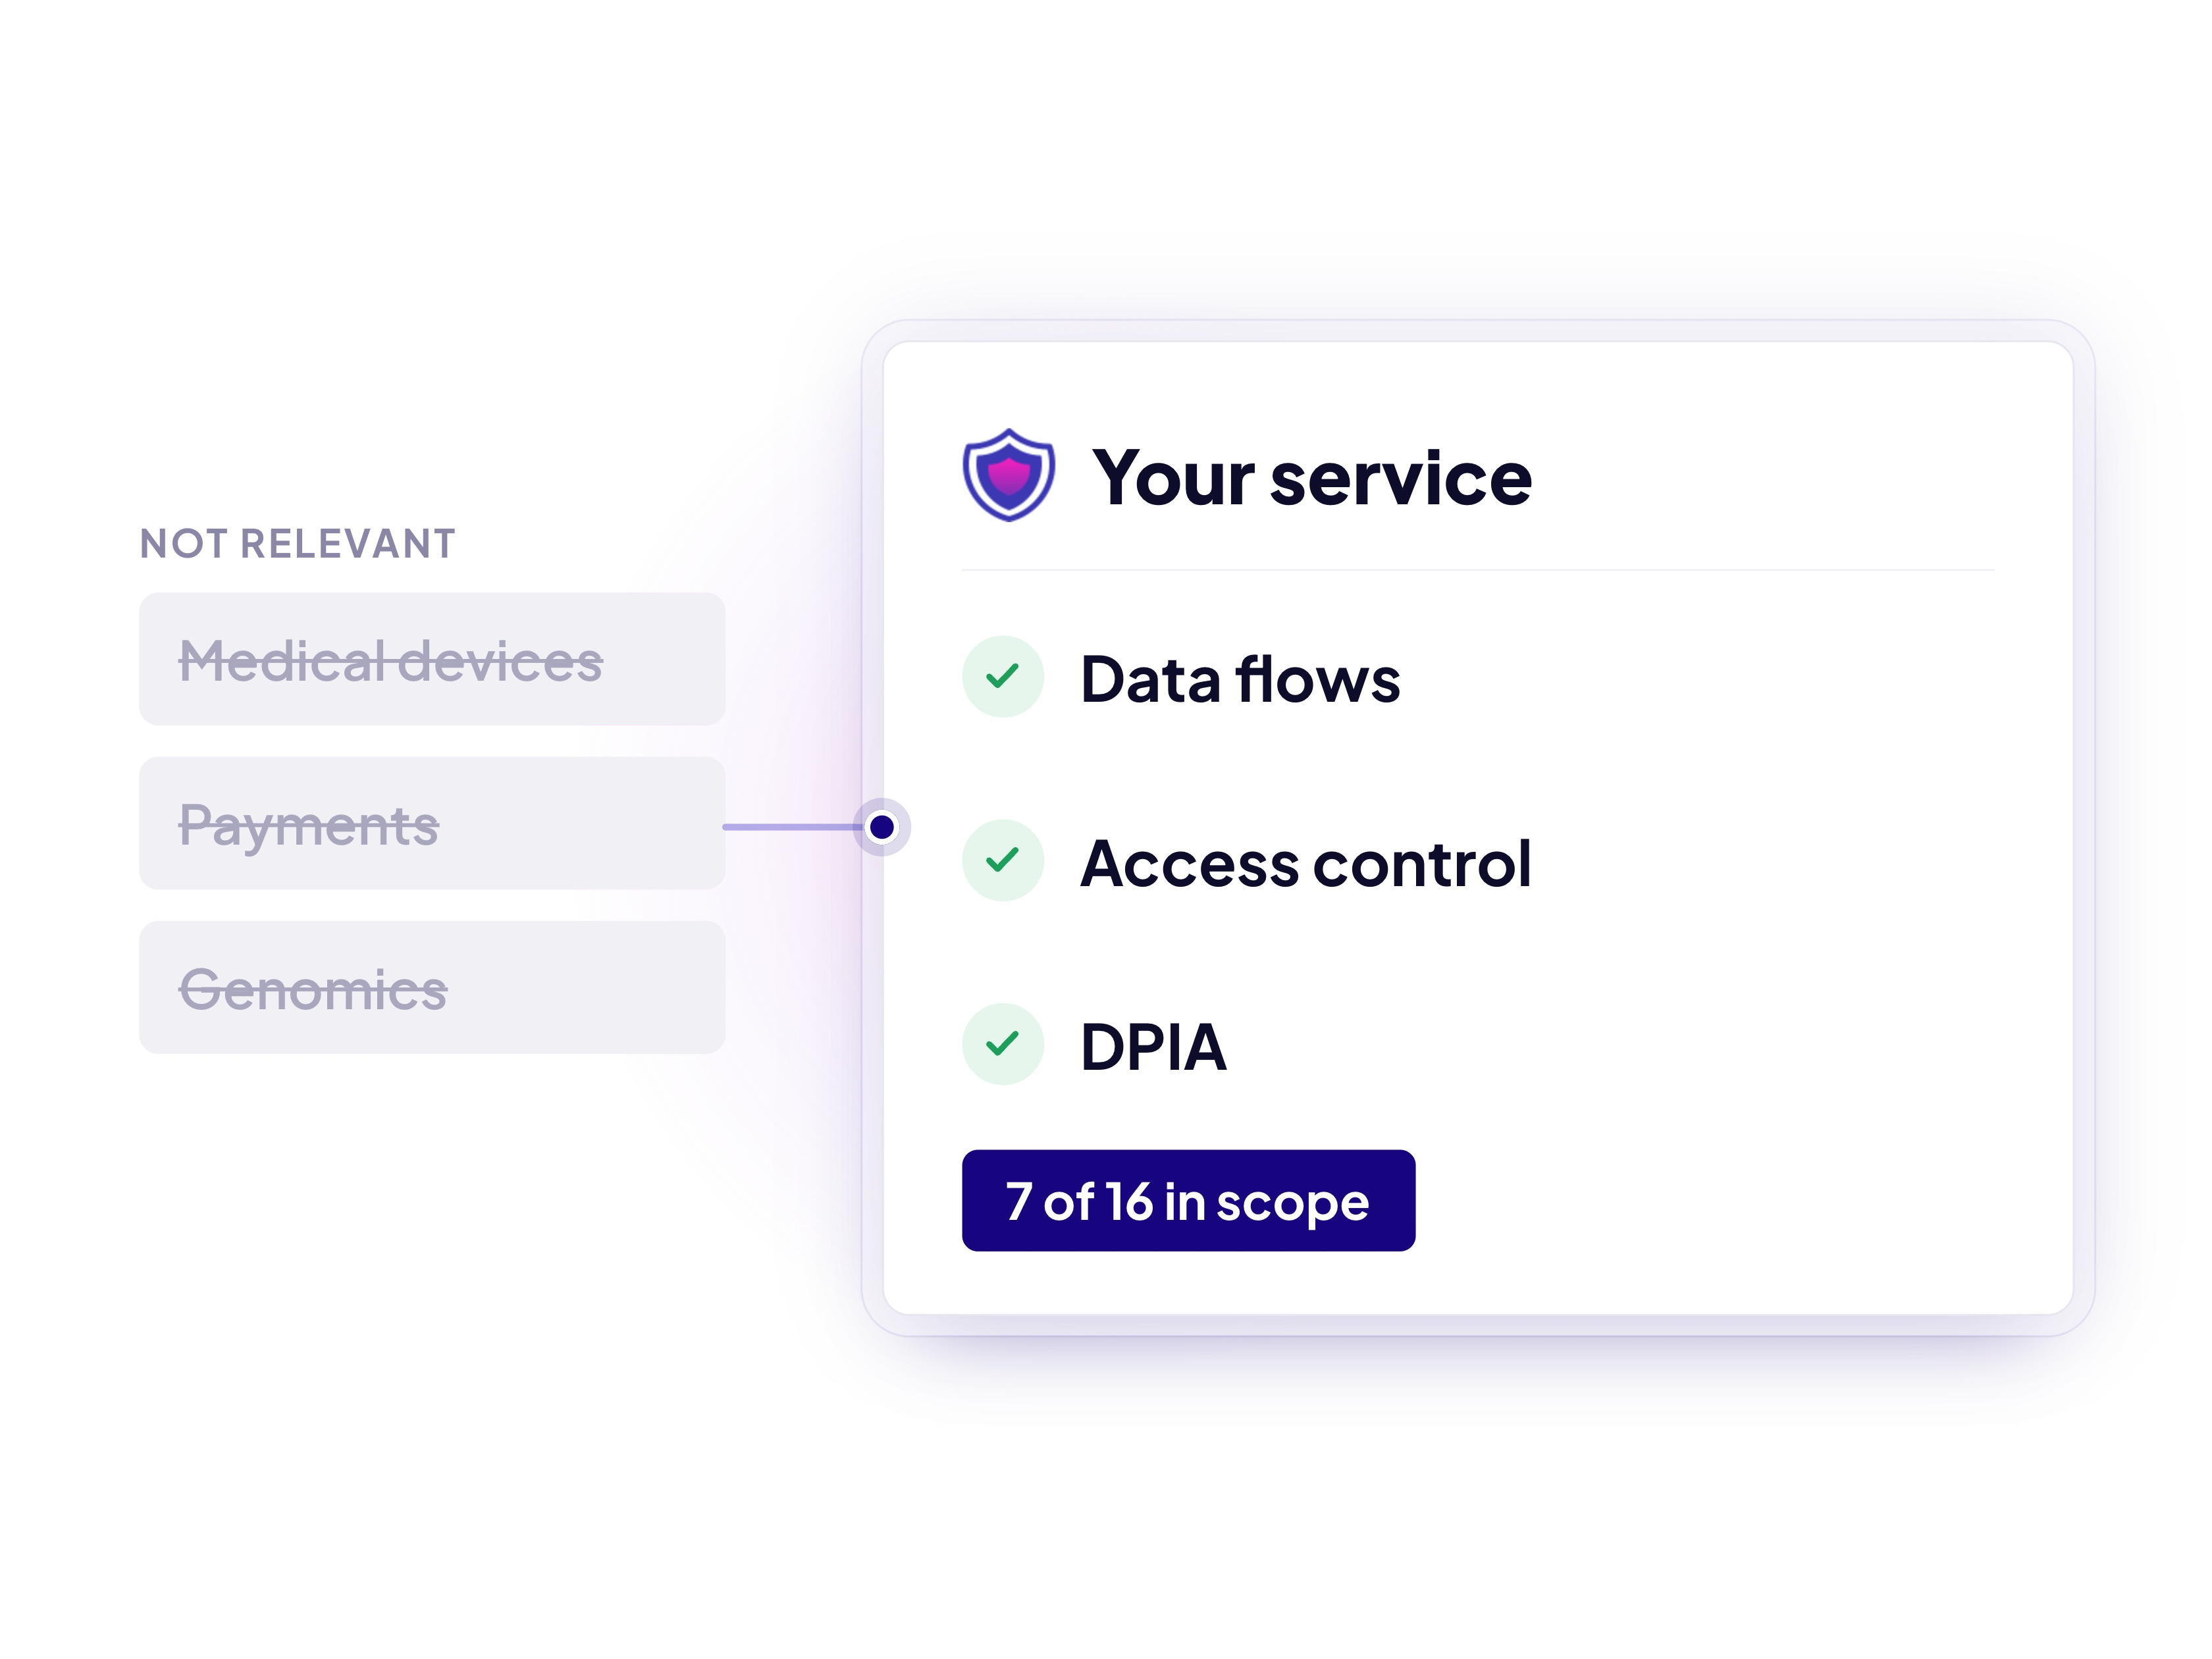
Assuric gives you the policies, controls and risk register to meet HIPAA, alongside every other framework you work to, all in one place.
Trusted by data protection teams


Features
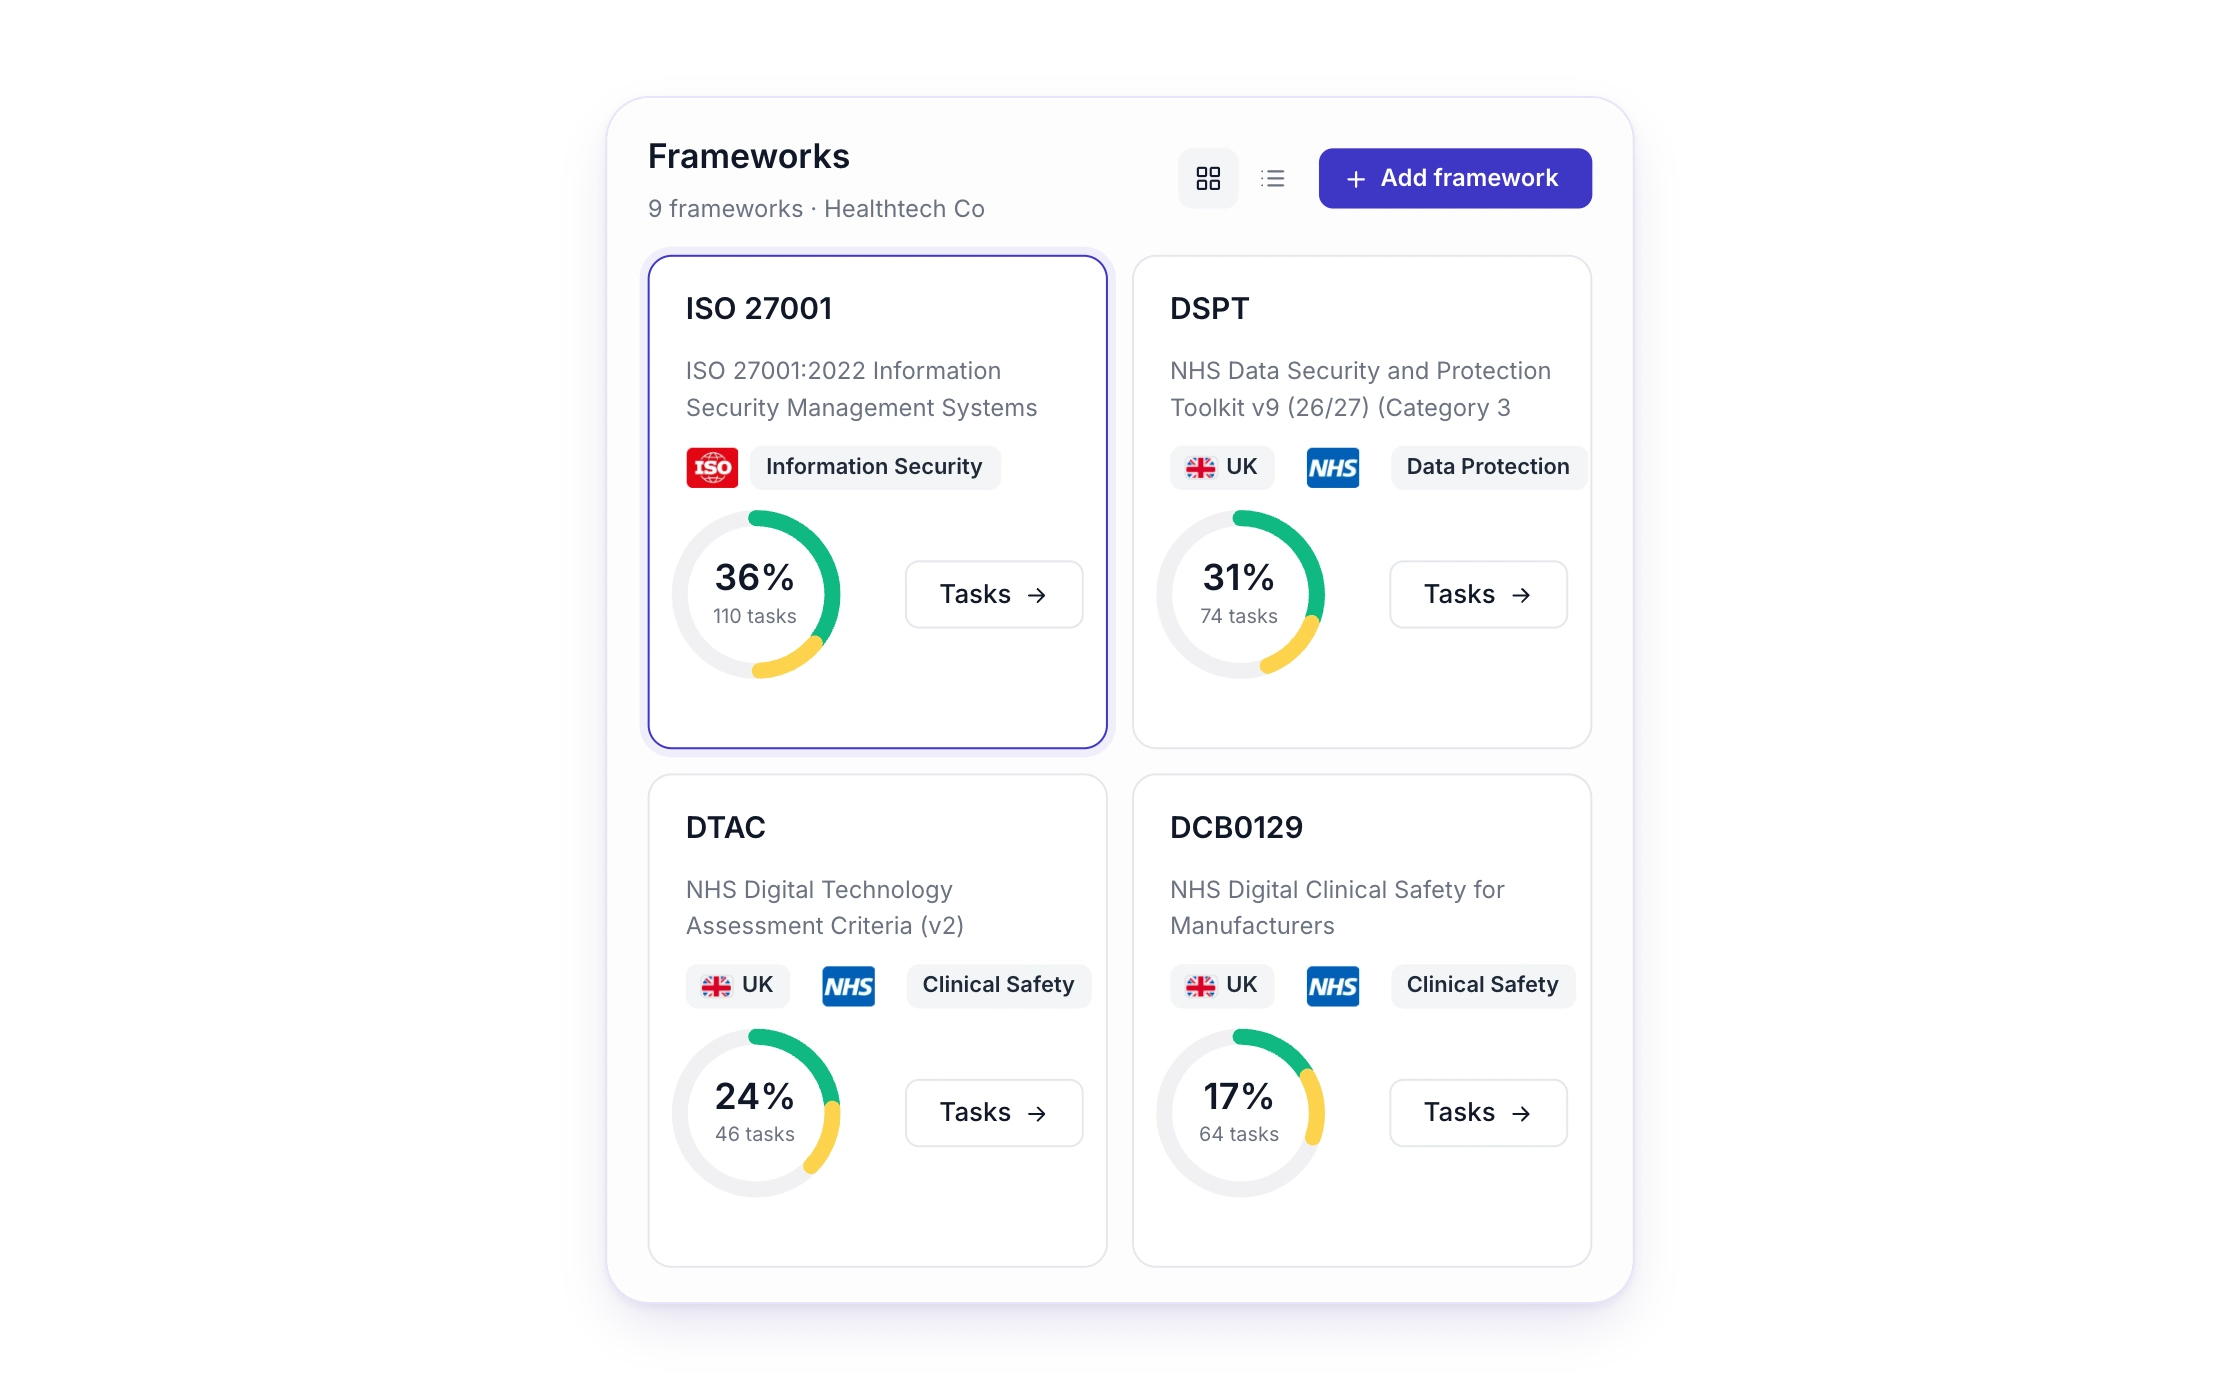
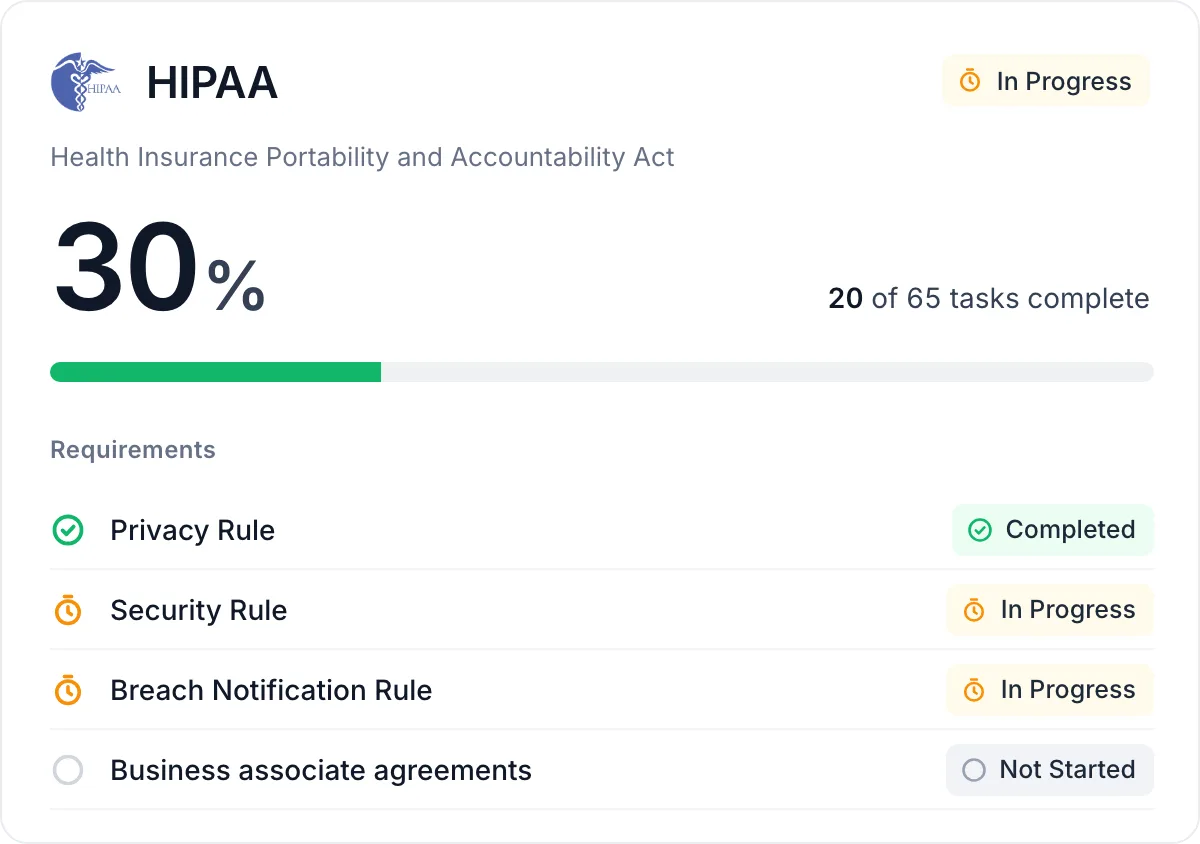
Automated compliance tracking
Fill any gaps, automate tasks, track compliance and get proactive alerts, so every requirement is met and stays met.
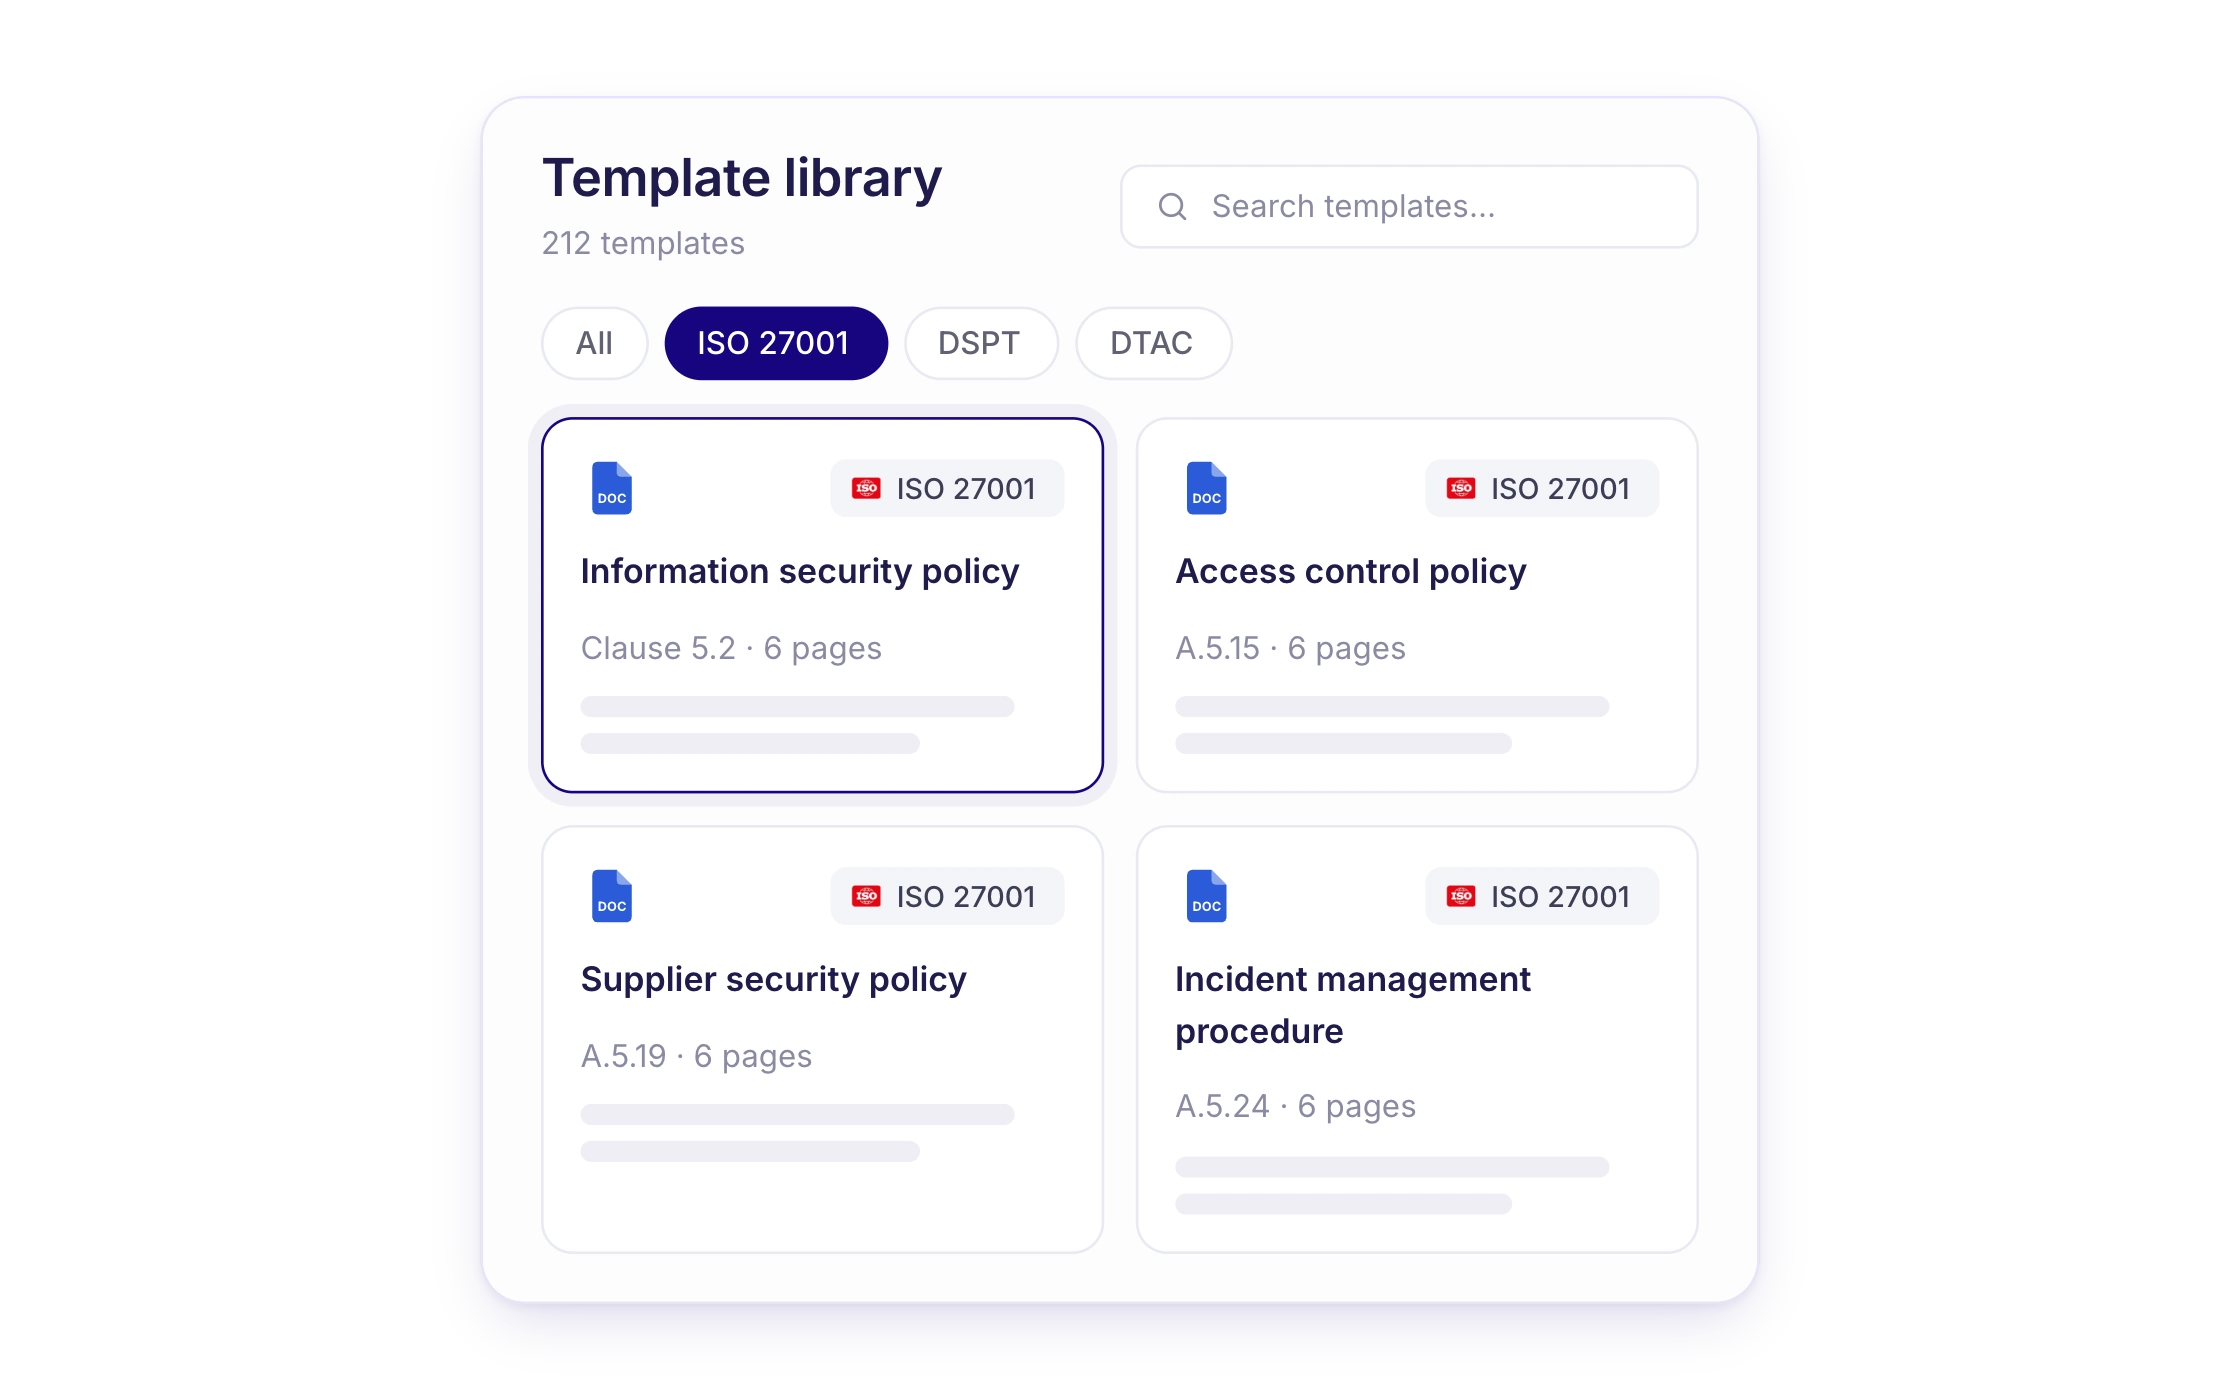
Document & policy management
Access our library of customisable templates, documents and procedures, including HIPAA Compliance Policies, HIPAA Breach Notification Procedures and more.
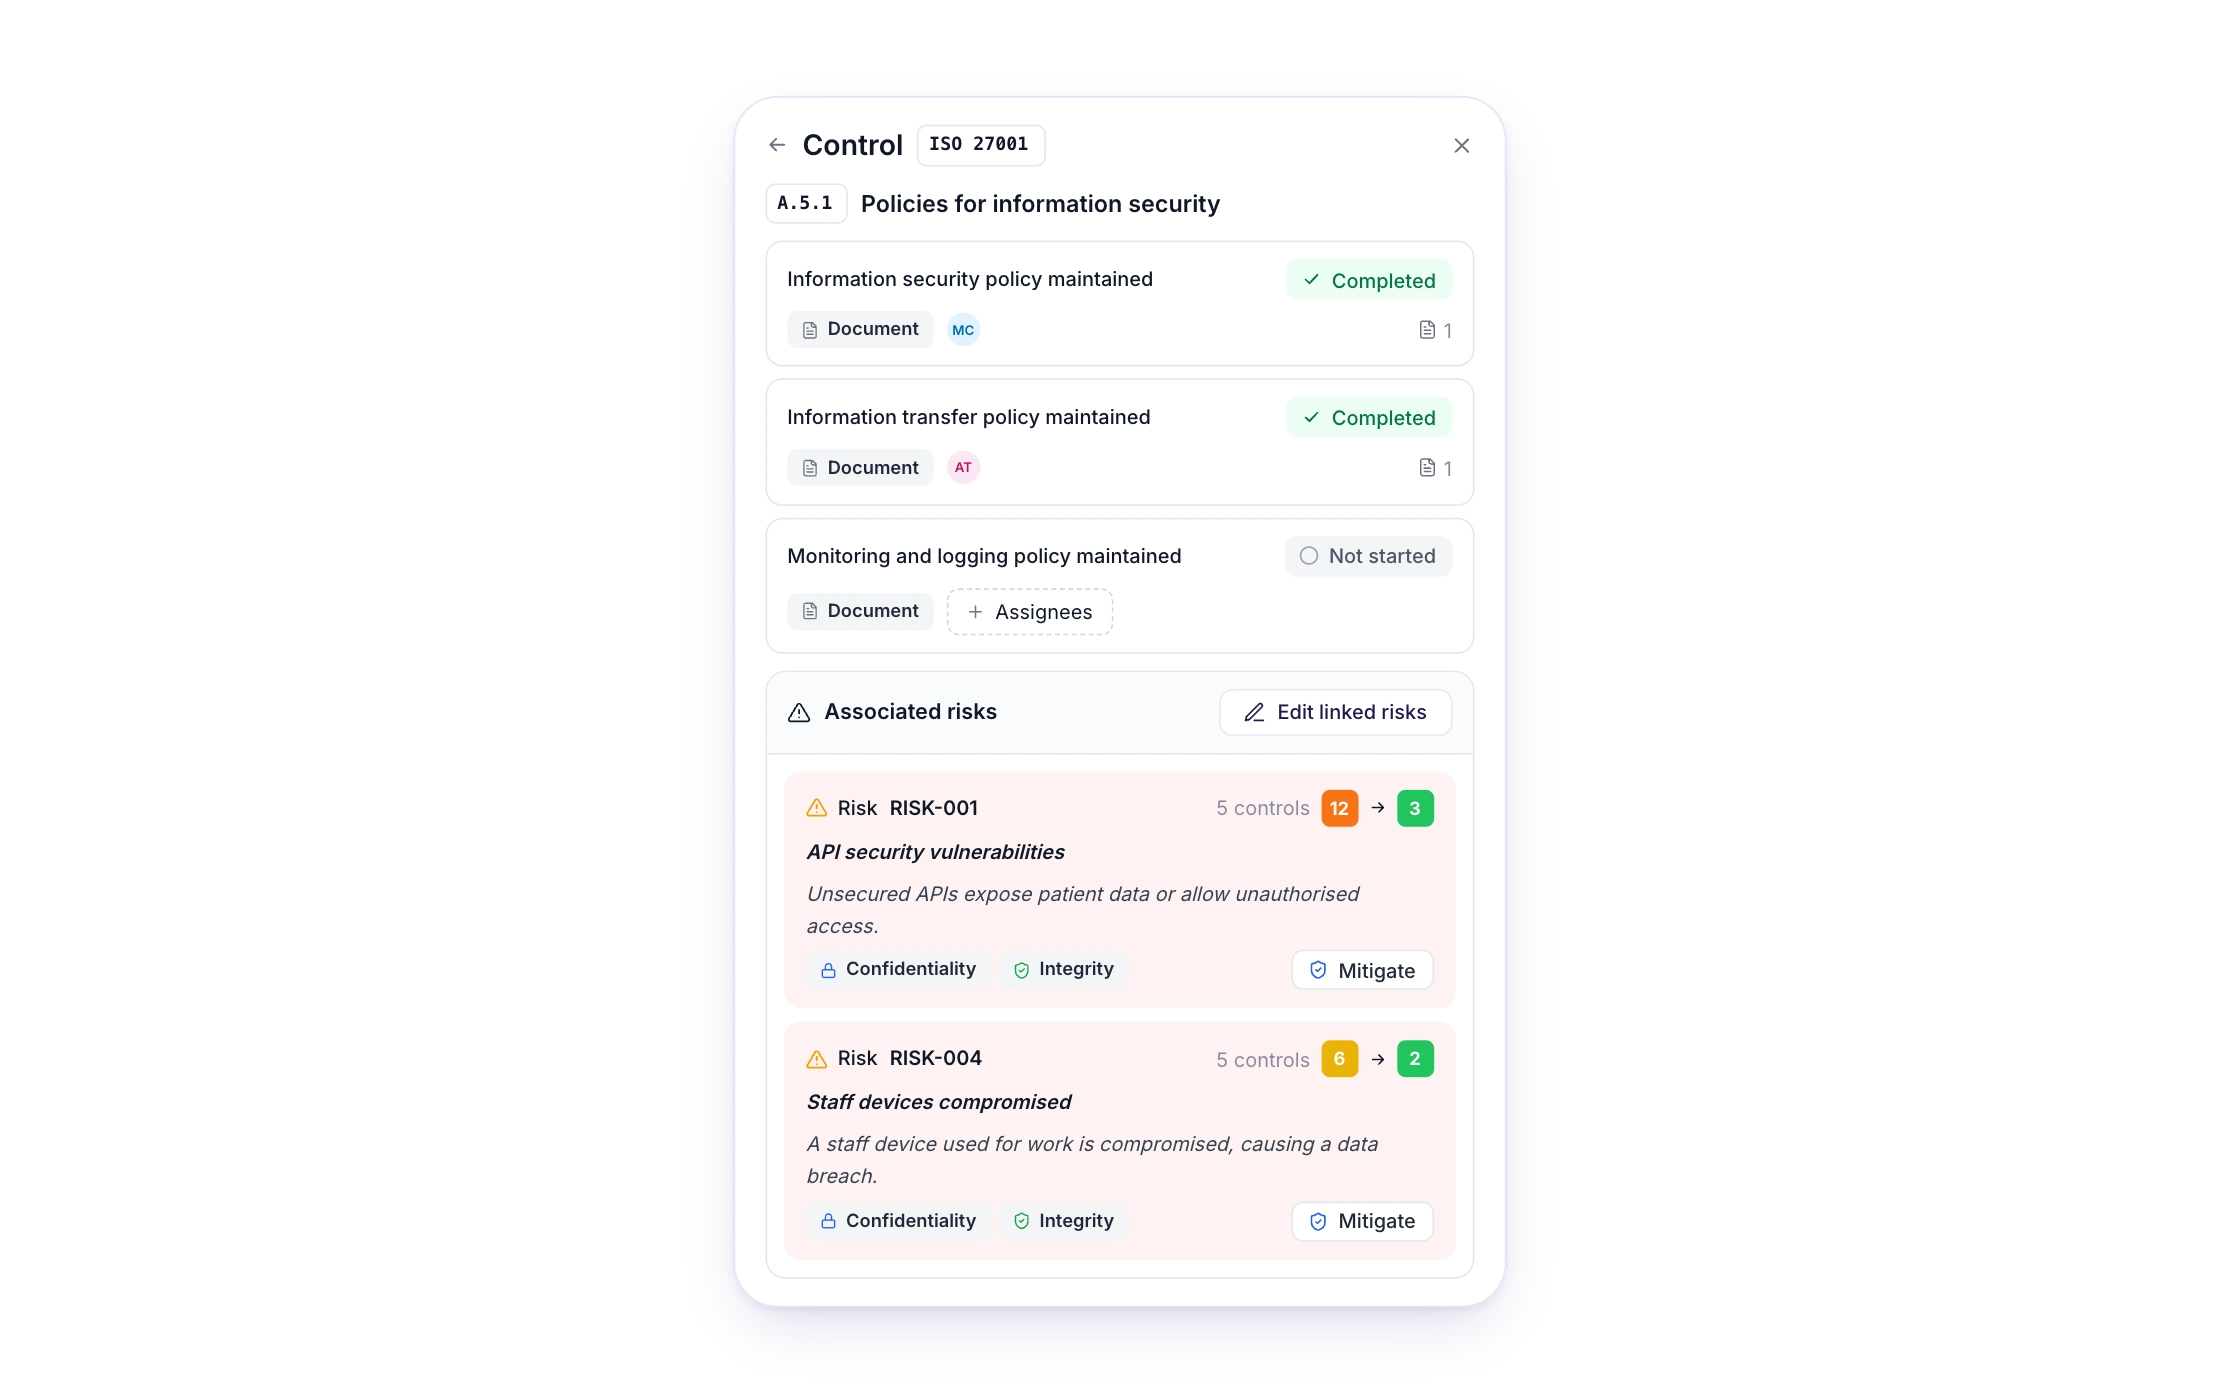
Automated compliance tracking
Implement the necessary HIPAA security controls including encryption, backups, access controls, screen locking and more.
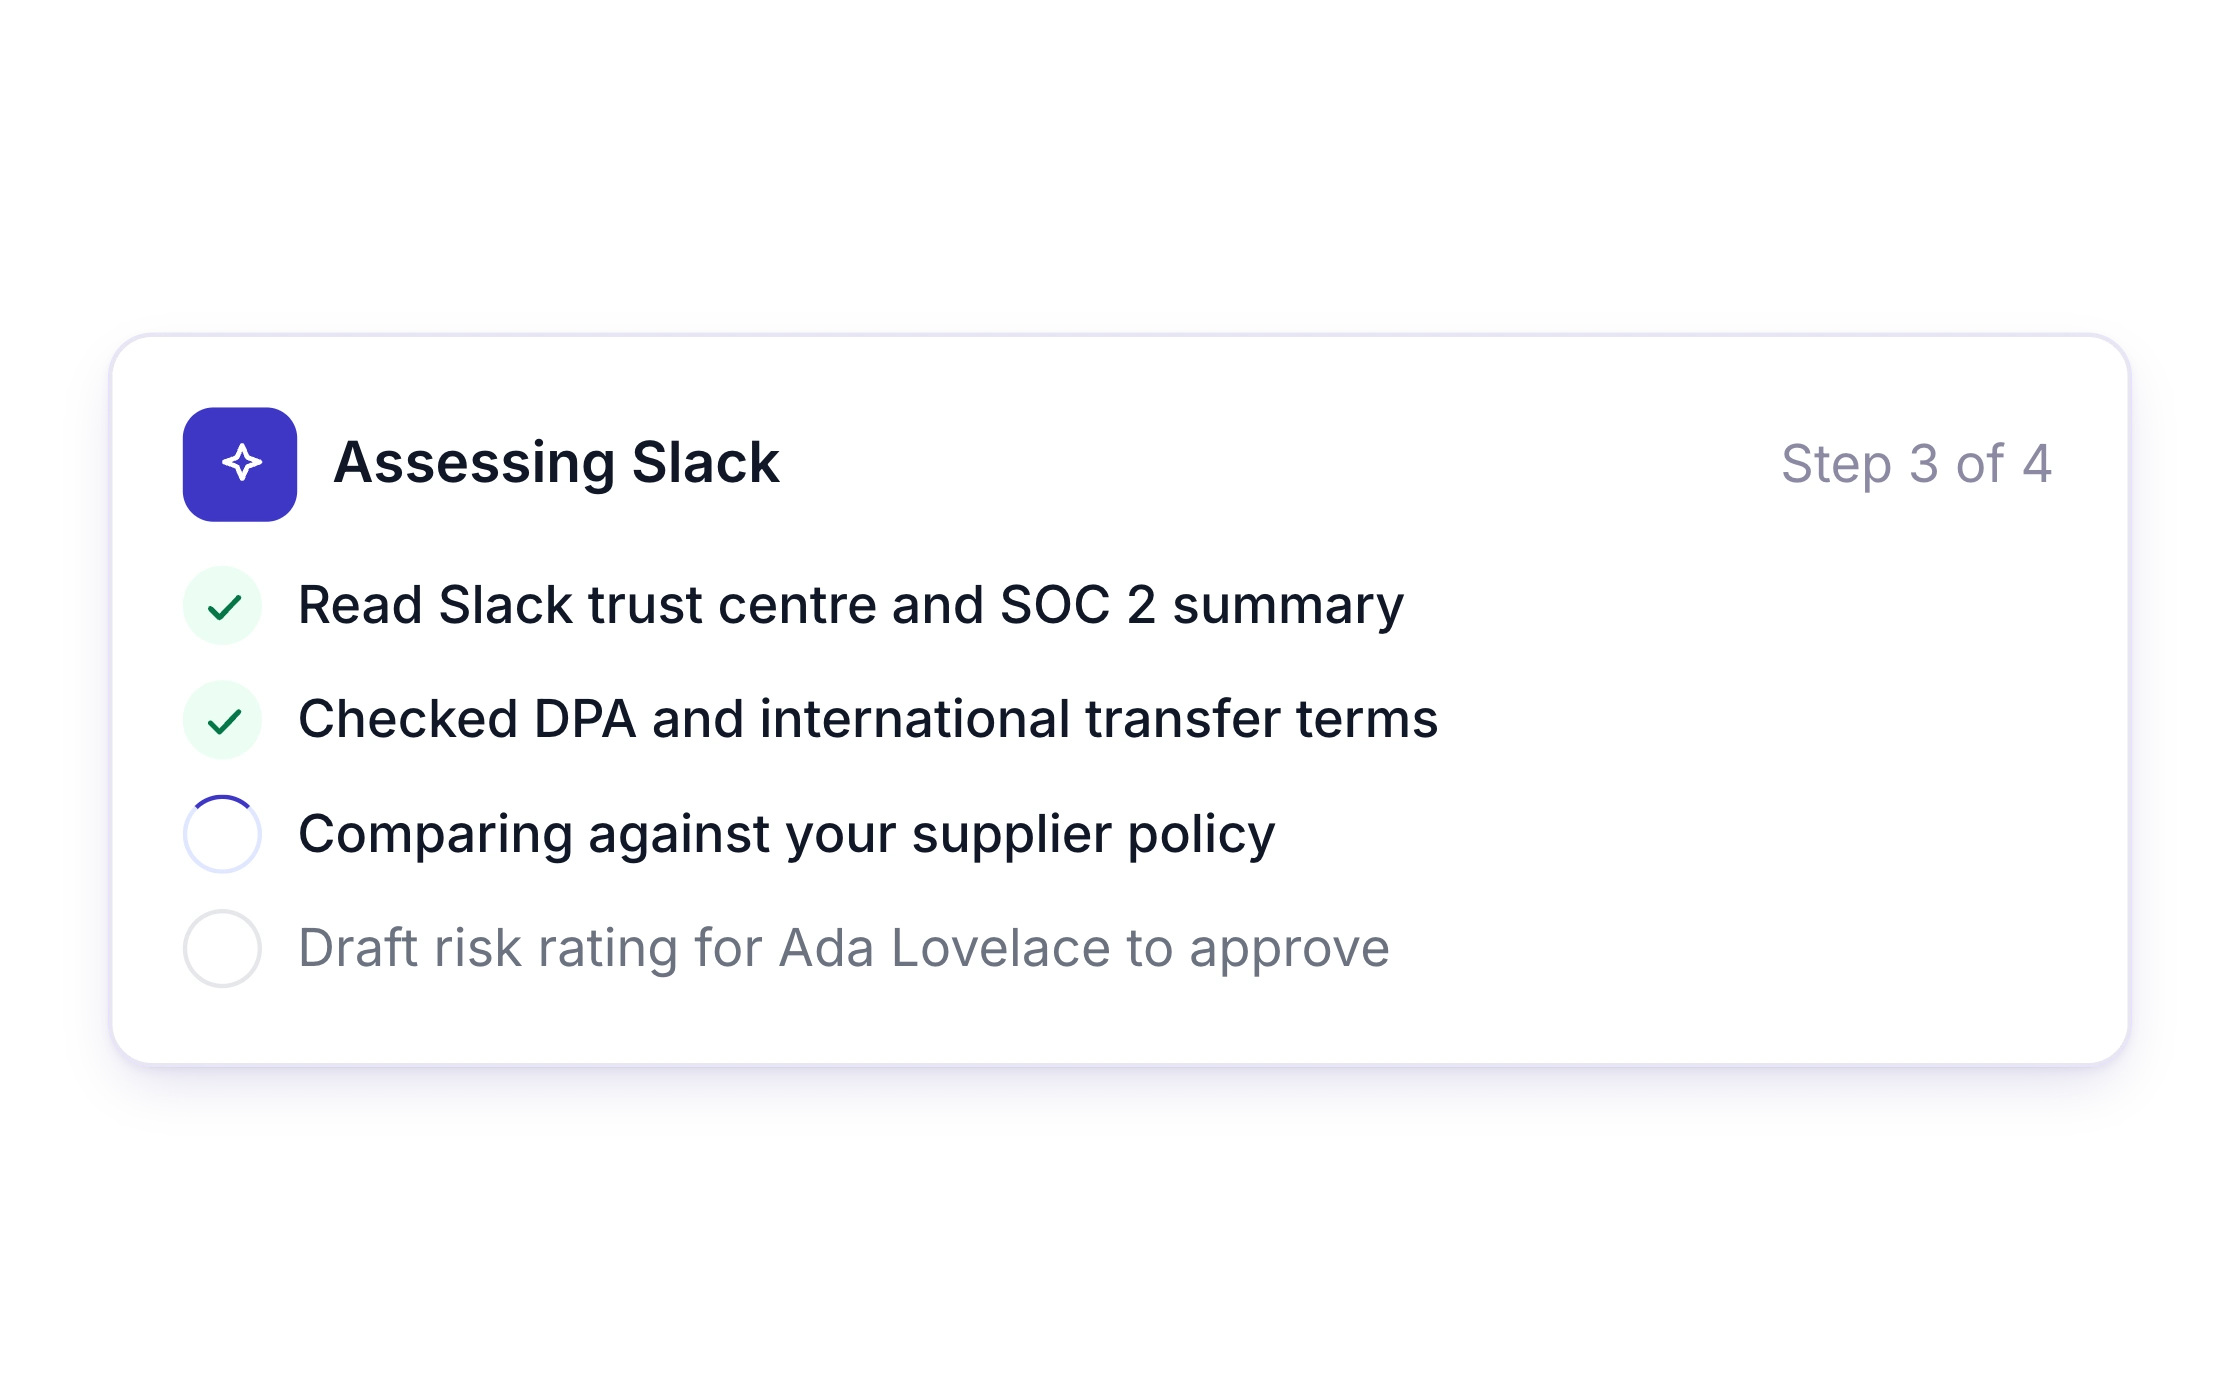
Third-party supplier management
Automate supplier security assessments and due diligence processes, including implementation and tracking of Business Associate Agreements (BAAs).
Benefits
Scope HIPAA to the systems, users and data that handle PHI for the covered entities you work with, so effort goes where it counts.
Policy templates, automation and linked records take care of the repetitive work, so keeping your HIPAA programme current takes minutes, not a quarterly clean-up.
Notifications, deadlines and task tracking keep risk analyses, reviews and training on schedule between assessments.
Show covered entities and partners a mature approach to protecting PHI, with policies, controls, BAAs and evidence ready whenever they ask.
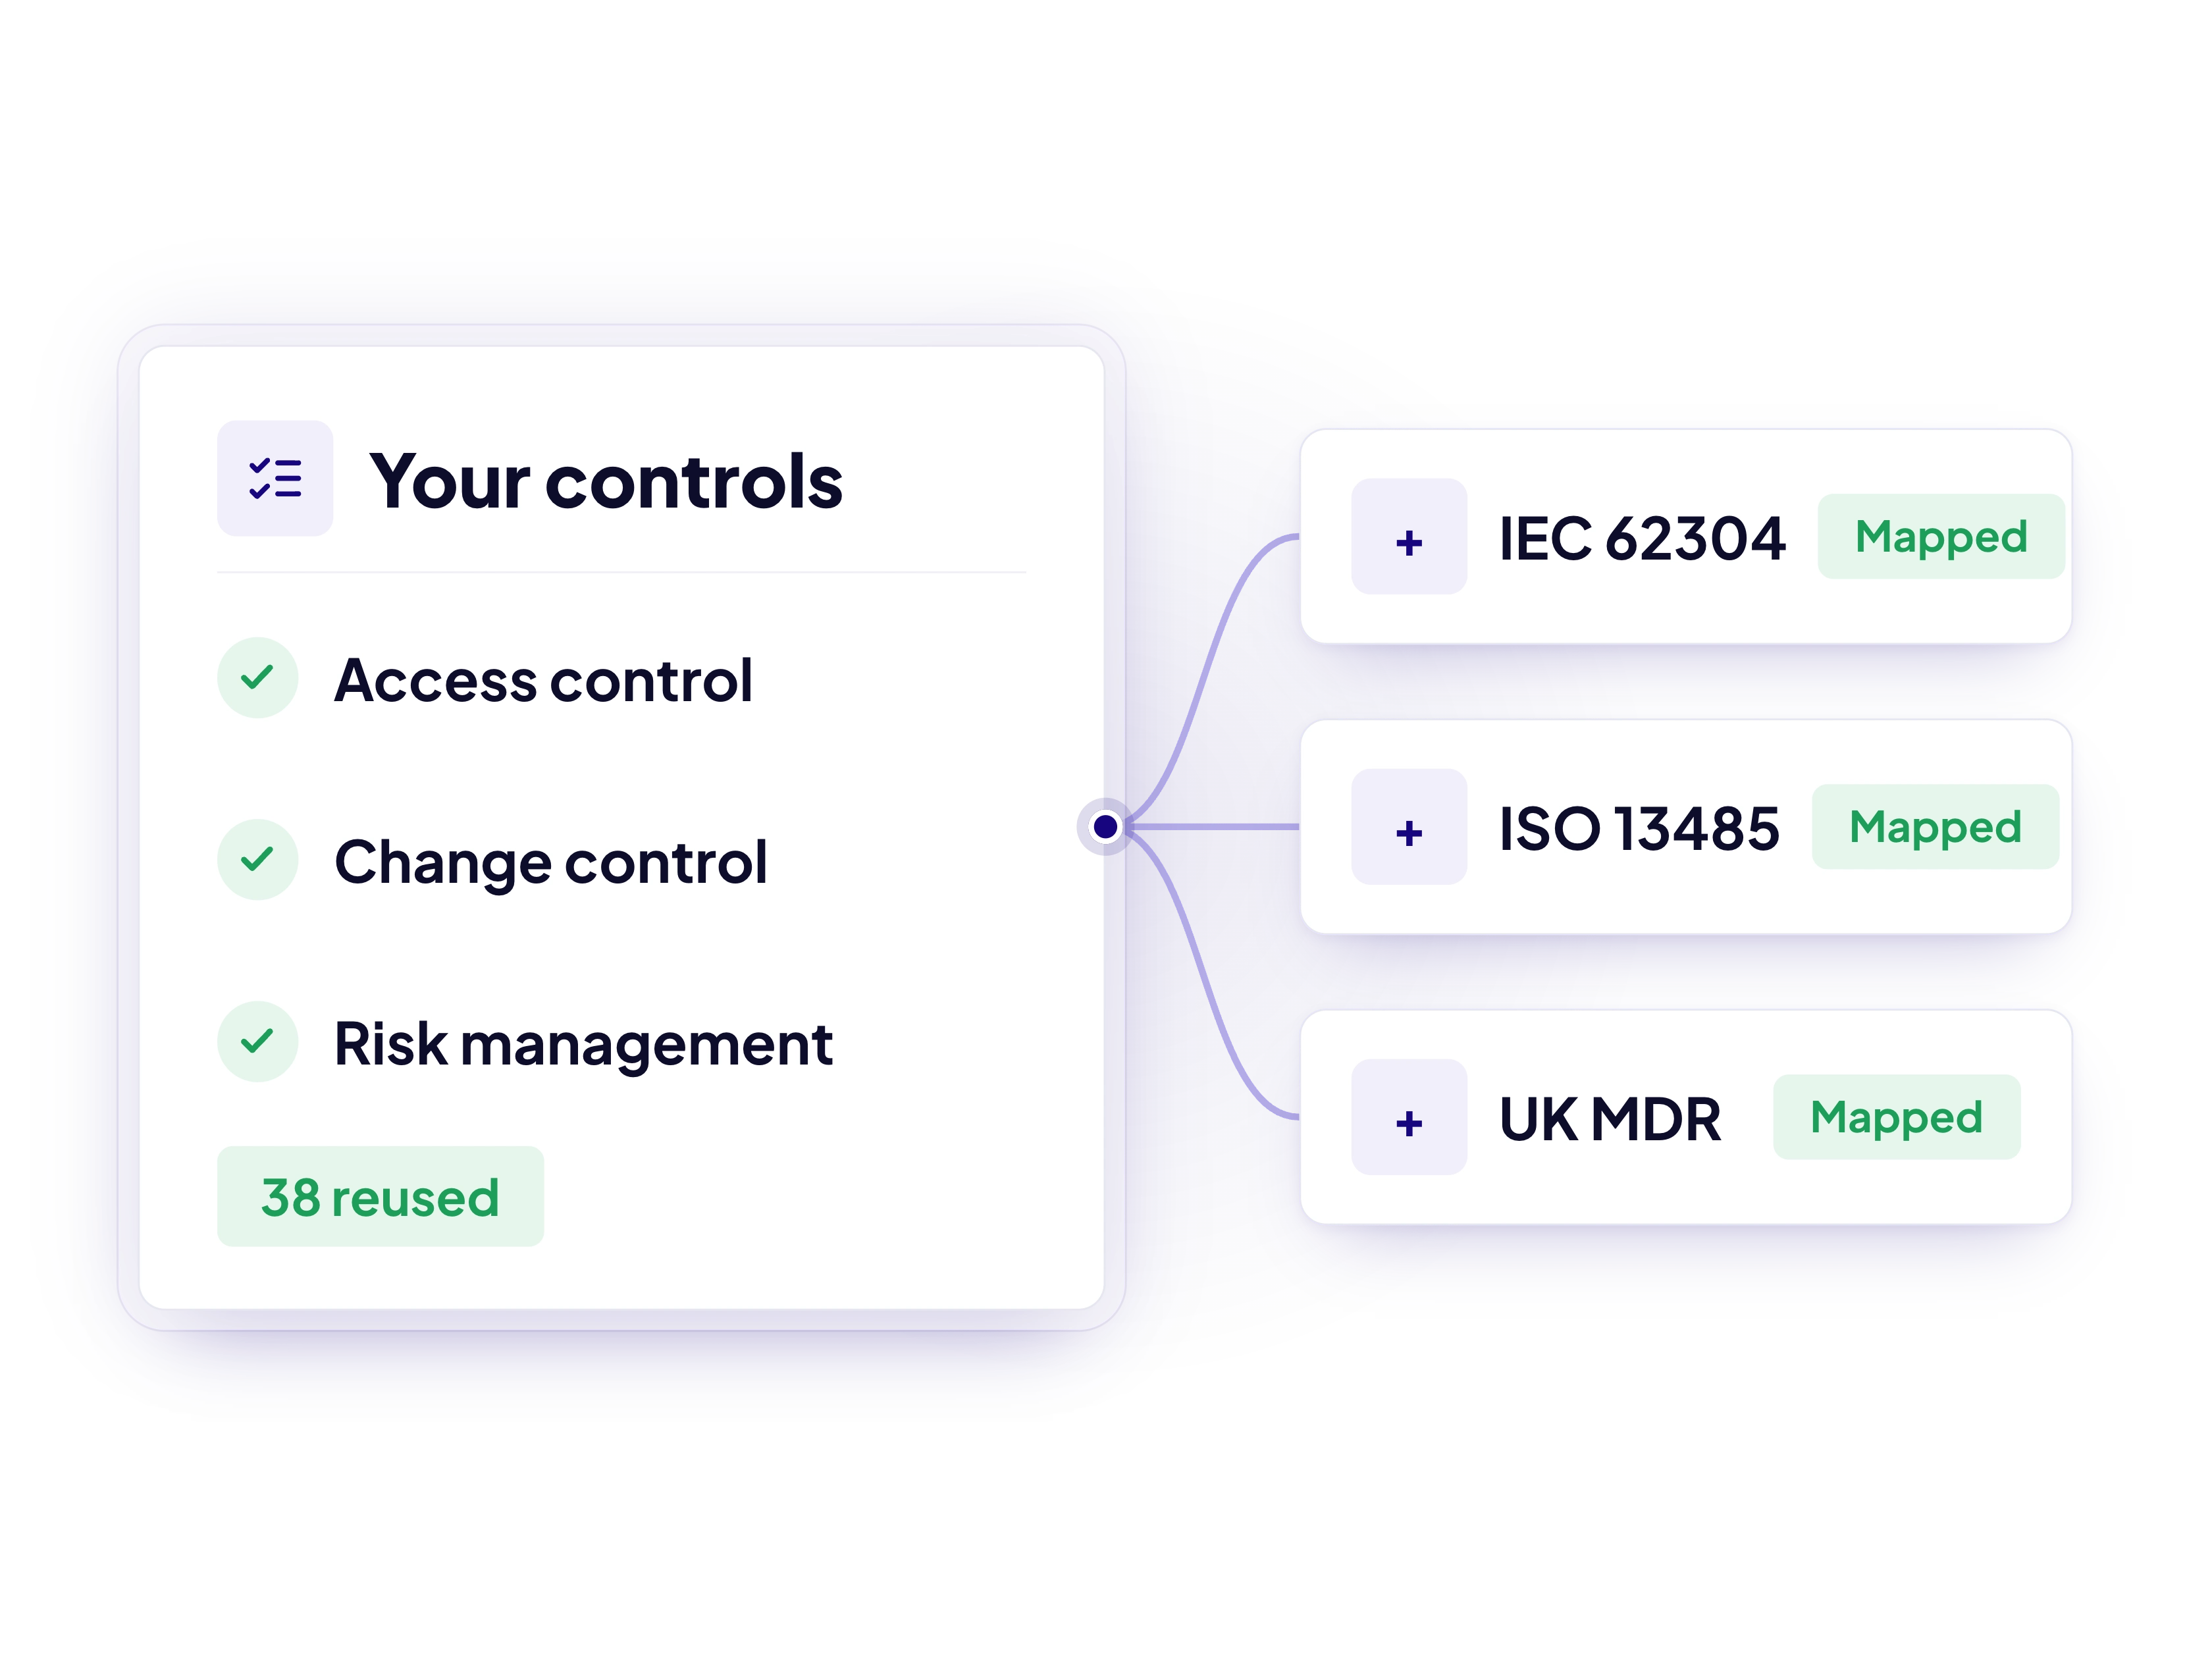
Cover HIPAA alongside SOC 2, ISO 27001 and the other frameworks you work to, reusing evidence instead of starting again.

“We couldn't speak highly enough of both the Assuric team and the platform itself, which is incredibly easy to use, and with the skill and hardworking nature of the Assuric team. They've been a key component in accelerating our progress and deployments!”
Maks Kozarzewski
COO, VitVio

“The Assuric platform is a game changer in the clinical risk management field. It has been carefully designed to make the job of a CSO significantly more streamlined. The team are excellent and responsive to any product suggestions I have requested, and it has been a pleasure to work with them.”
Paul Llewellyn
CCIO, Accenture

“Assuric has been fantastic in helping us quickly and safely navigate regulatory compliance in the UK. From completing Cybersecurity requirements to DSPT, DCB0129, and DTAC, the team was supportive, extremely knowledgeable, and the platform made everything quick and straightforward. A separate regulatory company we consulted at the beginning even remarked on how quickly we achieved compliance!”
Katie Baker
Director UK & Ireland, Tandem
The Health Insurance Portability and Accountability Act of 1996 (HIPAA) is a US federal law that sets national standards for protecting the privacy and security of individuals’ health information and for standardising electronic healthcare transactions. The Department of Health and Human Services (HHS) has issued Privacy, Security and Breach Notification Rules under it, which govern how "protected health information" (PHI) is used, disclosed, stored and transmitted by covered entities, such as health plans and most healthcare providers, and by the business associates that work for them.
HIPAA directly governs Covered Entities: health plans, healthcare clearinghouses, and healthcare providers that transmit health data electronically. Business Associates are vendors (suppliers) or subcontractors that create, receive, maintain, or transmit PHI on behalf of a covered entity. Cloud providers, billing services, telehealth platforms and other digital health suppliers are common examples of Business Associates.
Protected Health Information (PHI) is any individually identifiable health data (past, present, or future) created, received, or maintained by a covered entity or business associate. This can be broad including items like medical records and lab results, but also appointment reminders, insurance IDs, biometric identifiers, and even device IDs when they can reasonably link back to a person's health status.
A BAA is a legally binding contract between a covered entity and a business associate, or between a business associate and its subcontractor. It sets out how the vendor may use and disclose PHI, the safeguards it must apply, its duty to report breaches, and its duty to pass the same terms on to its own subcontractors. It must be in place before any PHI flows to the vendor. Without one, both organisations are non-compliant, even if no breach occurs.
Privacy Rule: governs how, when and why protected health information (PHI) may be used or disclosed, enforces the minimum necessary standard, and gives patients rights to access or amend their data.
Security Rule: requires a risk-based set of administrative, physical and technical safeguards, such as policies, facility controls, encryption, access management and audit logging, to protect electronic PHI (ePHI).
Breach Notification Rule: business associates must notify the covered entity of a breach of unsecured PHI without unreasonable delay, and no later than 60 days after discovering it. The covered entity must then notify the affected individuals and HHS.
The Security Rule requires every covered entity or business associate to build a risk-based programme that keeps electronic PHI confidential, intact, and available when needed. It groups safeguards into three mutually reinforcing layers:
All controls must be documented, periodically tested, and adjusted as technology, threats or the business change. HIPAA cares less about the specific tools you buy than about proving that the safeguards you chose are effective and continually improved.
No. A compliant-ready infrastructure only solves a fraction of the obligations. You still need a signed BAA with the cloud provider and must configure services securely, control application-layer access, document policies, train staff, maintain audit trails, manage incident response, and monitor for new risks. HIPAA liability ultimately stays with the covered entity or business associate, not the cloud vendor.
The HHS Office for Civil Rights (OCR) enforces the HIPAA Privacy, Security and Breach Notification Rules. State attorneys general can also bring civil actions, and the Department of Justice prosecutes criminal cases. If your health app isn’t covered by HIPAA, the Federal Trade Commission’s Health Breach Notification Rule may still apply.
The HHS Office for Civil Rights (OCR) imposes civil money penalties on four tiers, from violations an organisation didn’t know about up to wilful neglect left uncorrected, with per-violation amounts and annual caps adjusted for inflation each year. Separately, knowingly obtaining or disclosing health information in breach of HIPAA is a federal crime prosecuted by the Department of Justice, with fines of up to $250,000 and up to 10 years in prison. State attorneys general can also bring civil actions. OCR settlements often include multi-year corrective action plans, on top of breach-response costs, lawsuits and reputational damage.
HHS does not issue or recognise any formal certification. Independent auditors and third party organisations can perform external HIPAA audits and assessments, which can be advantageous but not an absolute requirement. Ultimately, compliance is demonstrated through continuous adherence to the rules and the ability to show evidence during an OCR investigation.
Assuric centralises your HIPAA programme in one workspace, mapping each requirement to straightforward tasks and controls that are shared with your other frameworks. Guided workflows take you through risk analysis, policy management, staff training, supplier assessments and BAAs.
See how Assuric helps you show covered entities you protect PHI properly, from risk analysis to signed BAAs.

