Data protection and security,
in one place

Manage your RoPA, DPIAs, security risks and assets in one platform, answer customer security questions faster and get expert DPO support when you need it.

  • All data protection and security frameworks in one place
  • Assets, risks, devices, RoPA and DPIAs
  • Incident and breach management
  • Fractional DPO support available

By continuing you agree to our privacy notice

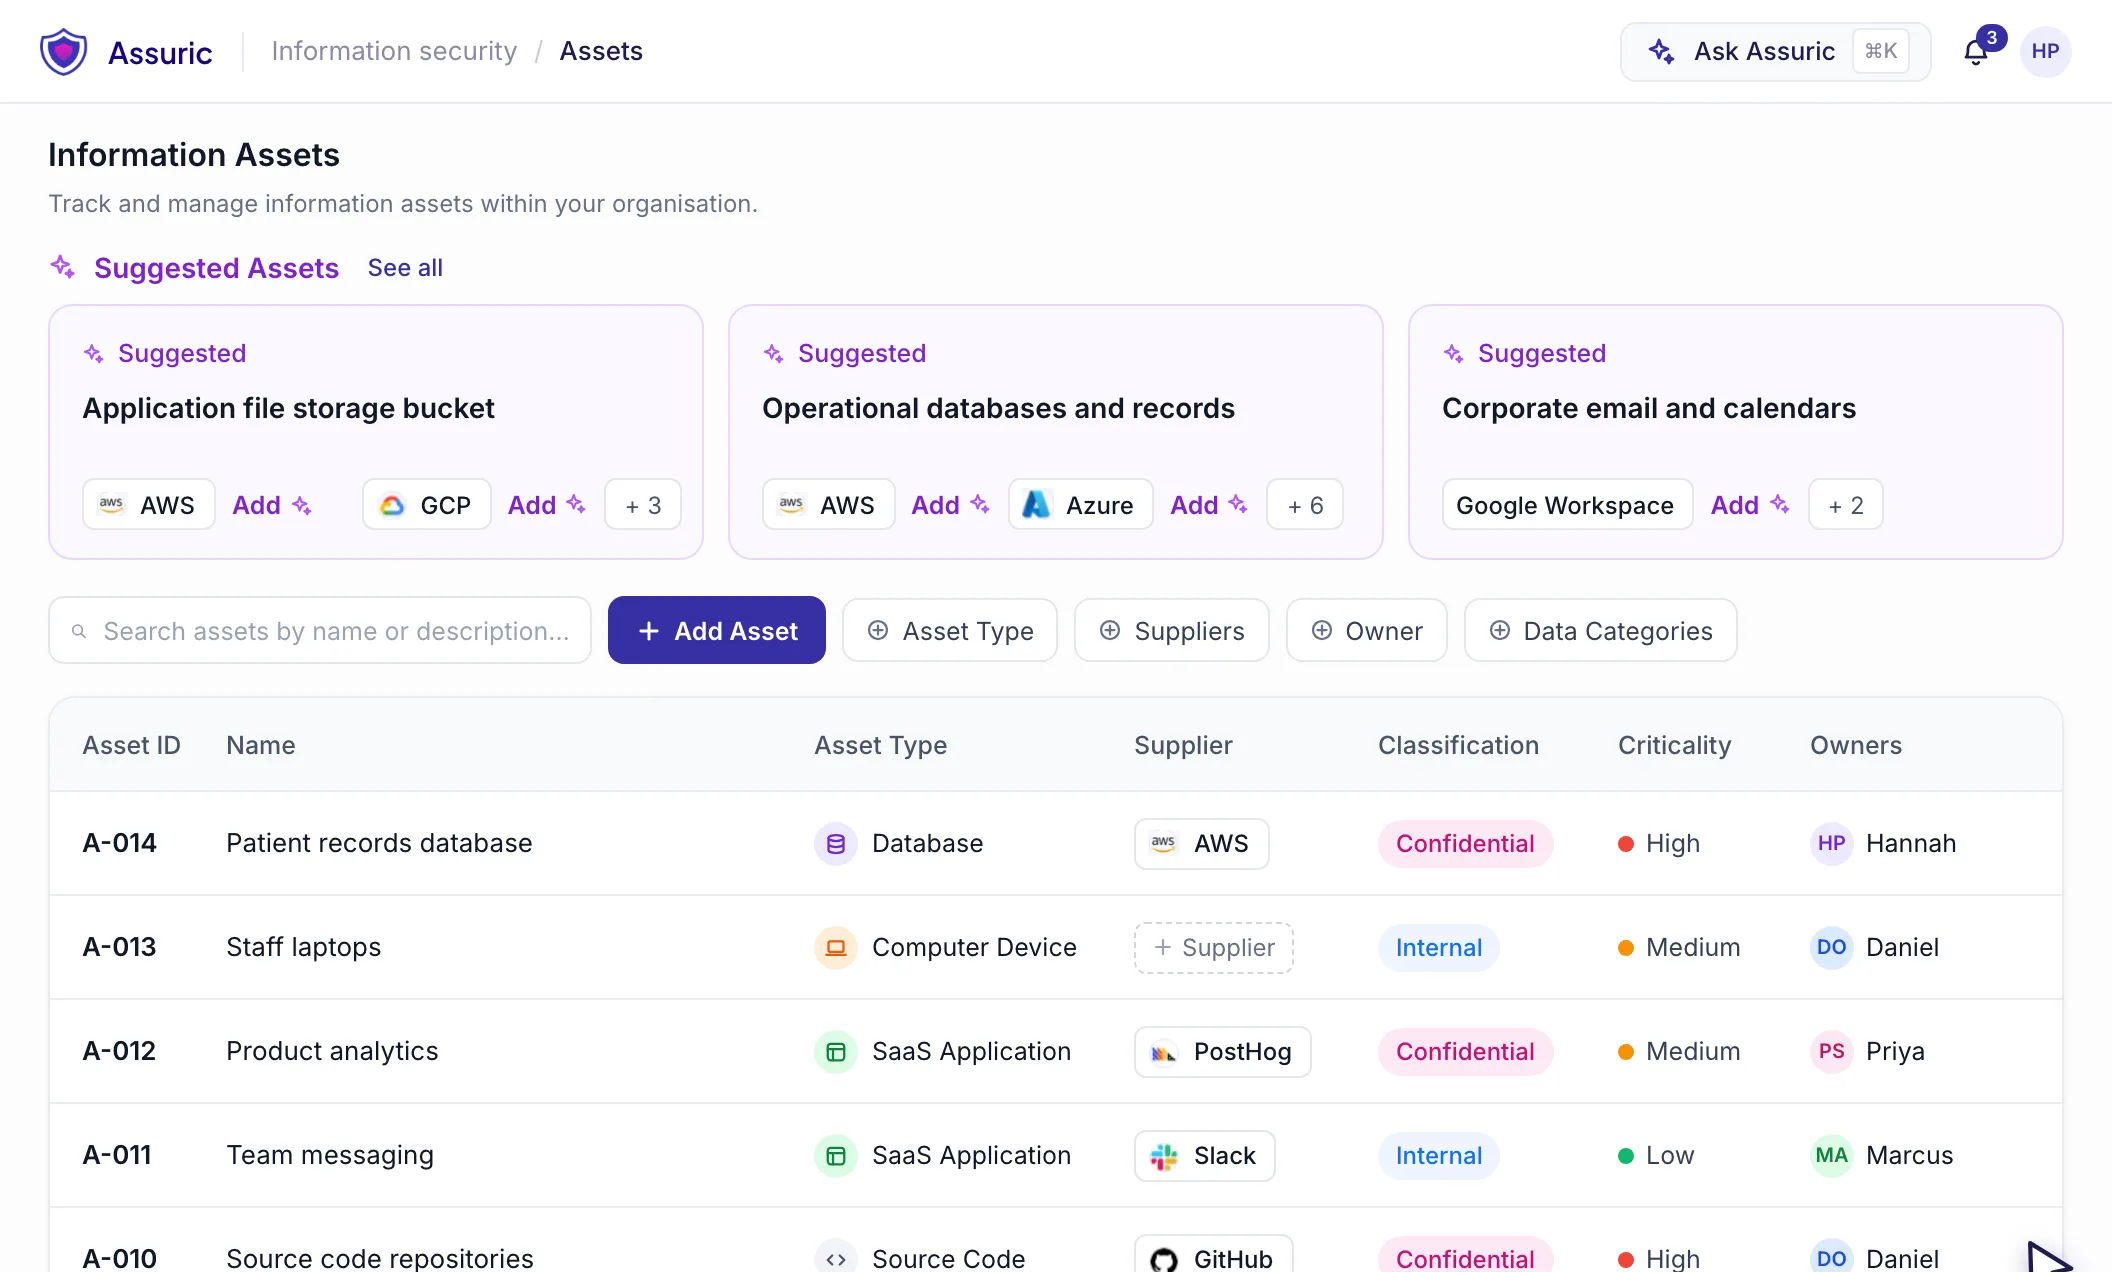
Information asset register with suggested assets, suppliers, classification, criticality and owners
AccurxTandemSembleLimbicBraiveDrDoctorCircle Health GroupNorthern Care Alliance NHS Foundation TrustCleo SystemsCorelineGuardantSanomePolyAIEolas MedicalChequpHeimDelfaHippo LabsInfixMegiNursebuddyOnion AIRhazesRosenfieldSurgery AIHealthnixThink DivergentHestaVitVioUniversity Hospitals of Derby and Burton NHS Foundation TrustAnimaAscentiAsterixEvergreen LifeHello PatientHealthtech-1Modality PartnershipNHS Wales Performance & ImprovementCwm Taf Morgannwg University Health BoardOperose HealthPatient Care Locally CIC (LLR)Theta SleepAccentureCareStackSouth Warwickshire University NHS Foundation TrustUniversity Hospitals of Leicester NHS TrustMersey and West Lancashire Teaching Hospitals NHS TrustWeymouth Bay Medical PracticeNottingham CityCare PartnershipMid Mersey Digital AlliancePenrose Health

Benefits

Take the hassle out of data protection and security

Know what personal data you collect, where it goes and how you use it

See what personal data you collect, why you use it, where it goes and which suppliers handle it. Keep your processing records and DPIAs together, so you can find the information you need without chasing people or searching spreadsheets.
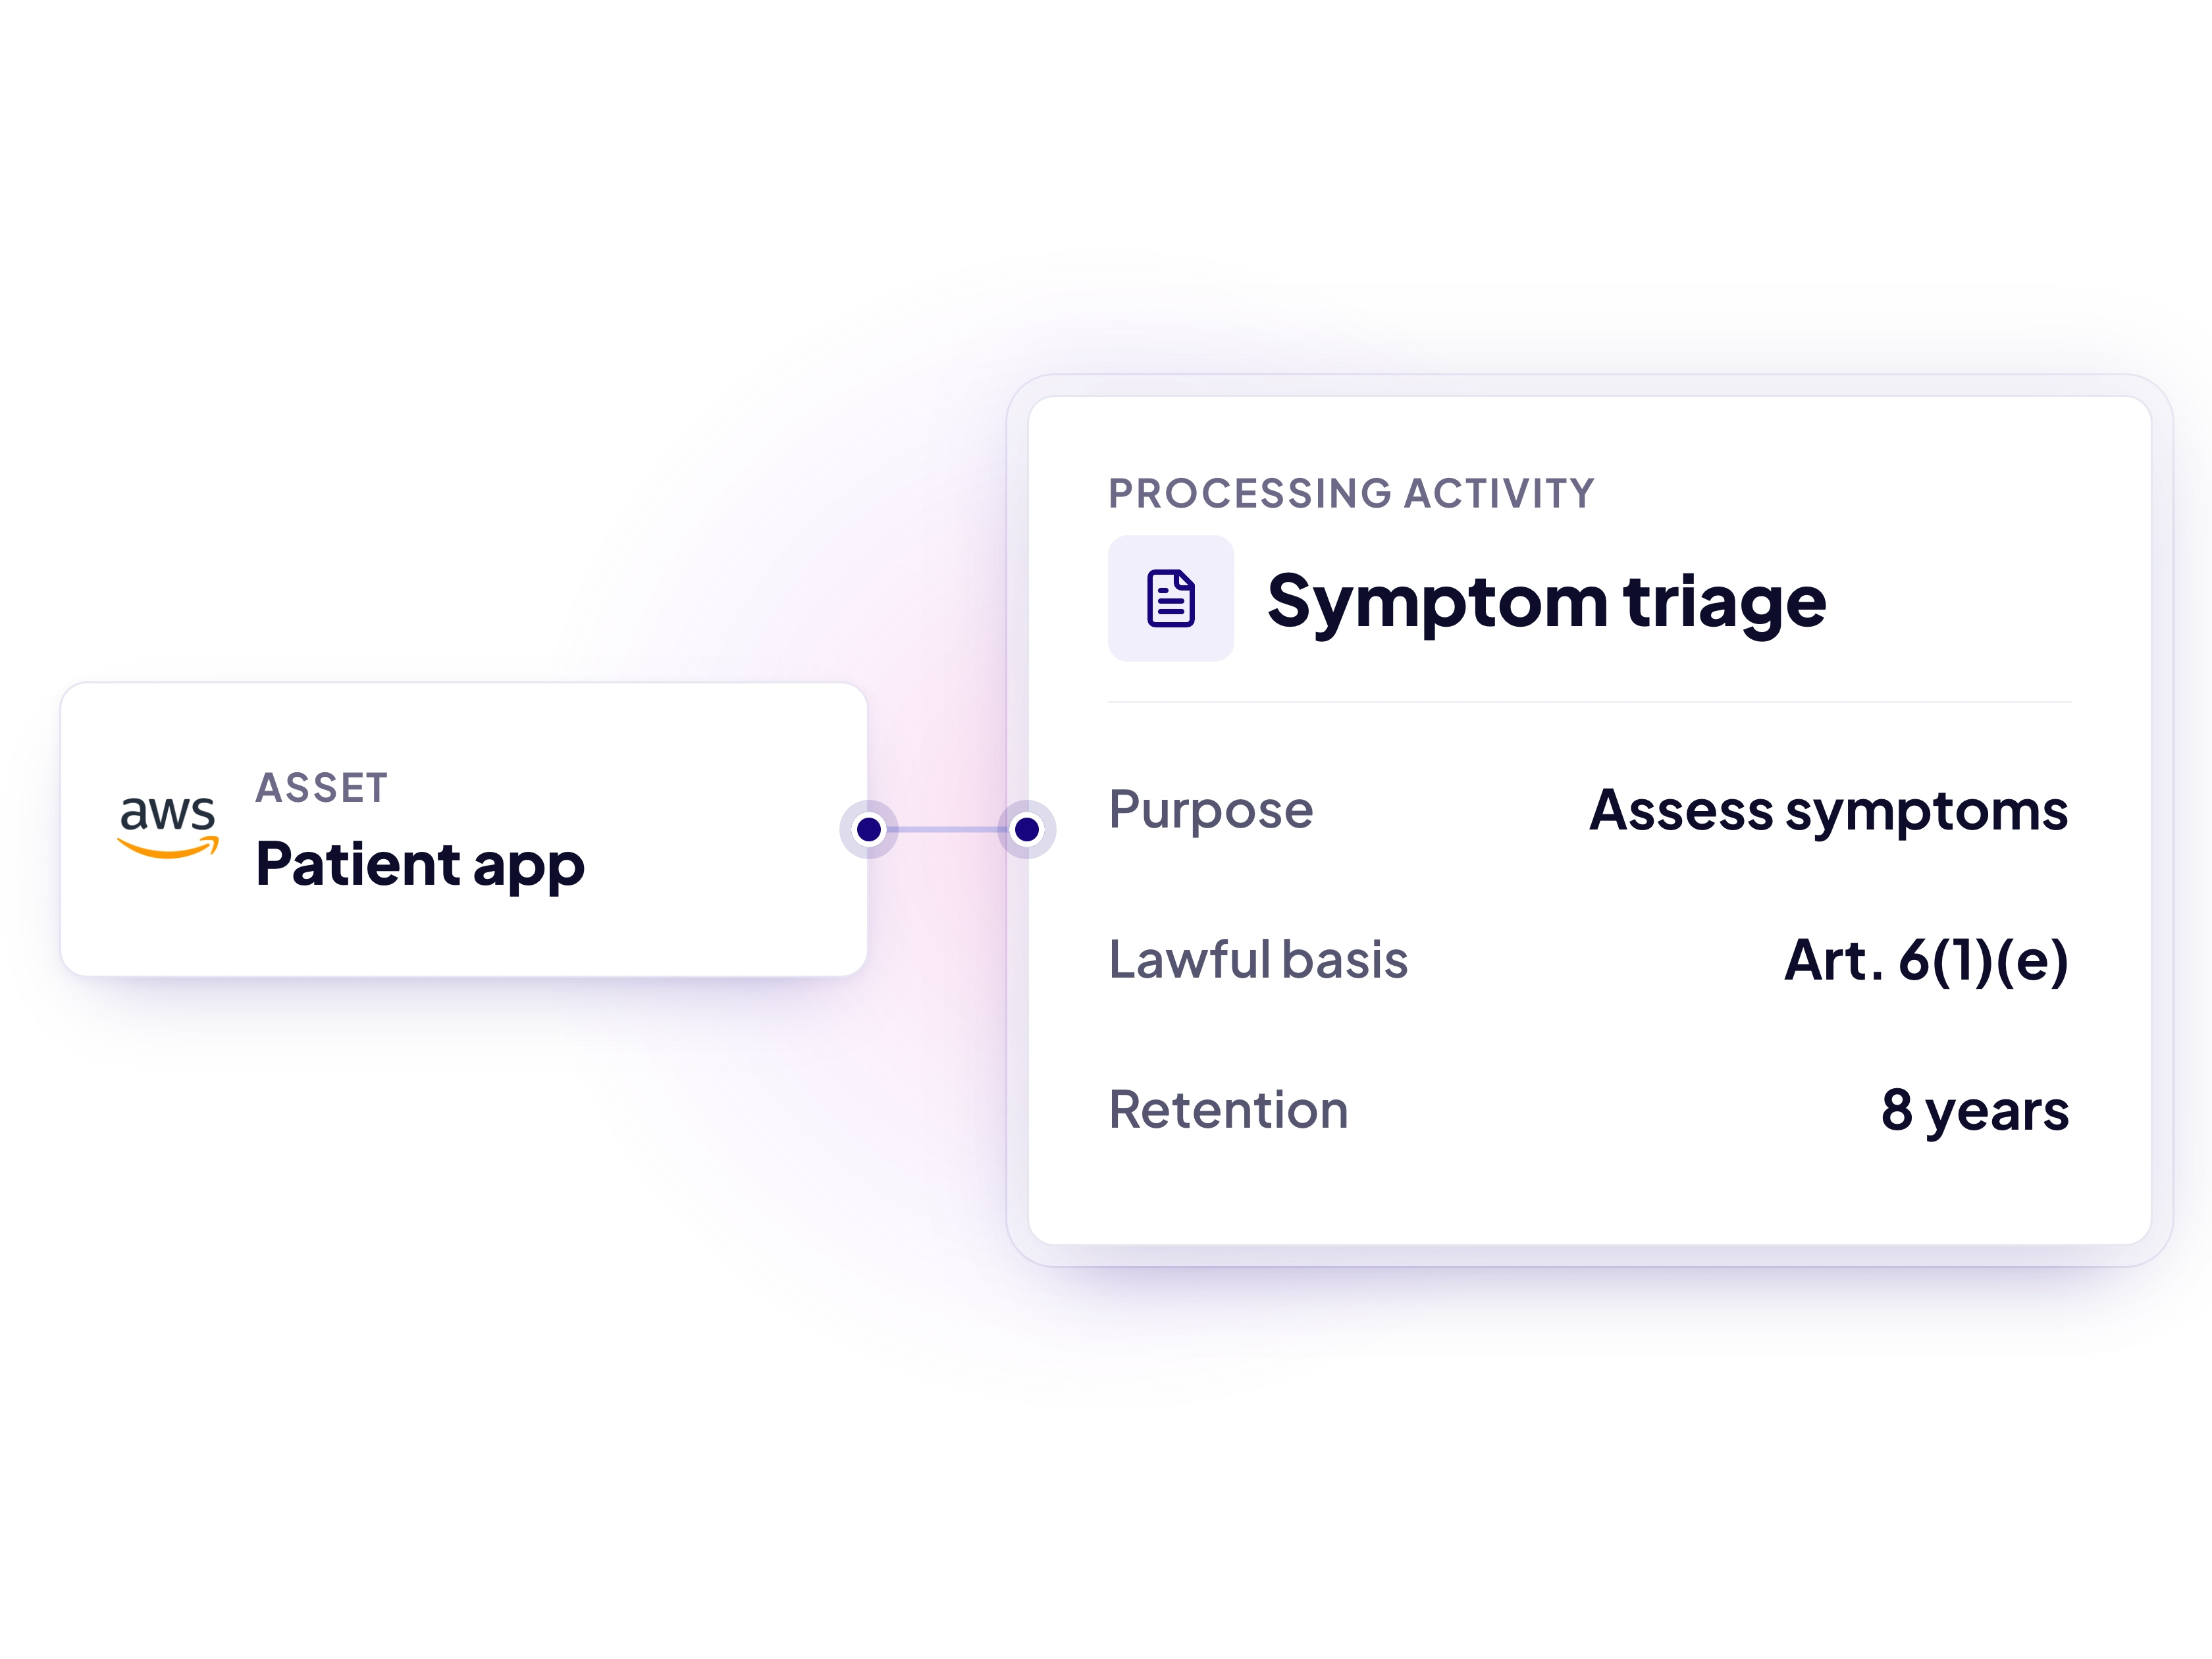
Patient app asset linked to the symptom triage processing activity, with purpose, lawful basis and retention

Draft data protection impact assessments using information you already have

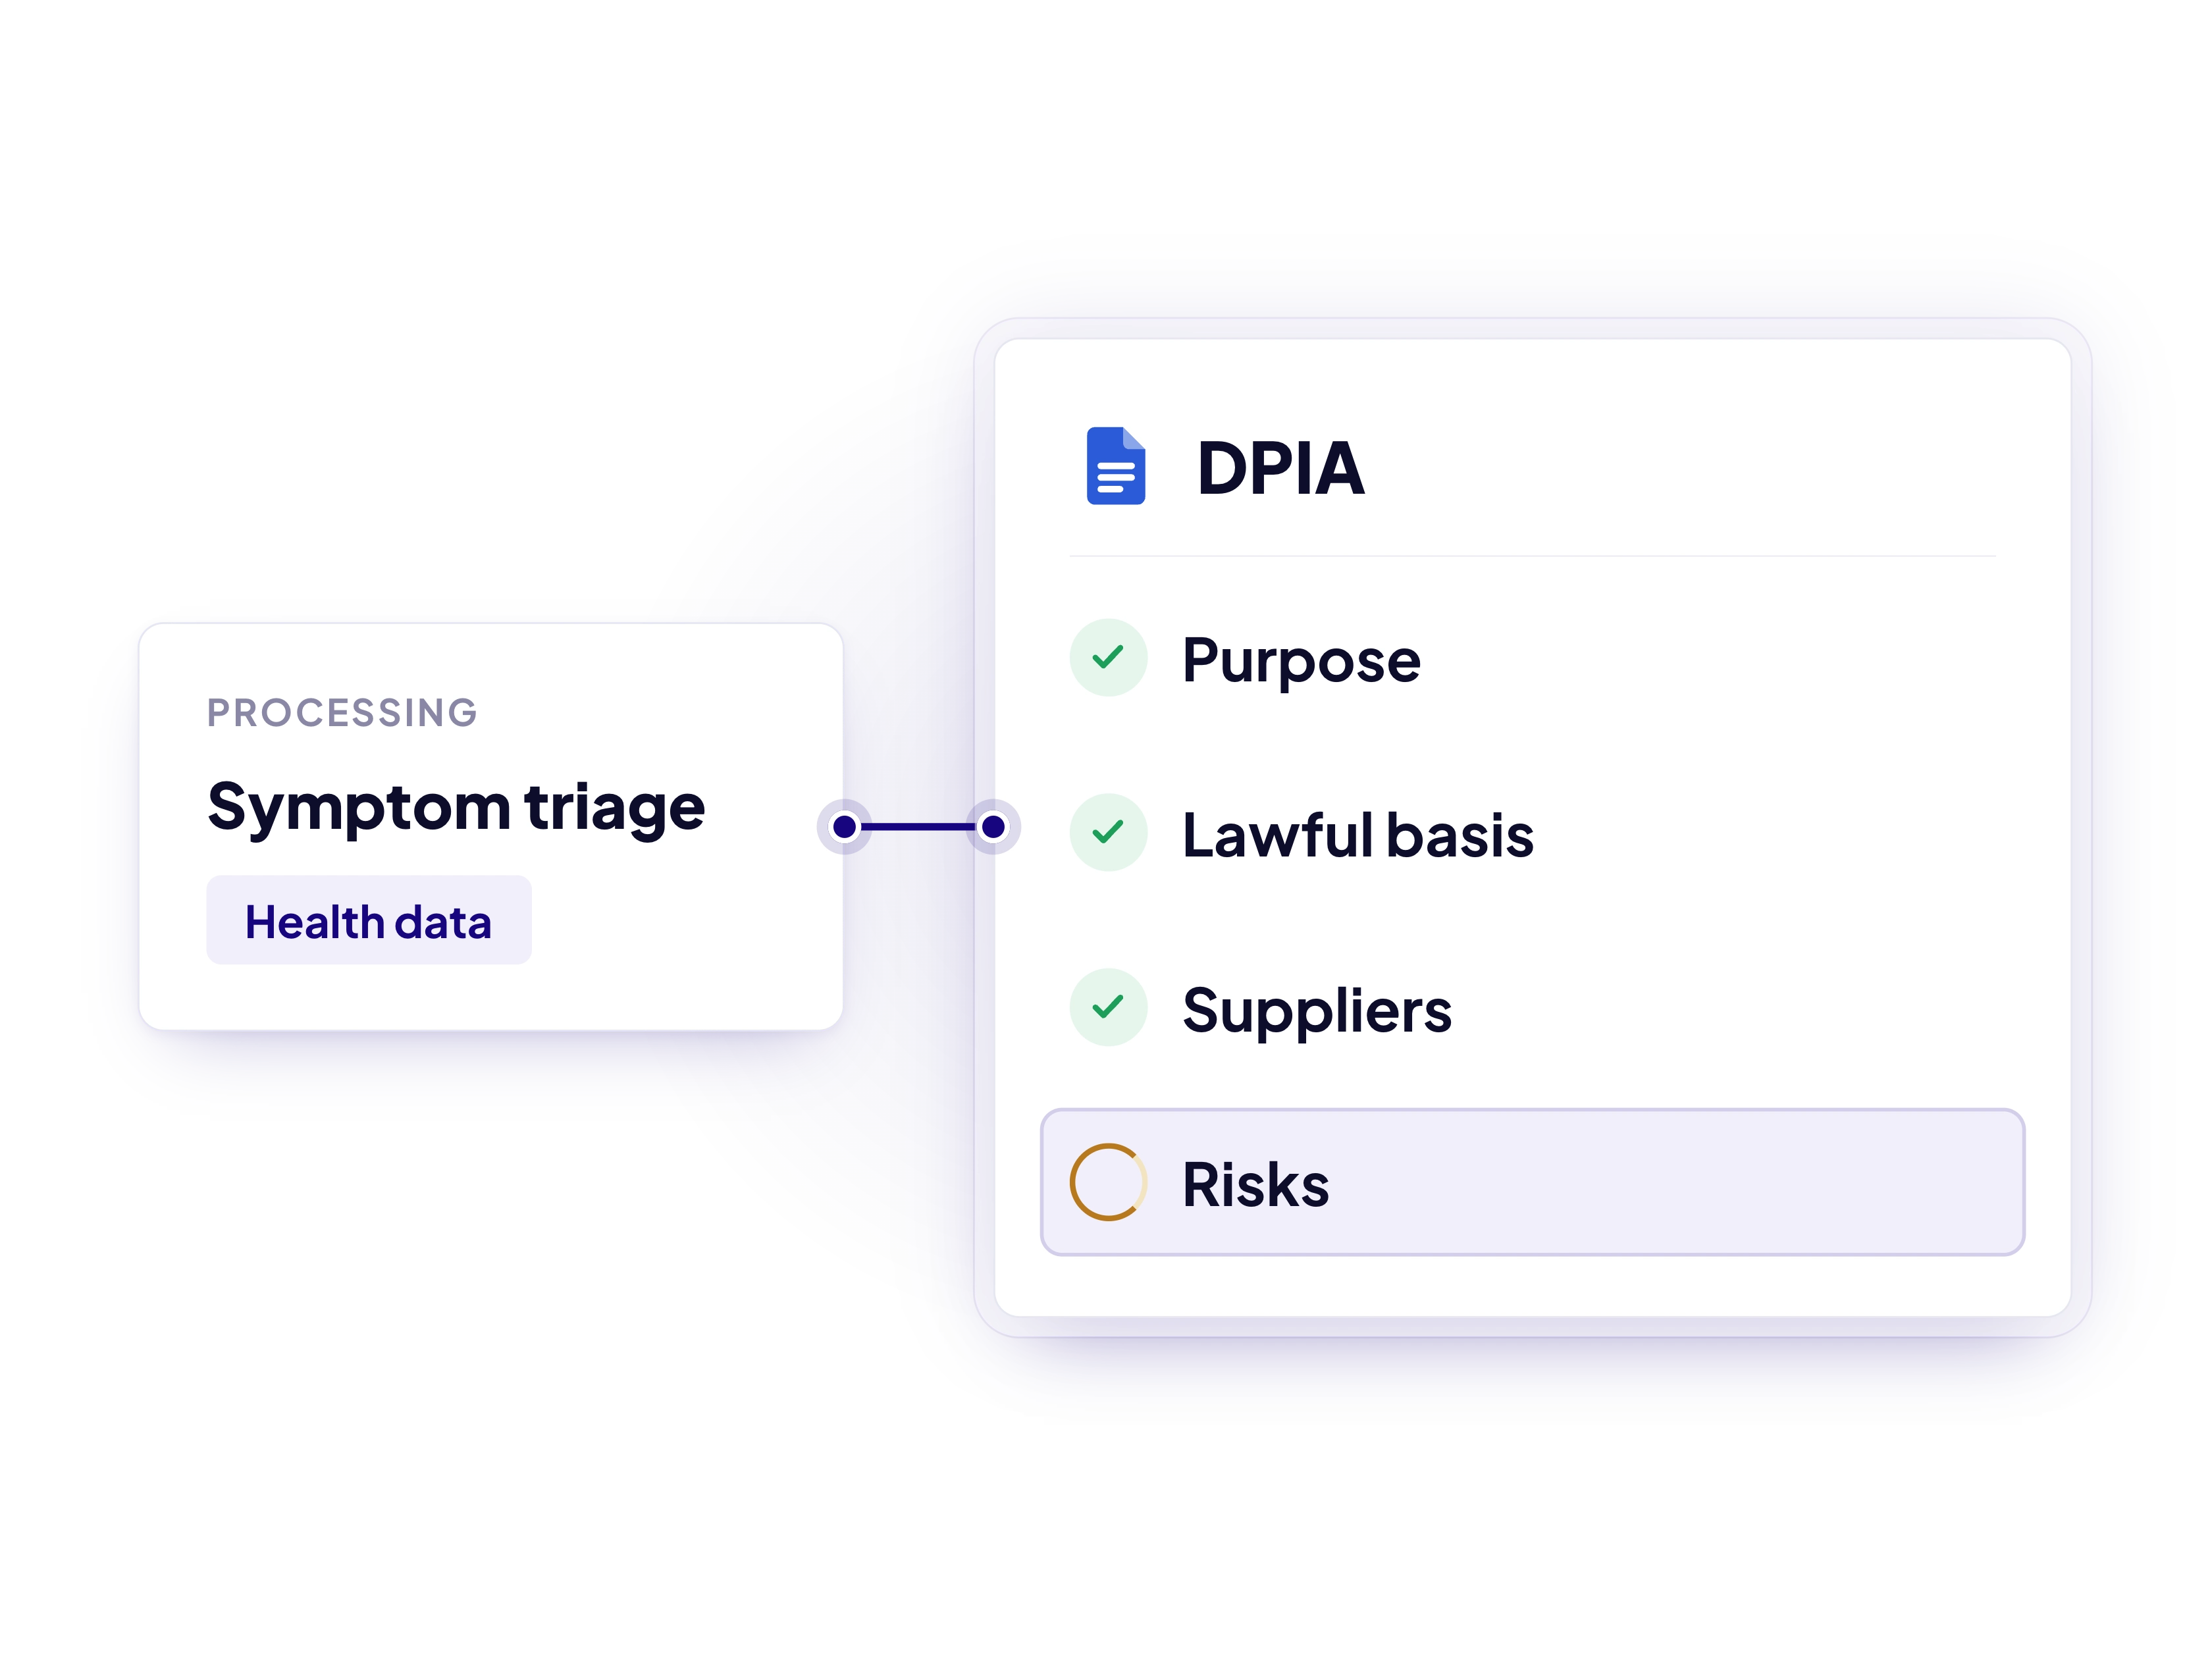
Use information already in Assuric to help draft DPIAs. Review the draft, assess risks and manage approvals in one place.

DPIA linked to a symptom triage processing activity, with purpose, lawful basis and suppliers complete

Answer security and IG questionnaires from your own evidence

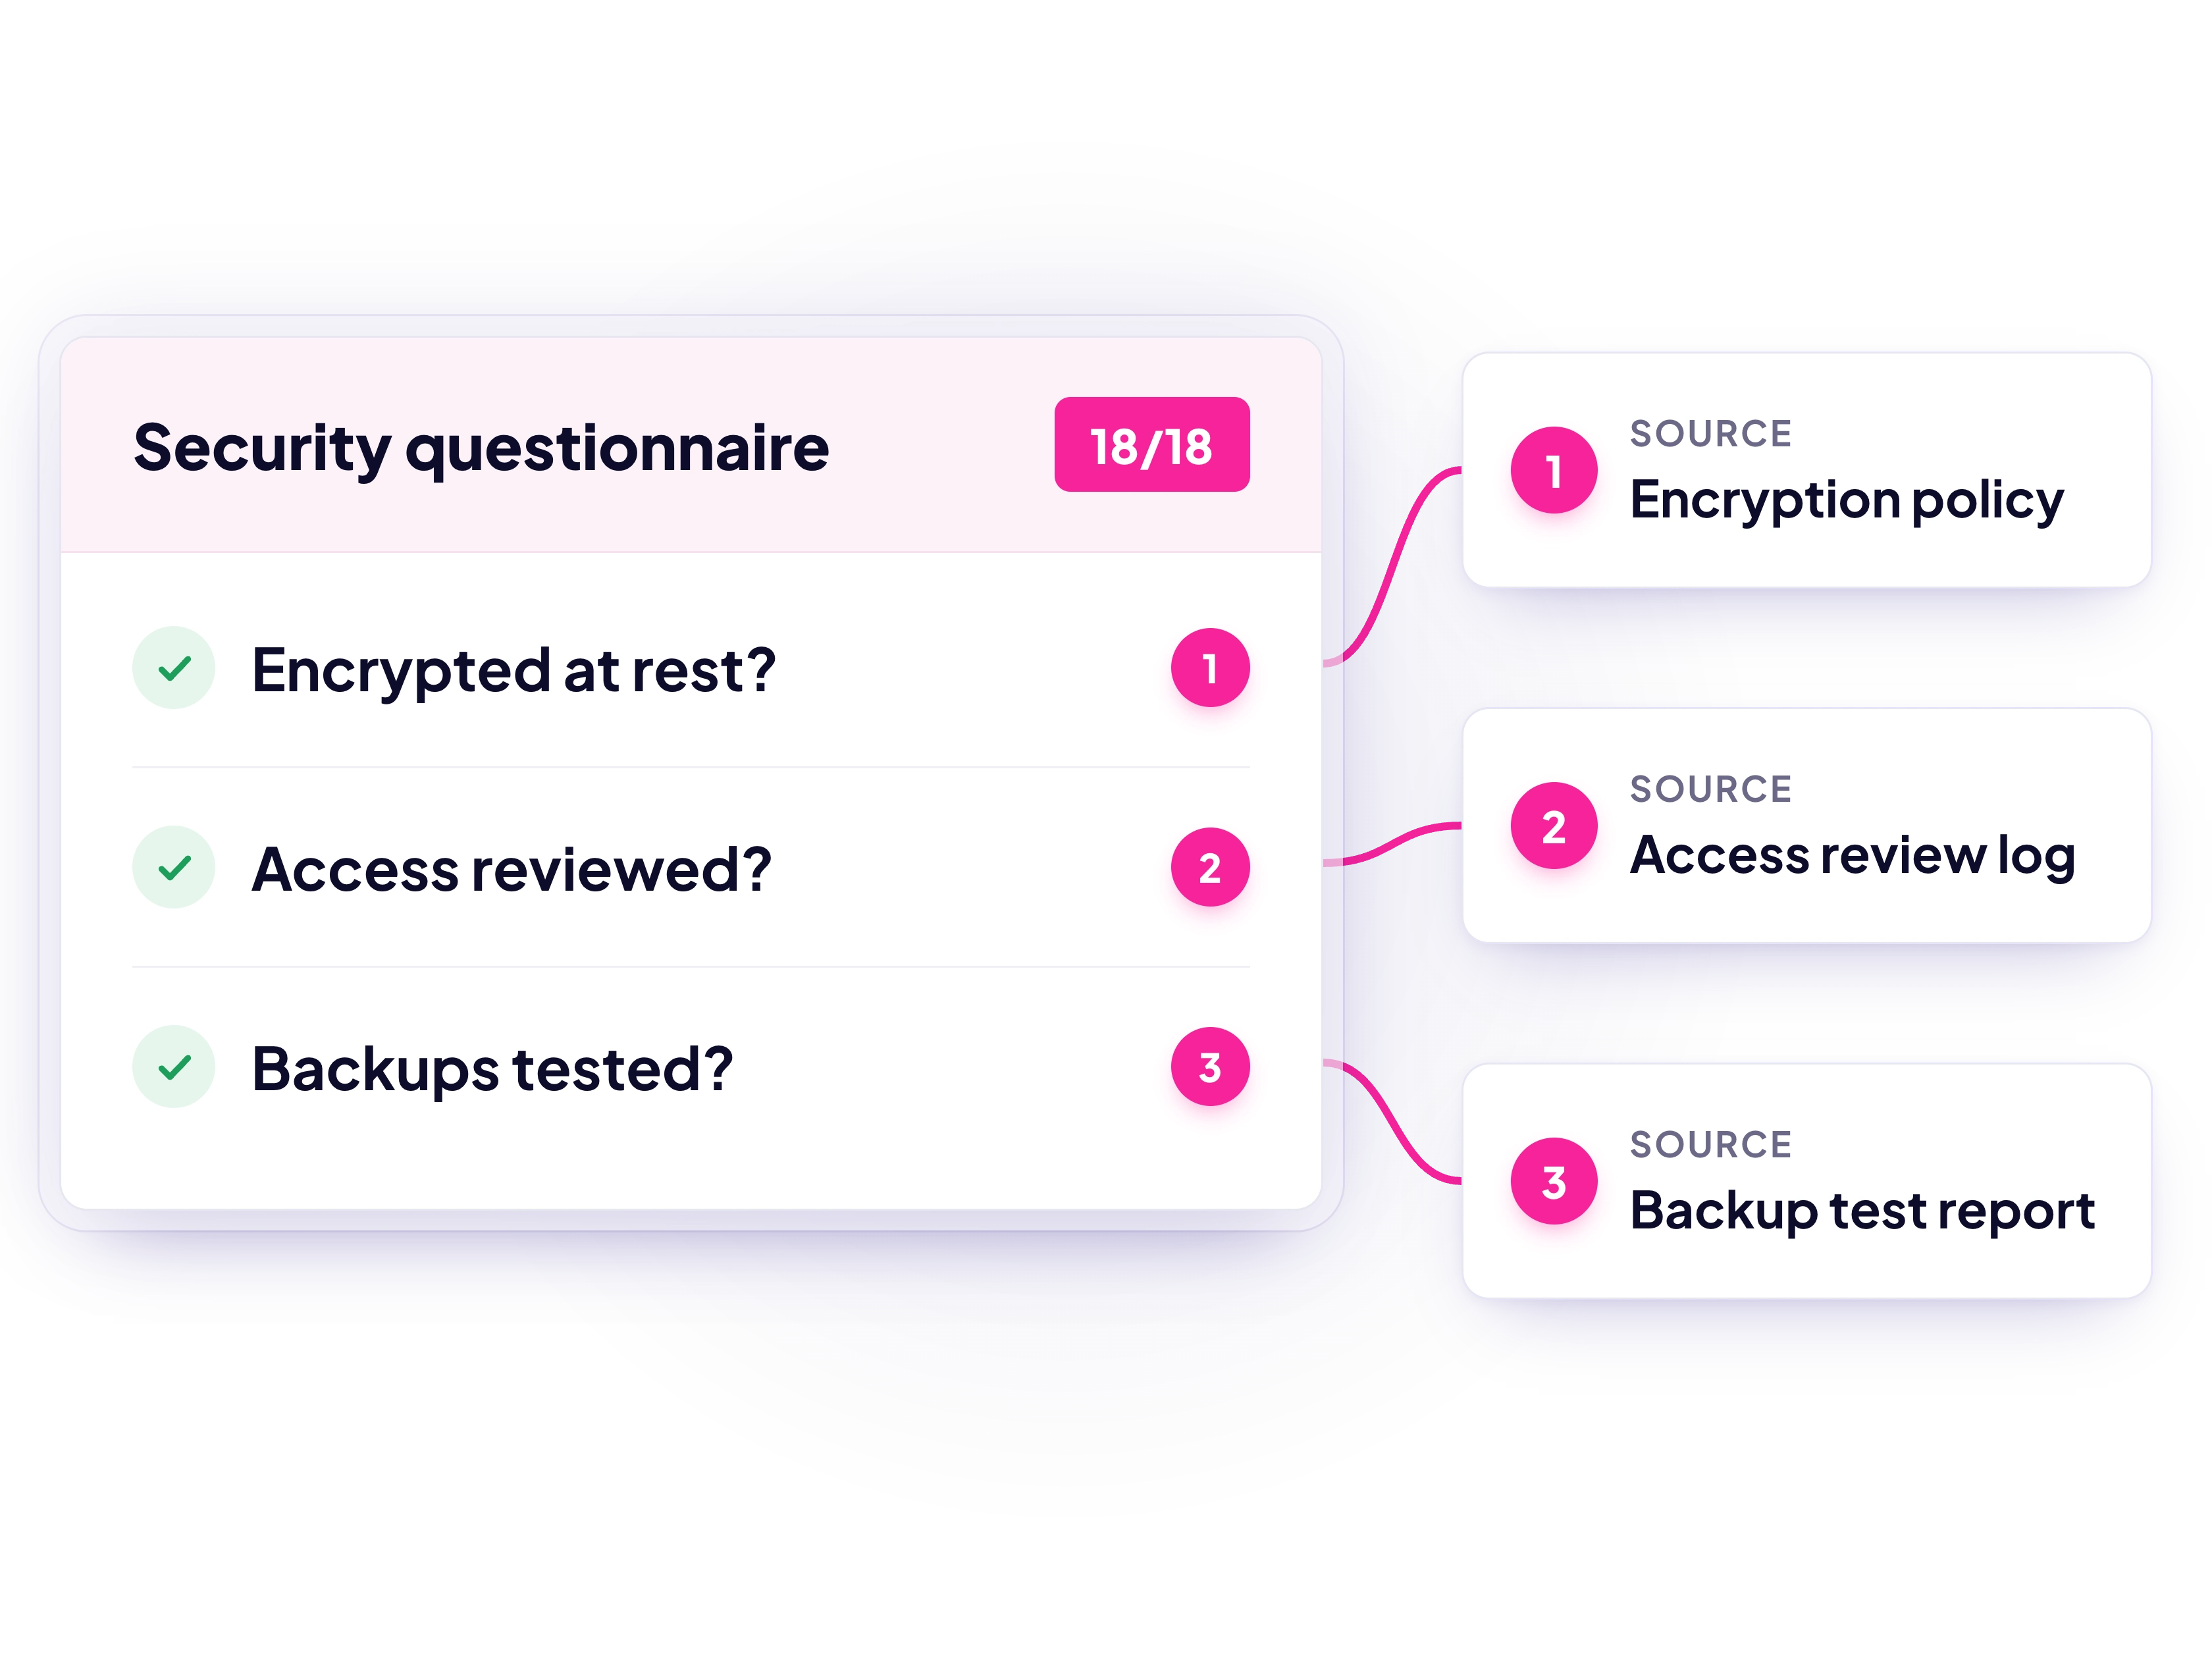
NHS and enterprise security and information governance questionnaires are drafted from your approved policies and evidence, with every answer cited, so your team reviews rather than writes from scratch.

Security questionnaire with each answer linked to its source policy, log or report

Use the same evidence to meet requirements across multiple frameworks

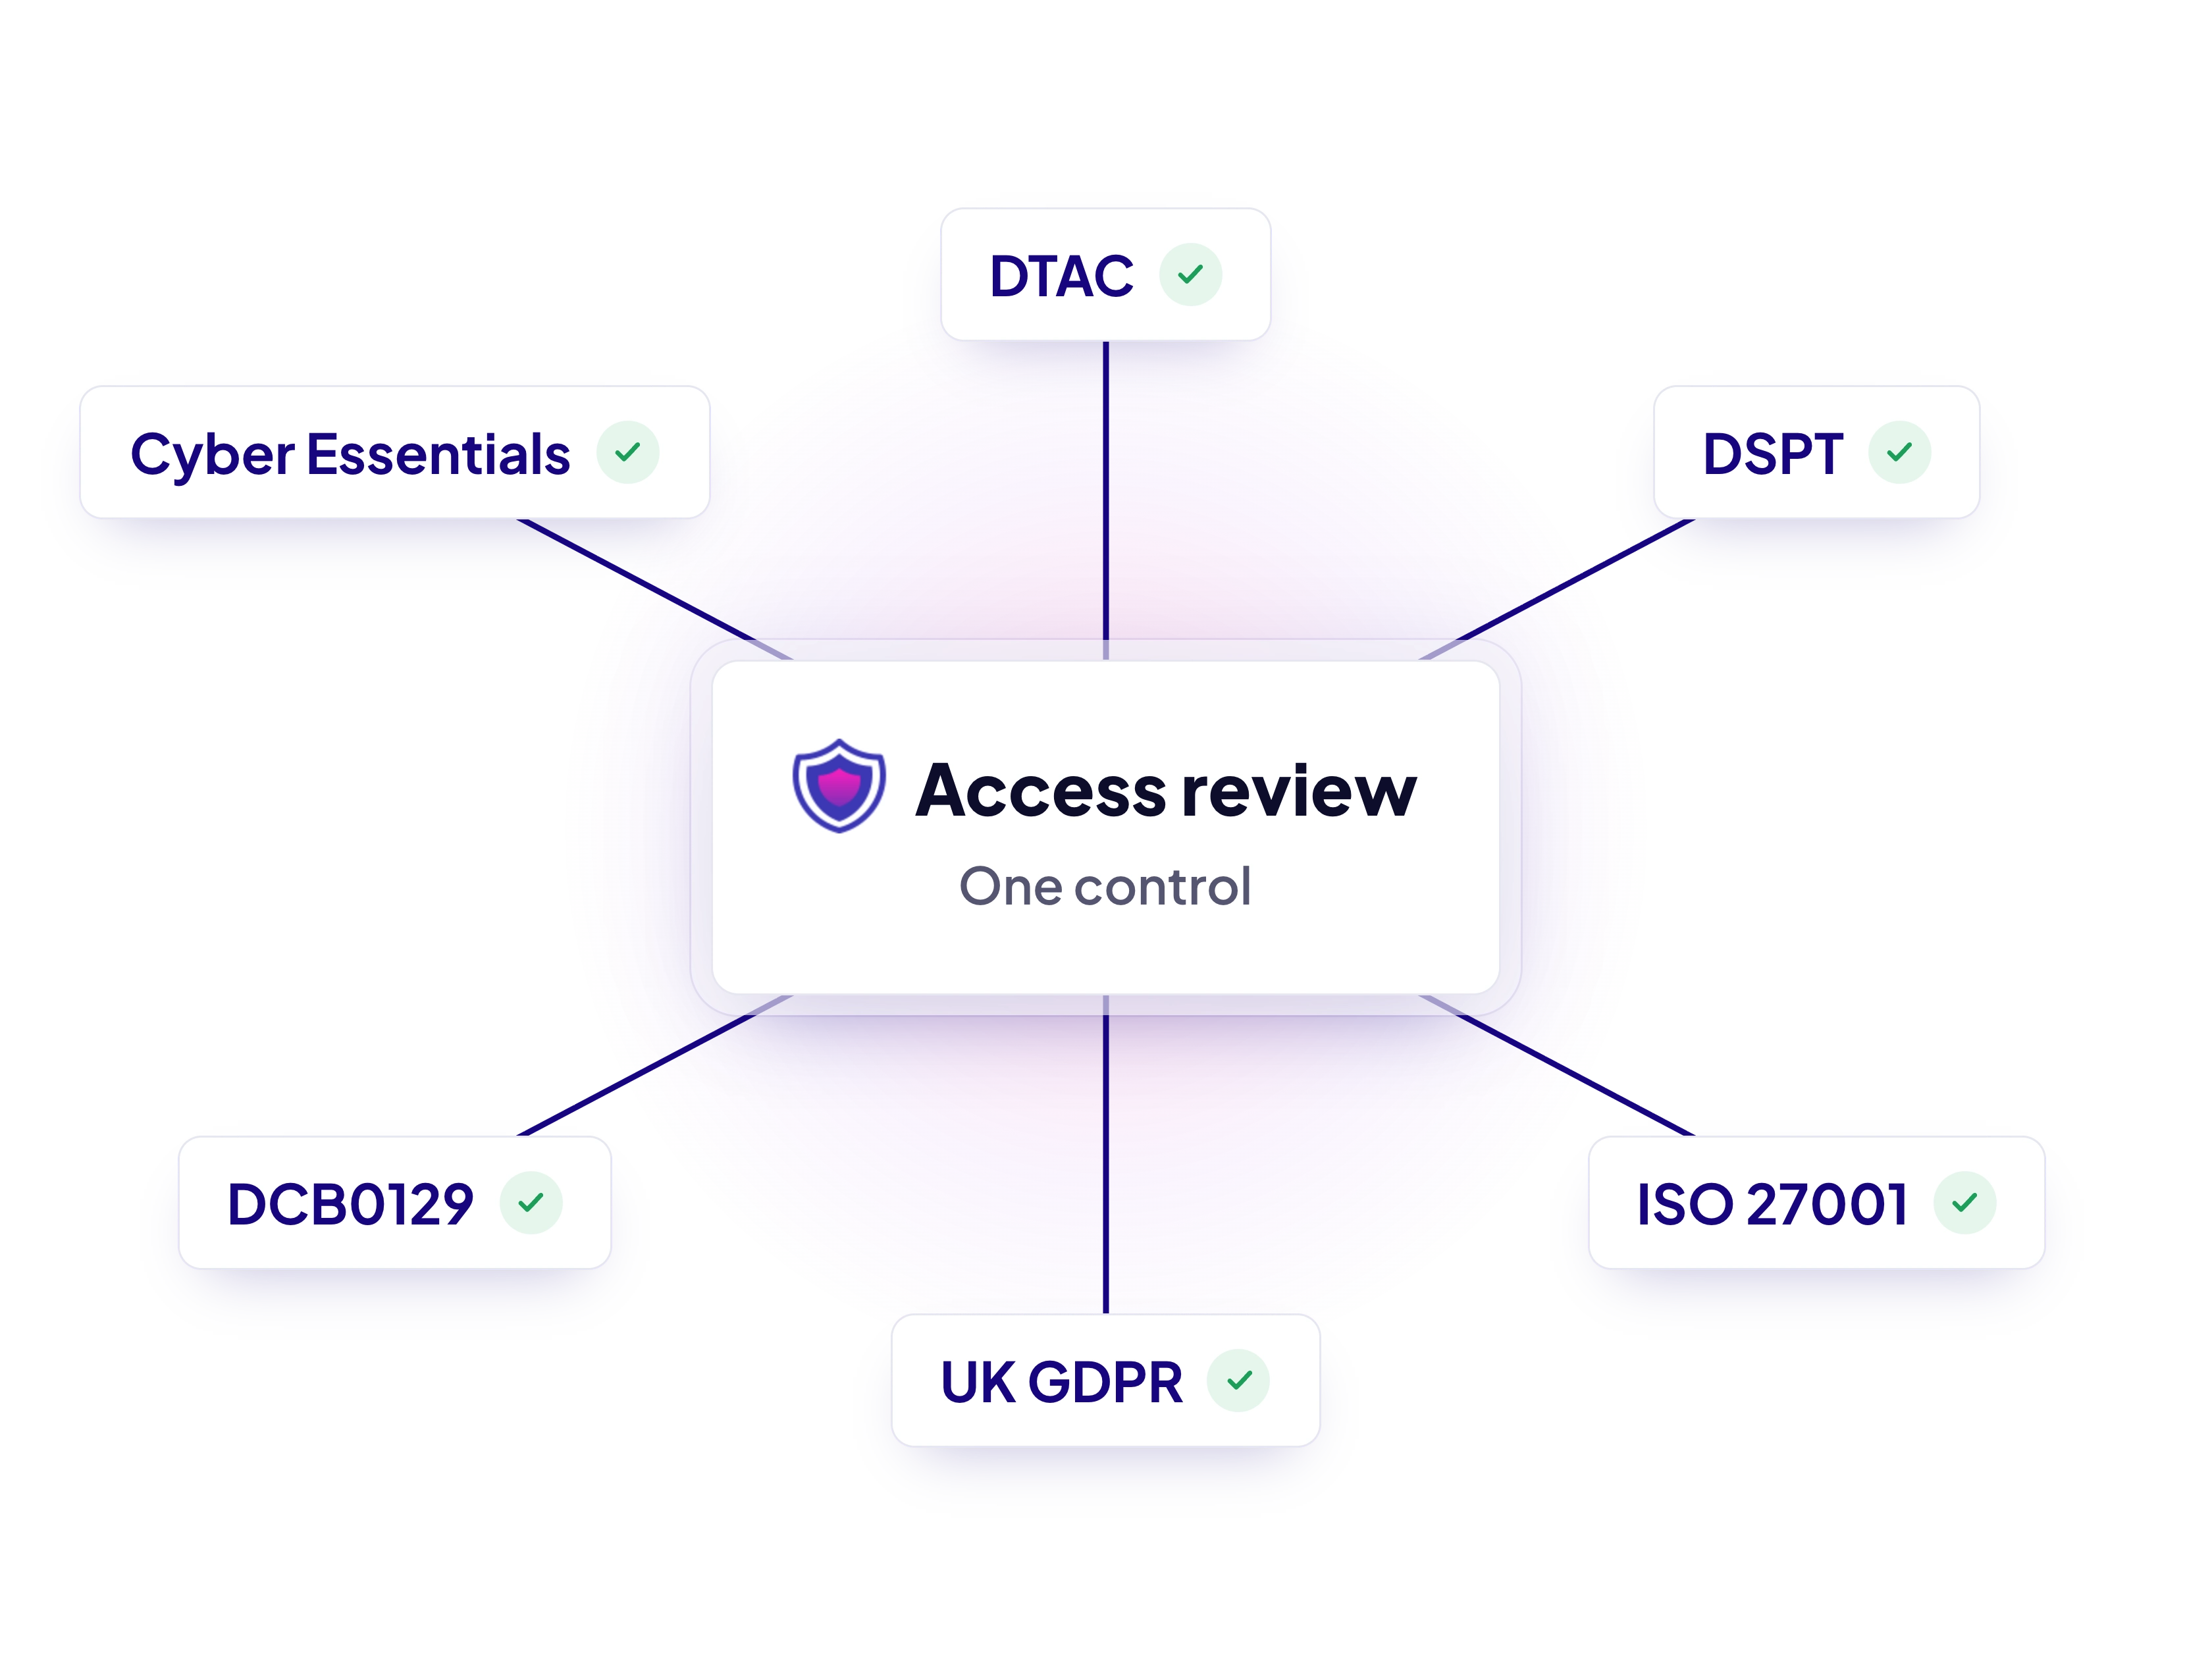
UK GDPR, DSPT, ISO 27001, Cyber Essentials and DTAC often ask for similar information. Assuric maps overlapping requirements so you can reuse evidence across frameworks rather than doing the same work twice.

One access review control mapped to DTAC, DSPT, DCB0129, UK GDPR, ISO 27001 and Cyber Essentials

AI that keeps your records current

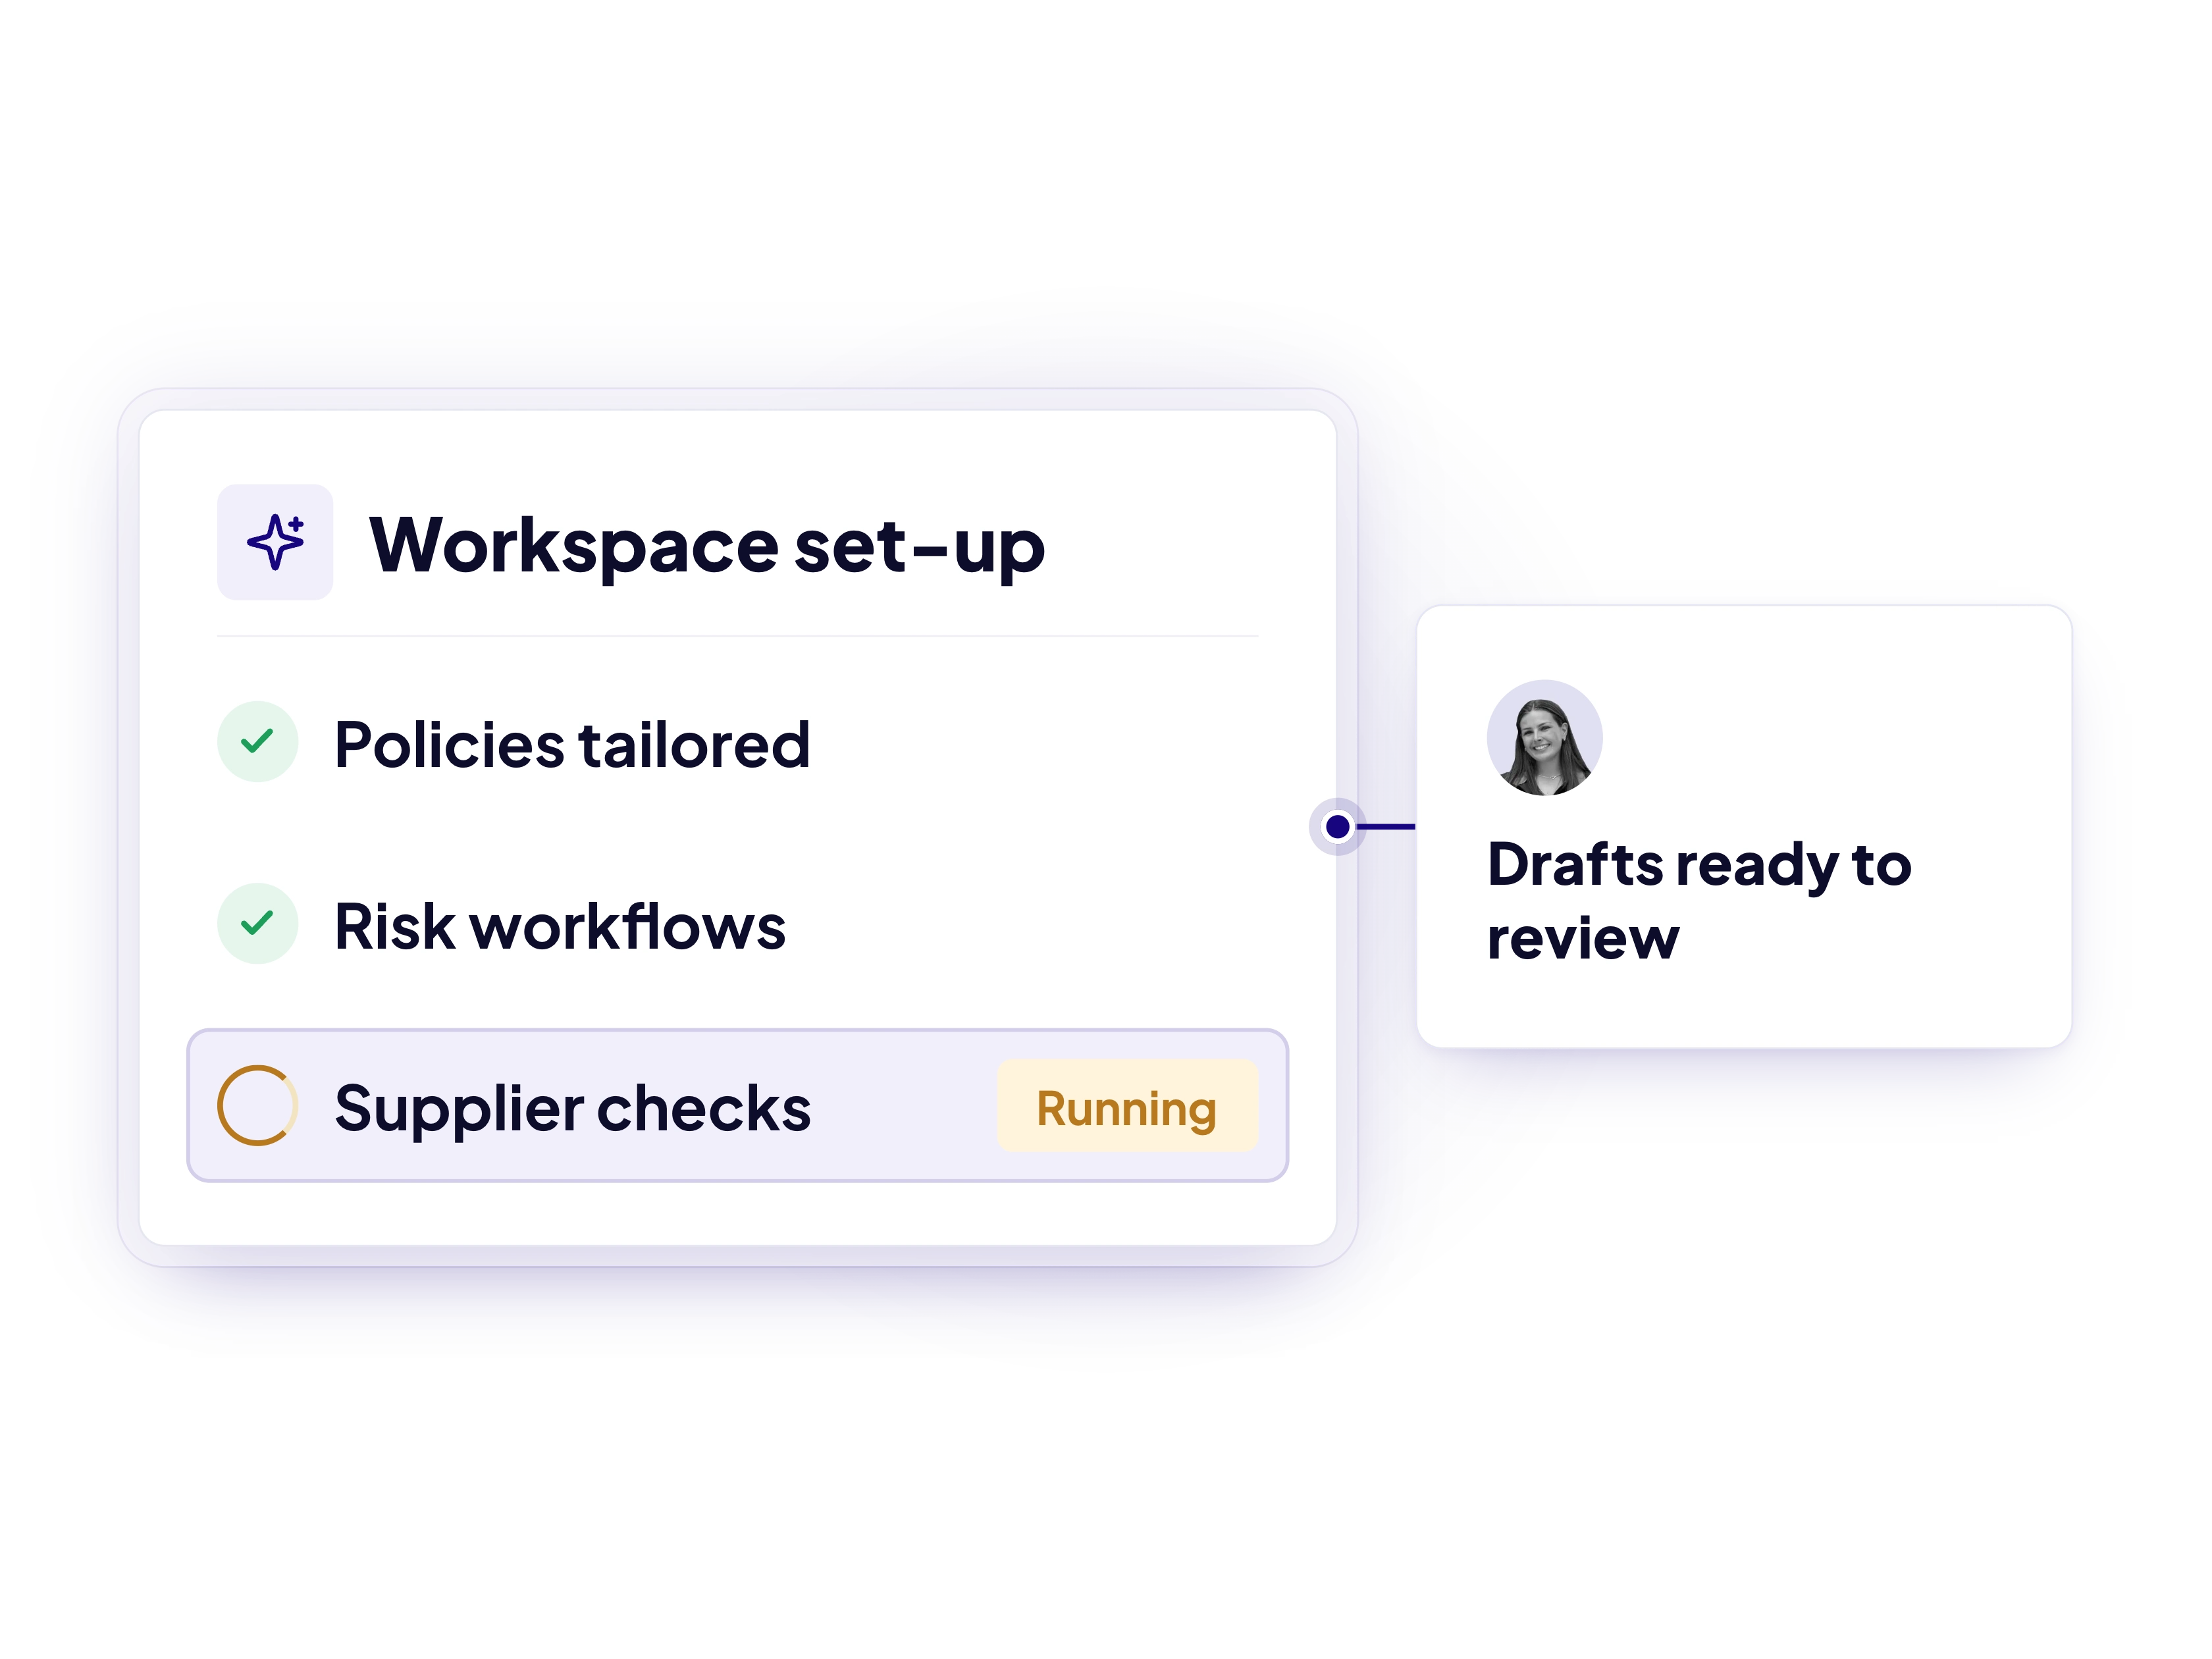
When your product or data processing changes, Assuric AI drafts updates to your RoPA, DPIAs and policies and flags what needs reviewing, with every change approved by a named person.

AI workspace set-up tailoring policies and risk workflows, with drafts handed over for review

Features

Everything you need to manage data protection and security

From understanding how you use personal data to managing security risks and preparing for customer reviews, Assuric brings your compliance work together.

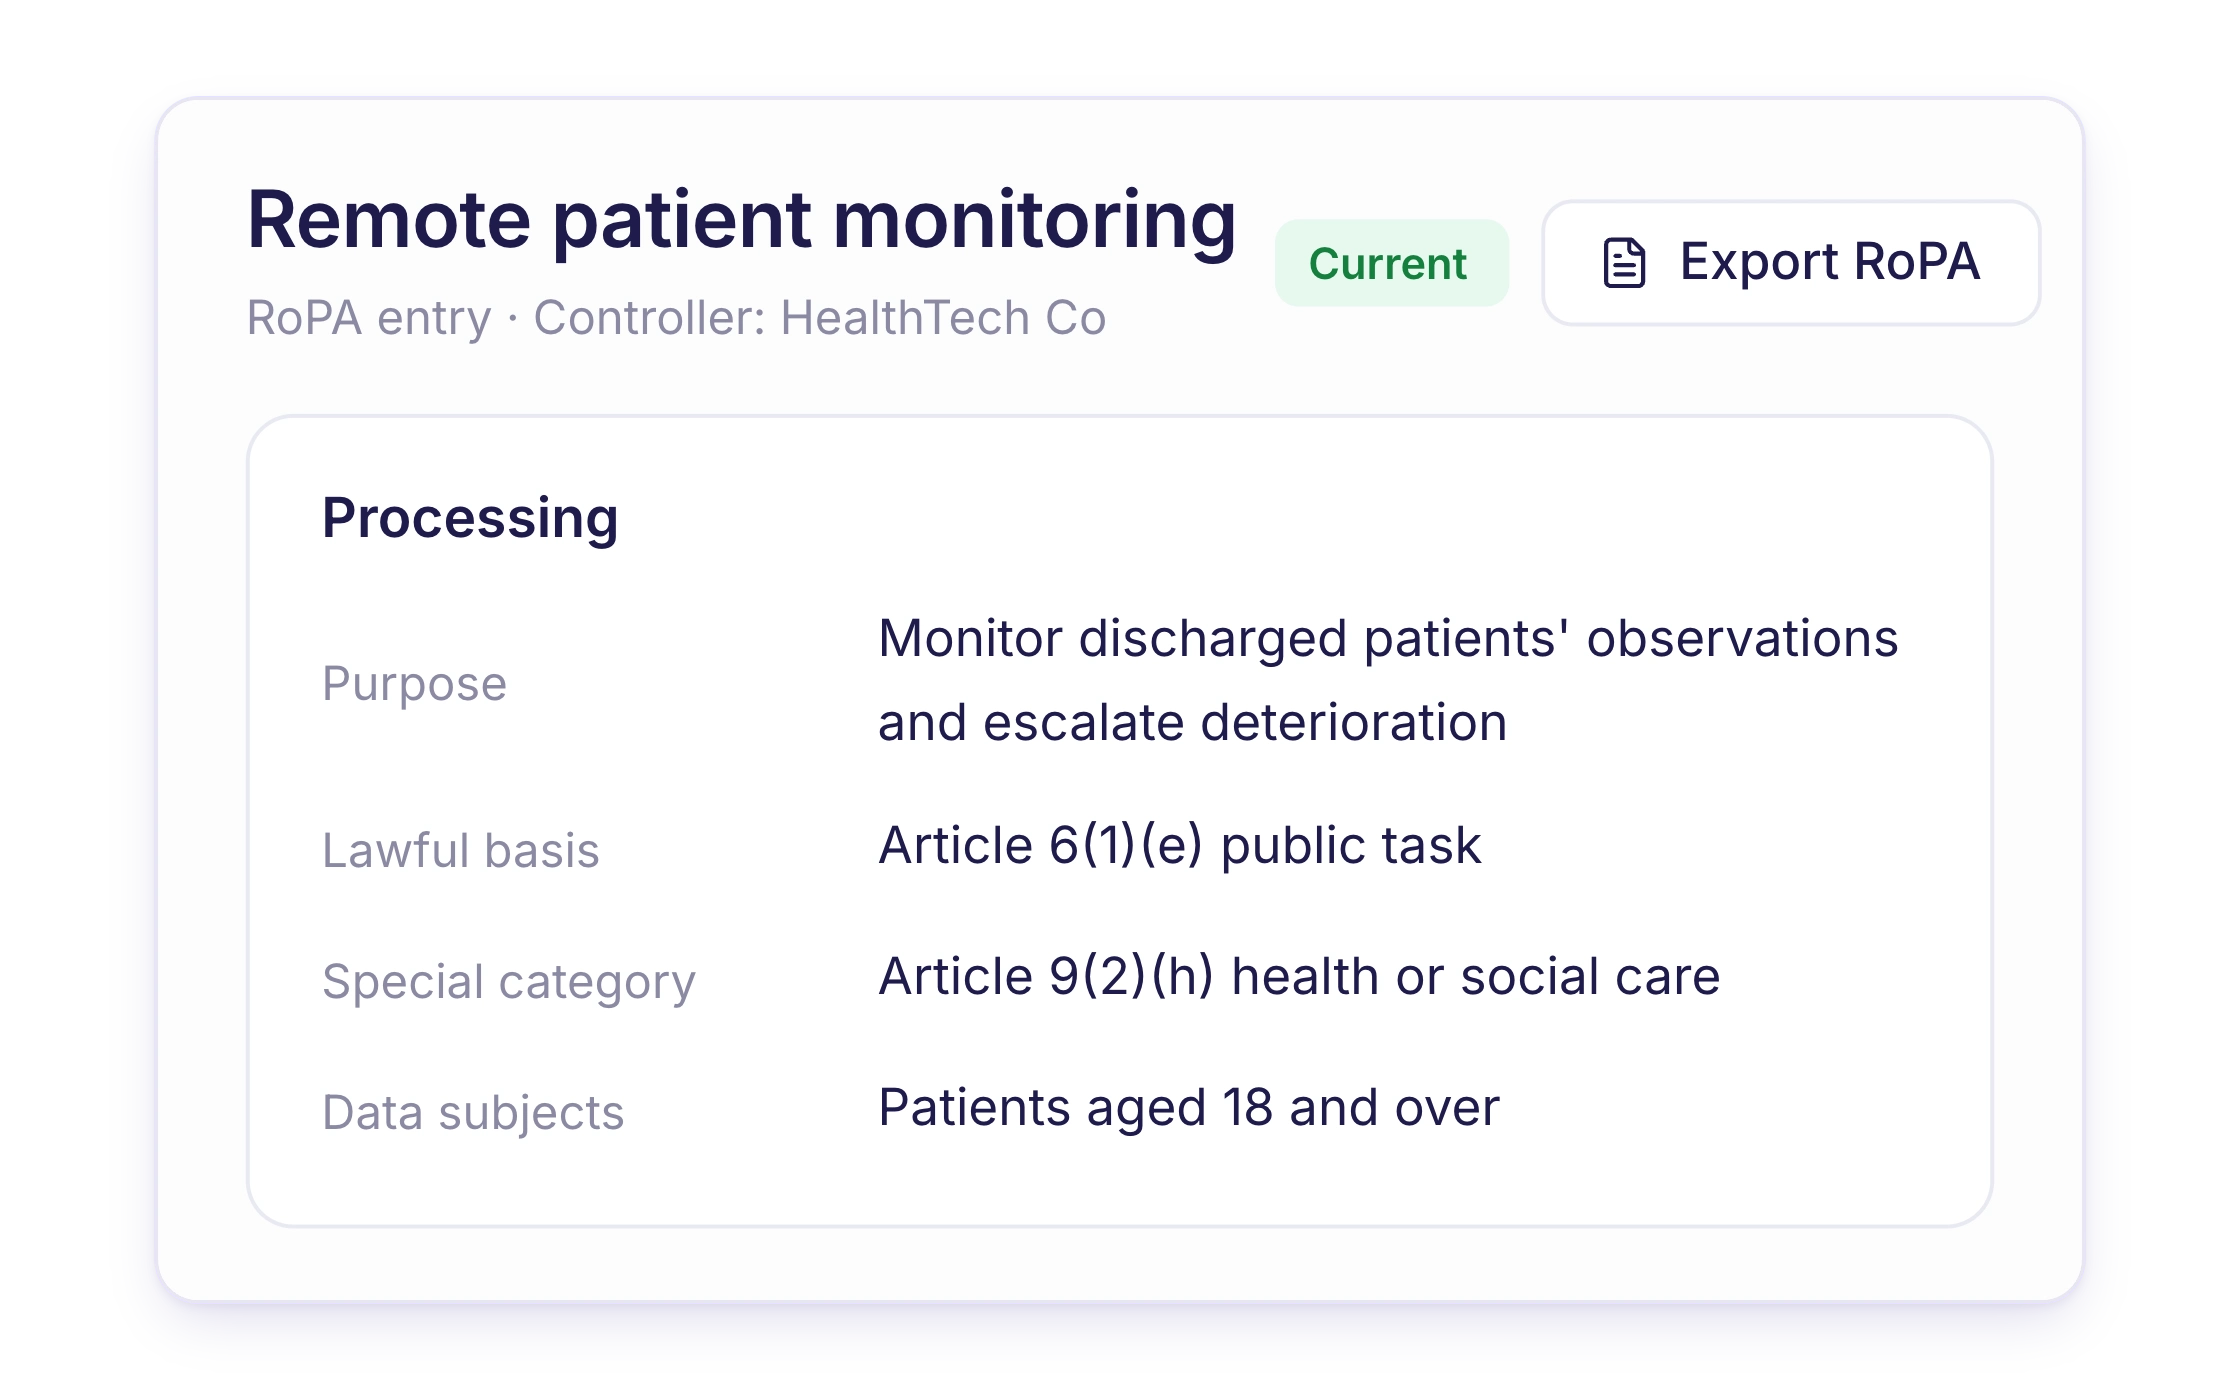
Record of processing activities, showing each purpose, data category and retention period

DPIAs and records of processing

Know exactly how you use personal data

Keep your records of processing activities (RoPA) and data protection impact assessments (DPIAs) in one place. Record what data you collect, why you use it, where it goes and how long you keep it. Use existing records to help draft new assessments.

Explore
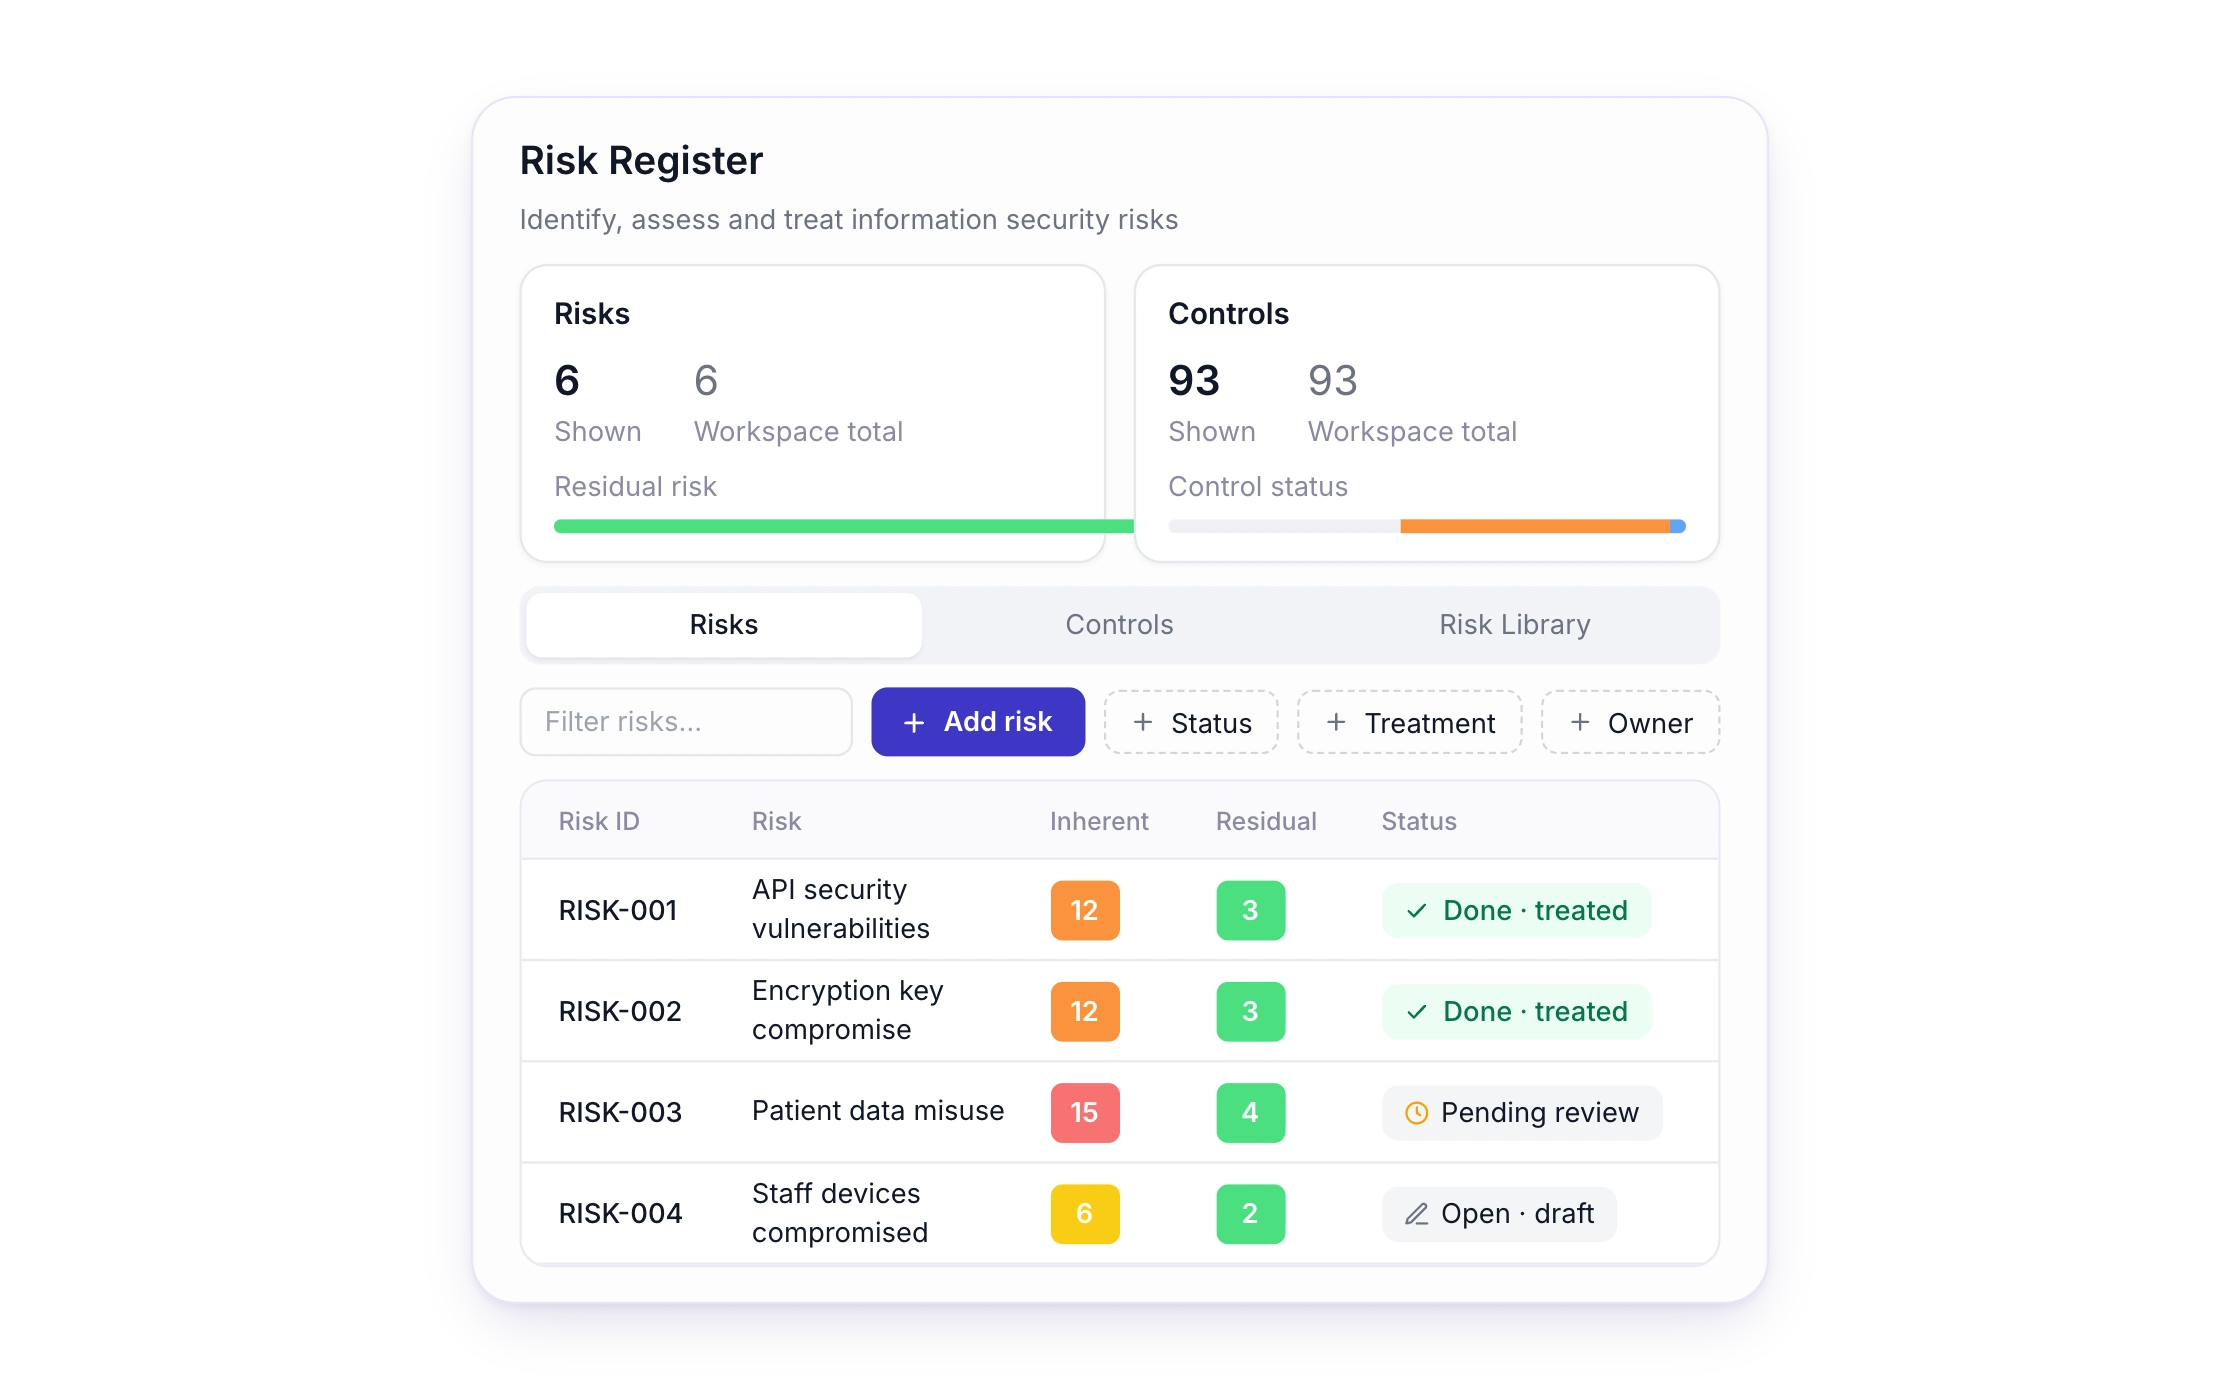
Information security risk register with scores, owners and actions

Security risk management

Identify and manage security risks

Record risks, assess their severity, assign actions and track progress. See which systems, suppliers and controls each risk relates to.

Explore
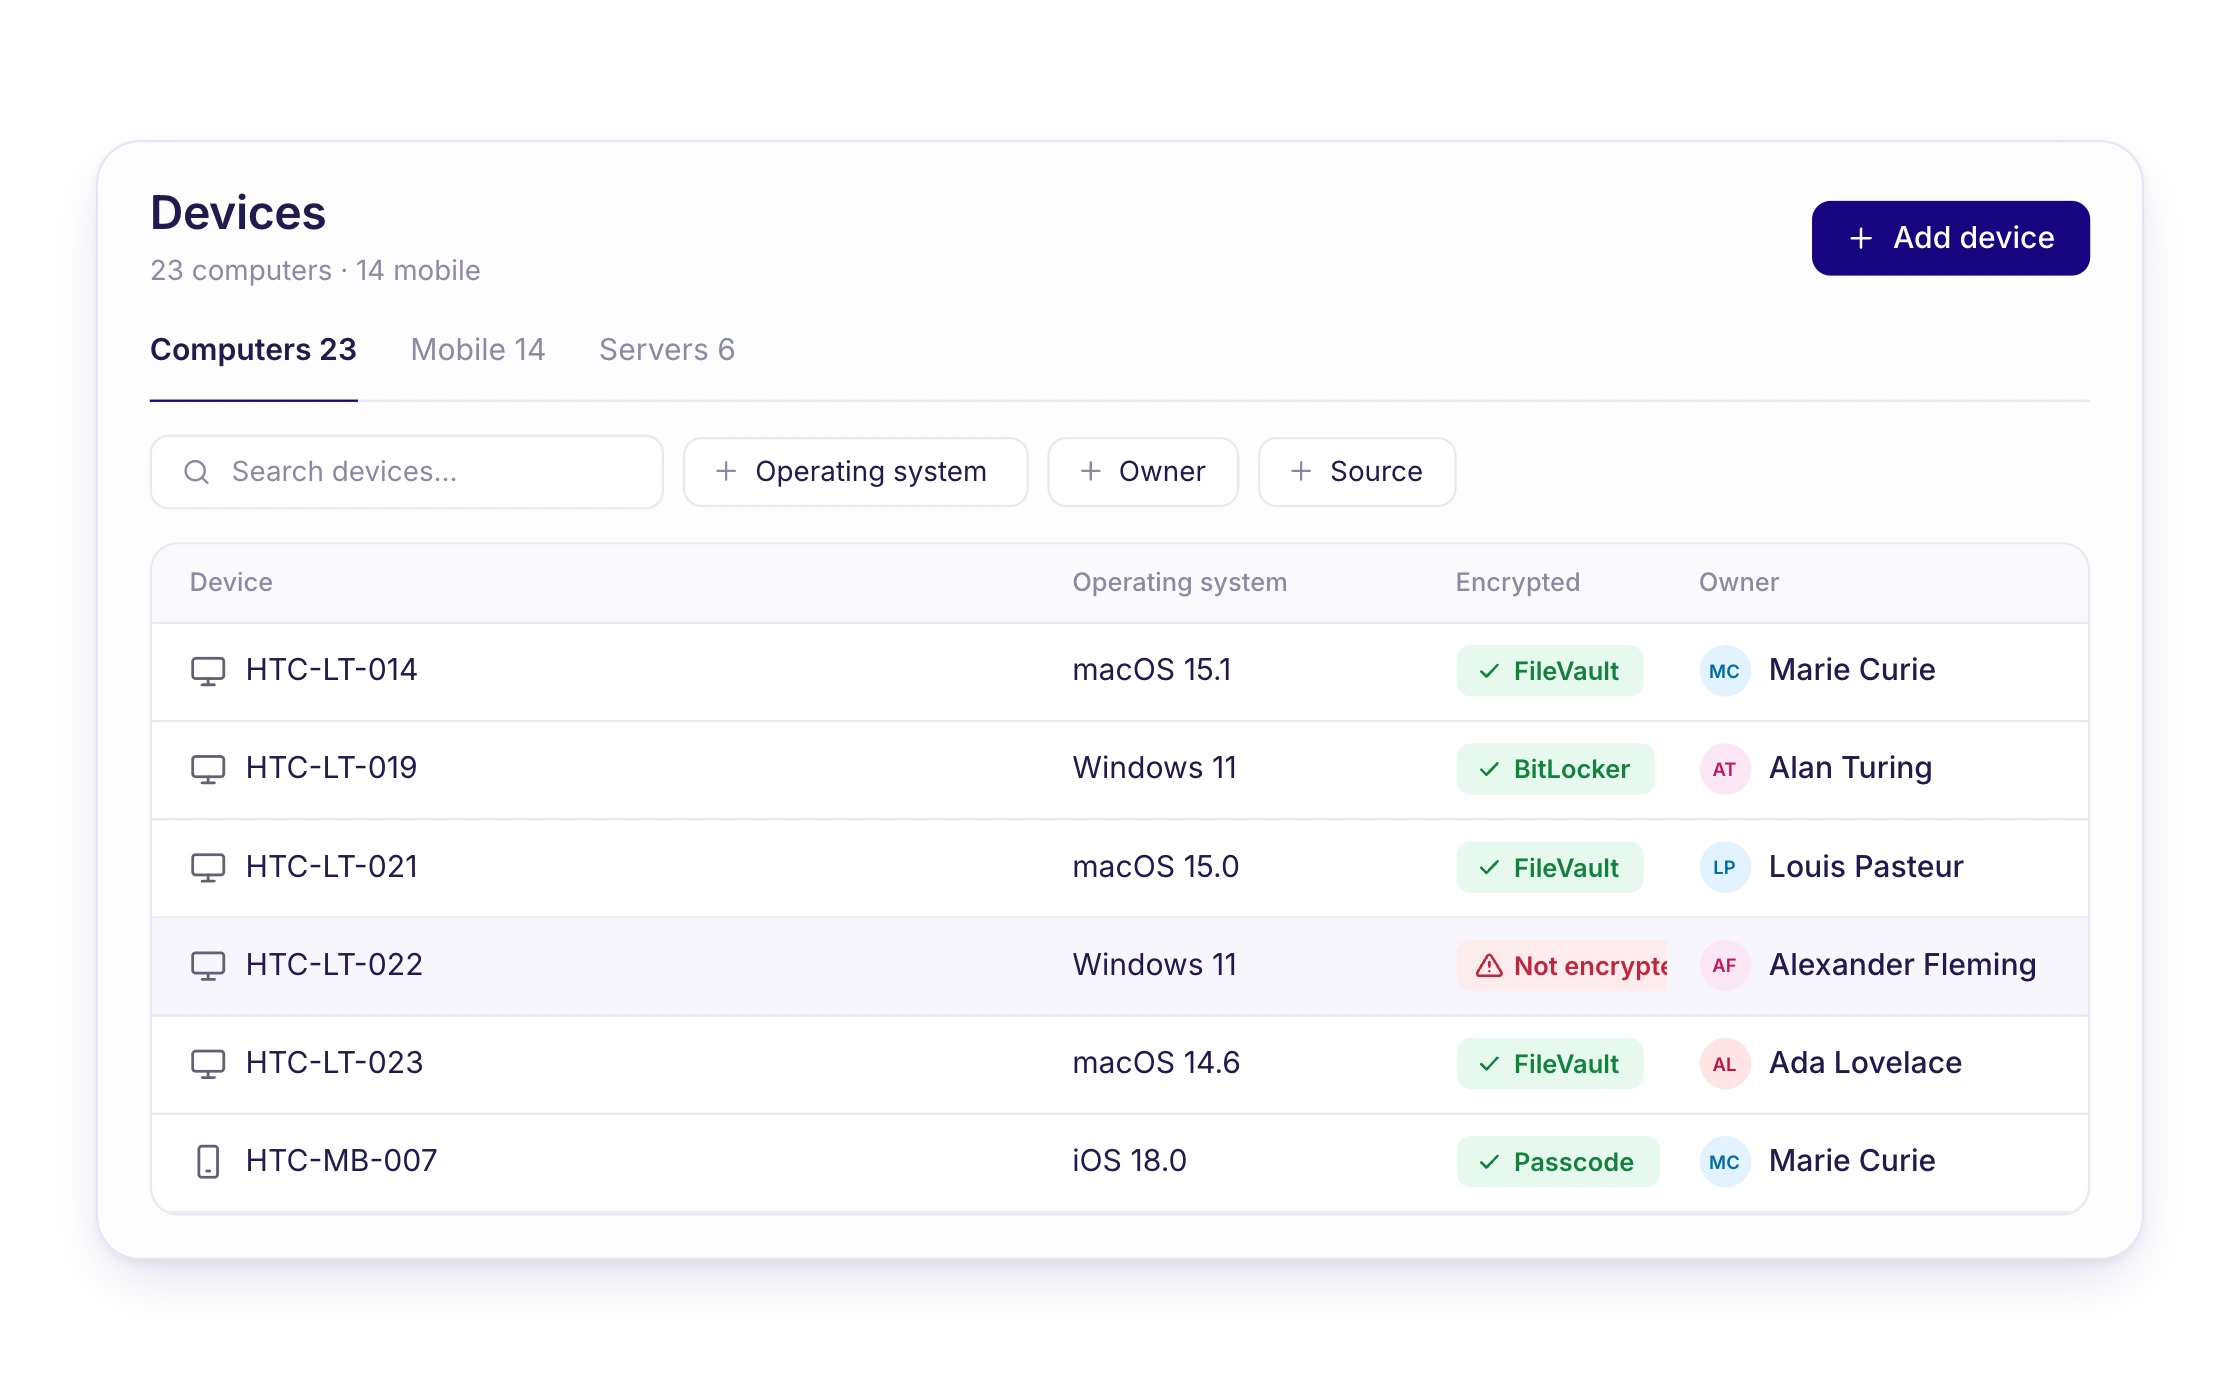
Register of company and personal computers and mobile devices

Asset and device management

Know which systems and devices you use

Maintain a register of information assets, cloud services and company or personal devices. See what needs protecting and let staff register devices through the Staff Portal.

Explore
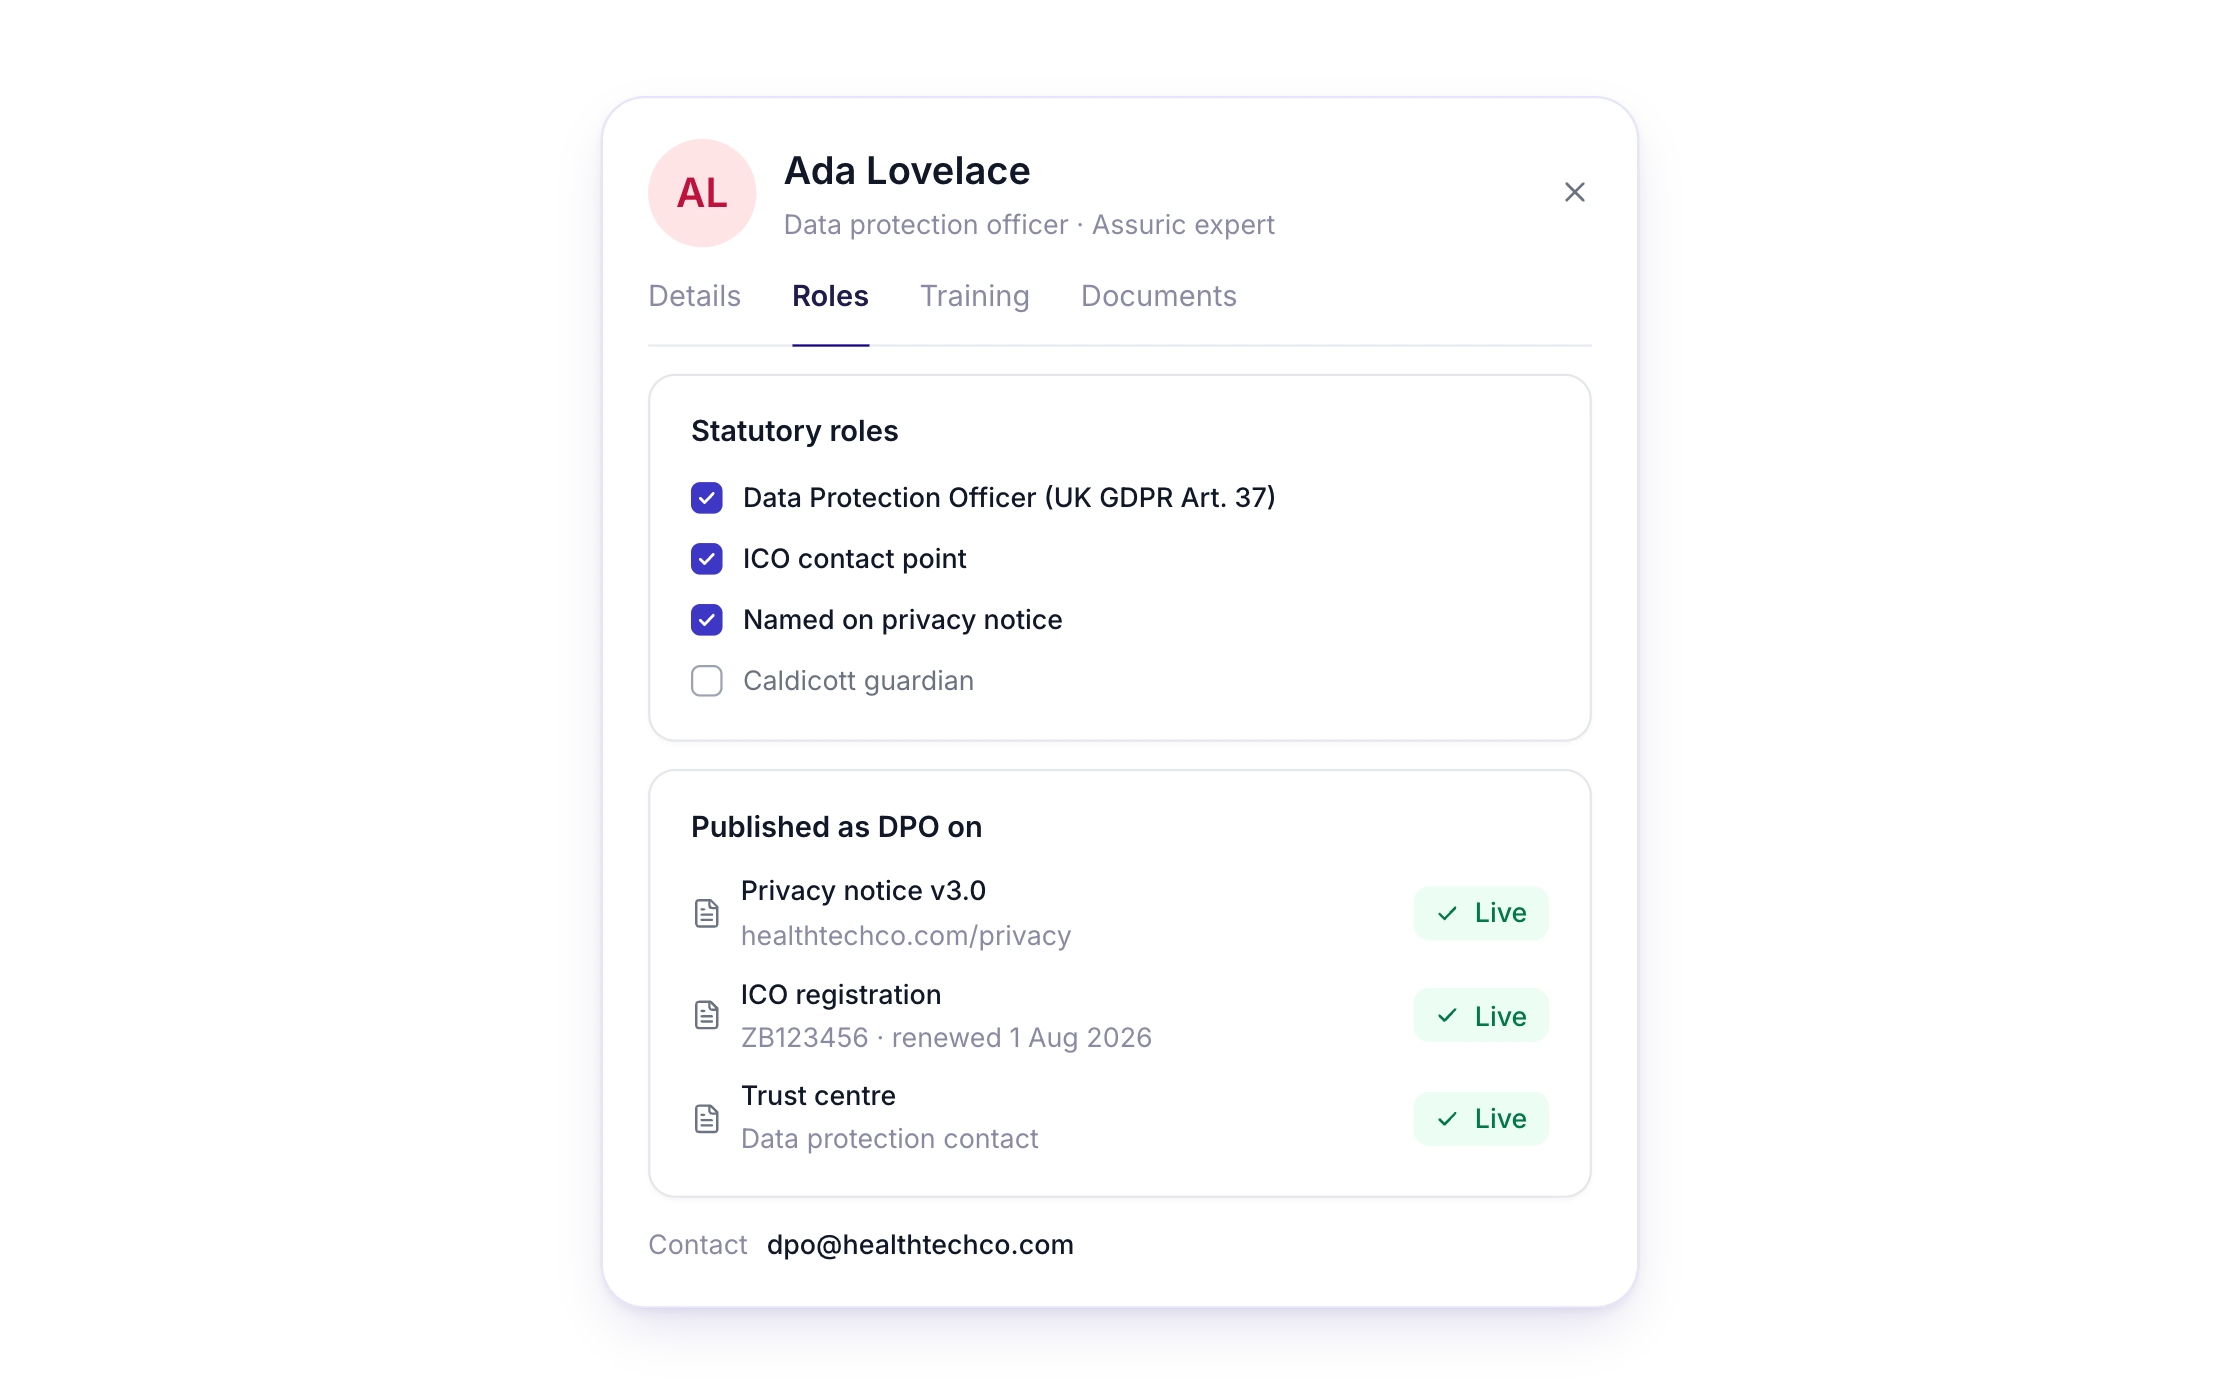
Named data protection officer assigned to the workspace

Fractional DPO

Get expert data protection support

Access experienced healthcare data protection expertise to help with DPIAs, documentation and ongoing compliance, without hiring a full-time DPO.

Explore
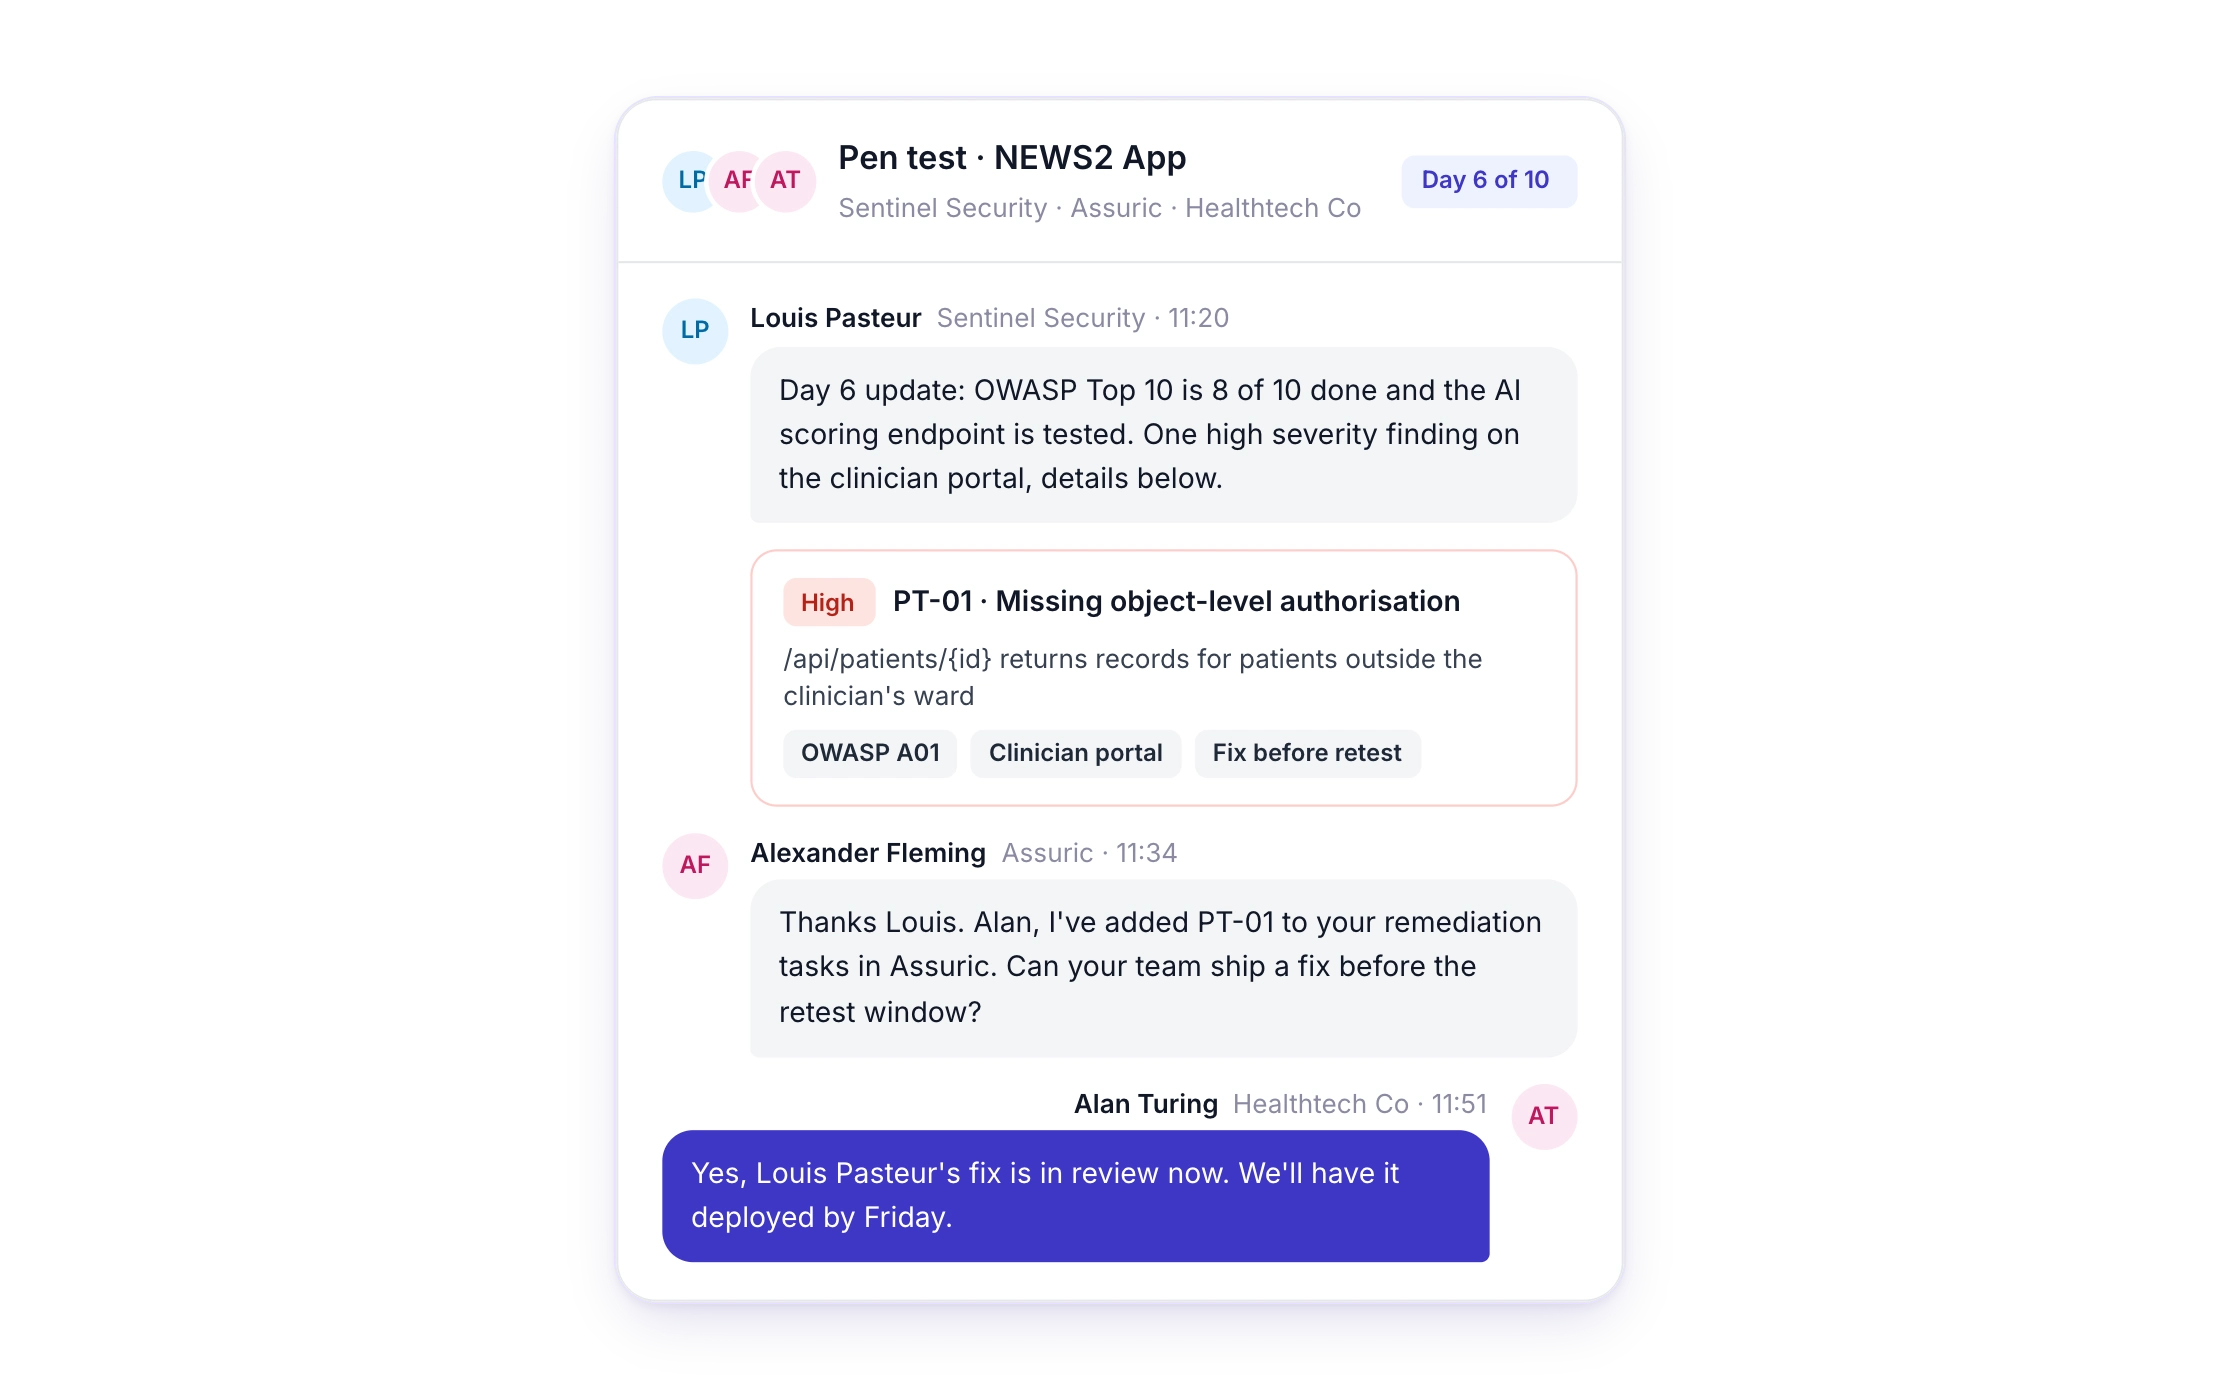
Penetration test findings and vulnerabilities tracked through to retest

Penetration testing

Find security weaknesses before someone else does

Work with CREST-accredited testers experienced in digital health. Receive a report outlining findings and recommended fixes, with retesting included.

Explore
Trust Centre access requests from buyers, approved in one place

Trust Centre

Give customers the evidence they ask for

Share security and compliance documents with NHS buyers, customers and partners through your own Trust Centre. Make due diligence easier without searching for and emailing individual documents.

Explore

Frameworks

Meet multiple requirements without repeating the work

Manage overlapping requirements across data protection and information security in one platform. Assuric maps shared controls and evidence across frameworks, helping you complete assessments with less duplication.

Trusted by healthtech teams

VitVio

“We couldn't speak highly enough of both the Assuric team and the platform itself, which is incredibly easy to use, and with the skill and hardworking nature of the Assuric team. They've been a key component in accelerating our progress and deployments!”

Maks Kozarzewski

COO, VitVio

Accenture

“The Assuric platform is a game changer in the clinical risk management field. It has been carefully designed to make the job of a CSO significantly more streamlined. The team are excellent and responsive to any product suggestions I have requested, and it has been a pleasure to work with them.”

Paul Llewellyn

CCIO, Accenture

Tandem Health

“Assuric has been fantastic in helping us quickly and safely navigate regulatory compliance in the UK. From completing Cybersecurity requirements to DSPT, DCB0129, and DTAC, the team was supportive, extremely knowledgeable, and the platform made everything quick and straightforward. A separate regulatory company we consulted at the beginning even remarked on how quickly we achieved compliance!”

Katie Baker

Director UK & Ireland, Tandem

Frequently asked questions

UK GDPR, alongside the Data Protection Act 2018, is the law that applies to any organisation processing personal data in the UK. The Data Security and Protection Toolkit (DSPT) is the NHS England self-assessment that organisations with access to NHS patient data and systems must complete every year, by the 30 June deadline, to show they meet the National Data Guardian’s data security standards. Much of the evidence overlaps, so Assuric maps it once and reuses it for both.

Under UK GDPR, you must appoint a Data Protection Officer if your core activities involve processing special category data, such as health data, on a large scale, or the regular and systematic monitoring of people on a large scale. Many healthtech companies meet that test, and NHS buyers and the DSPT will ask who your DPO is. Our fractional DPO service gives you an experienced, named DPO without a full-time hire.

UK GDPR requires a Data Protection Impact Assessment before any processing that is likely to result in a high risk to people’s rights and freedoms. The ICO lists examples such as large-scale processing of health data and the use of innovative technology, so most digital health products need one, and NHS organisations will usually ask to see it. Assuric drafts DPIAs from the information already in your workspace and tracks them through review and approval.

A RoPA is the record UK GDPR requires of how you process personal data: the purposes, the categories of data and people involved, who you share it with, any international transfers, how long you keep it and how you protect it. Organisations with fewer than 250 employees are exempt only when their processing is occasional, low risk and doesn’t include special category data, so if you process health data you need one. In Assuric, your RoPA links to your suppliers, systems and DPIAs, so it stays current as things change.

Cyber Essentials is the UK government-backed scheme covering five technical controls: firewalls, secure configuration, user access control, malware protection and security update management. NHS buyers ask for it, and it is part of DTAC. ISO 27001 is a broader, internationally recognised standard for running an information security management system, which larger NHS, enterprise and international customers often expect. Many teams start with Cyber Essentials and move to ISO 27001 as they grow, and Assuric reuses the same evidence across both.

At least once a year, and again after any significant change to your product or infrastructure. NHS buyers commonly expect a test from within the last 12 months as part of their assurance checks. Our penetration testing service uses CREST-accredited testers experienced in digital health, with retesting included.

Yes. Every DSPT assertion has its evidence attached and an owner named, with reminders well before the 30 June deadline, so your annual submission is a review of work you have already done. Evidence you hold for UK GDPR, ISO 27001 and Cyber Essentials counts towards the DSPT too, and our Data Protection Officers can review your submission before you publish it.

Pass every security review
with confidence

See how Assuric keeps your data protection and security evidence in one place, ready for every buyer and audit.